Mistakes Made Integrating Security Scanning into CI/CD
Explore common pitfalls and solutions for integrating security scanning into CI/CD pipelines, learning from real-world experiences and best practices.
You Might Still Need Patches for Denim
Explore container patch management strategies, including image registry maintenance, continuous deployment, and Google's approach to critical vulnerability patching without downtime.
Pensieve - Finding Malicious Artifacts in Container Environments
Explore techniques for forensic investigation in container environments, focusing on evidence retention and artifact gathering to understand adversarial activities.
A Case Study of MacOS Supply Chain Compromise
Explore MacOS supply chain vulnerabilities and learn proactive defense strategies using open-source tools for threat detection and malware identification in network environments.
From Cockroaches to Marble Floors - What Happens When You Turn On the Lights?
Practical tools and methodologies to transform software security posture by eliminating false distinctions between security bugs and other defects, improving product quality and aligning teams.
All Your Containers Are Belong to Us
Explore container orchestration security risks, focusing on exposed management nodes and APIs. Learn implications, recommendations, and see demonstrations of potential exploits in popular platforms.
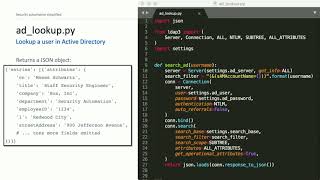
Security Automation Simplified
Practical guide to implementing security automation using existing tools and basic coding, demonstrating how to streamline SecOps processes and save time without relying on expensive products.
How to Lose a Container in 10 Minutes
Explore container security challenges, common deployment mistakes, and real-time vulnerabilities in cloud environments with practical examples and live demonstrations.
Checking Your --privileged Container
Explore container security, focusing on privileged containers, capabilities, and security contracts. Learn practical demos and admission controller techniques for enhanced protection.
Security Learns to Sprint - DevSecOps
Explore strategies for integrating security into DevOps, focusing on the "Three Ways" and providing actionable steps for immediate implementation in your organization.
Purple is the New Black - Modern Approaches to Application Security
Explore modern application security approaches combining defense, offense, automation, and continuous learning for various app types, including zero trust, supply chain, and microservices.
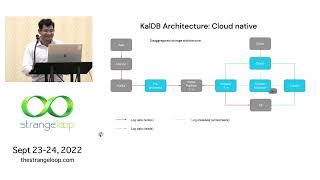
KalDB - A Cloud Native Log Search Platform
Explore KalDB, a cloud-native log search platform addressing Elasticsearch limitations. Learn about its architecture, real-time visibility, automatic field conflict handling, and cost-saving techniques.
With Friends Like eBPF, Who Needs Enemies?
Explore eBPF's evolution from network monitoring to a powerful Linux kernel observability tool, its security implications, and potential misuse by attackers.
Container Attack Surface Reduction Beyond Name Space Isolation
Explore techniques to reduce container vulnerabilities by analyzing and removing unnecessary dependencies, binaries, and permissions, enhancing security beyond namespace isolation.
An Attacker Looks at Docker - Approaching Multi-Container Applications
Explore containerization's impact on offensive security operations, focusing on Docker's implications for penetration testing and multi-container application vulnerabilities.
Vulnerability Exploitation in Docker Container Environments
Explore Docker container vulnerabilities, exploitation techniques, and security risks. Learn about cgroups, namespaces, and mitigation strategies for protecting critical data in containerized environments.
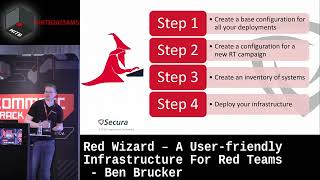
Red Wizard – A User-friendly Infrastructure For Red Teams
Introducing Red Wizard: An open-source tool for automated, OPSEC-safe Red Team infrastructure deployment. Streamlines setup with user-friendly wizards, self-documentation, and resilient architecture for efficient cybersecurity testing.
Securing Fast and Furious DevOps Pipelines
Learn strategies to secure DevOps pipelines without compromising speed, focusing on integrating security measures seamlessly into fast-paced development workflows.
Cloud Keep - Protect Your Secrets at Scale
Explore Cloud Keep, an open-source key management solution for secure data protection in cloud environments. Learn about its architecture, implementation, and future plans for enhancing cloud security.
Vulnerability and Threat Management - How Can We Close the Gaps
Explore strategies to enhance vulnerability and threat management through DevOps, Visible Ops, and improved application development, configuration, and operations processes.
Streamlining Mobile Releases
Discover strategies for efficient, reliable mobile app releases. Learn automation techniques to minimize errors, improve user experience, and maintain high app store ratings.