Cloning a Game Using Game Hacking and Terabytes of Data
Explore game hacking techniques and data analysis to clone games, with insights on leveraging large datasets for reverse engineering and replication.
Go with the Flow - Get Started with Flow Analysis Quickly and Cheaply
Learn flow data analysis techniques using Silk, from collection to visualization. Explore advantages over PCAP, query building, and automation for efficient network traffic insights.
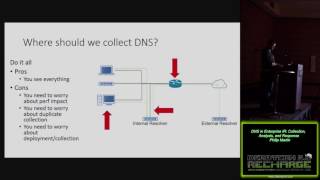
DNS in Enterprise IR Collection Analysis and Response
Explore DNS logging techniques for enterprise incident response, covering data collection, analysis, and response strategies to enhance network security and threat detection.
Garbage in Garbage Out - Generating Useful Log Data in Complex Environments
Explore effective log data generation in complex environments, focusing on meaningful data, thresholds, and log management systems for improved security and analysis.
Intro to WireShark
Comprehensive introduction to Wireshark network protocol analyzer, covering packet capture, filtering, and analysis techniques for effective network troubleshooting and security monitoring.
Mobile Forensics - An Introduction
Explore mobile device forensics techniques, evidence collection, and analysis methods for criminal investigations and digital security.
Private Matters
Explore privacy concerns in the digital age, focusing on personal data protection, online security, and strategies to safeguard your digital footprint.
Technological Changes that Affect Forensic Investigations
Explore technological advancements impacting forensic investigations, from IoT and connected cars to biometrics and big data, addressing challenges and opportunities in digital evidence collection.
Abstract Tools for Effective Threat Hunting
Learn effective threat hunting techniques using abstract tools, investigative processes, and data-driven observations. Develop expertise in pivoting, aggregation, and creating a knowledge base for cybersecurity investigations.
Chunky Cookies - Smashing Application Aware Defenses
Explore application-aware defense bypassing techniques, including data chunking, encryption, and reassembly methods for network traffic manipulation and evasion.
Weaponizing Splunk - Using Blue Teams for Evil
Explore how attackers can exploit Splunk for malicious purposes, including data extraction and command control, in this eye-opening cybersecurity presentation.
Arming Small Security Programs - Network Baseline - Matt Domko
Learn to establish network baselines for small security programs, covering malware detection, logging, and traffic analysis using tools like Bro and Security Onion.
Homebrew PowerShell - Where to Begin with Data Sources and Baseline Data
Learn to leverage PowerShell for data analysis, exploring essential data sources and establishing baseline metrics for effective cybersecurity monitoring and threat detection.
Detecting DNS Anomalies with Statistics
Explore statistical methods for detecting DNS anomalies, including letter analysis, unique queries, and outlier identification. Learn practical tools and techniques for enhancing network security.
Changing Our Future with 3D Printing
Explore 3D printing's transformative potential in manufacturing, economics, and society, from industrial revolution to sustainability and equality.
Big Data's Big Problems
Explore the challenges and implications of big data, from digital exhaust to algorithmic transparency, and its impact on human interests and destiny.
Getting Back to the Old School
Explore old-school cybersecurity techniques, emphasizing manual analysis, critical thinking, and foundational skills to complement modern tools and stay ahead of evolving threats.
Quantifying Security's Value - It Can Be Done
Explore methods to quantify security's value through ROI equations, scenario analysis, and expert models. Learn to effectively communicate security's importance to stakeholders.
Measuring Cyber Risk with Open FAIR
Explore cyber risk measurement using Open FAIR, covering qualitative and quantitative analysis, threat event frequency, and scenario-based approaches for effective cybersecurity leadership.
Data Mining Wireless Survey Data with ELK
Explore data mining techniques for wireless survey data using ELK stack, enhancing network analysis and security insights.
Regular Expressions Regex Overview
Learn to harness the power of regular expressions for efficient text pattern matching and data extraction. Explore syntax, quantifiers, capture groups, and practical applications in threat intelligence.