Stopping Cyber Criminals During a Pandemic
Explore how cyber criminals exploit COVID-19 fears, learn about the Cyber Threat Intelligence League's global efforts to combat attacks, and discover strategies for enhancing cybersecurity during the pandemic.
Acing the IOC Game - Toward Automatic Discovery and Analysis of Open-Source Cyber Threat Intelligence
Explore automatic discovery and analysis of open-source cyber threat intelligence, focusing on IOC generation, correlation analysis, and impact on security.
Mitigating Russian State-Sponsored Cyber Threats to US Critical Infrastructure
Explore Russian state-sponsored cyber threats to US critical infrastructure, learn mitigation strategies, and understand FBI resources for enhancing cybersecurity preparedness.
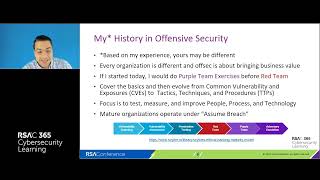
Intro to Purple Team - Cyber Threat Intelligence, Attack, Detect, Respond
Learn to build an effective Purple Team program, covering threat intelligence, attack emulation, and detection engineering using MITRE ATT&CK as a common language for improved cybersecurity.
Introduction to STIX - TAXII 2 Standards
Comprehensive overview of STIX/TAXII 2 standards for Cyber Threat Intelligence, covering key concepts, data models, and interoperability challenges in threat intelligence sharing.
What is Cyber Threat Intelligence
Discover cyber threat intelligence essentials, including analyst skills, frameworks, daily tasks, and maintaining anonymity. Learn to put intelligence into action for effective cybersecurity.
24-7 CTI - Operationalizing Cyber Threat Intelligence
Operationalizing 24/7 cyber threat intelligence: techniques, training methodologies, and lessons learned for leveraging SOC Analysts, implementing with existing tools, budget, and experience.
Nomadic Honeypots - How To Create Actionable CTI
Explore Automated Moving Target Defense using nomadic honeypots to create actionable Cyber Threat Intelligence. Learn deception techniques, attacker behaviors, and how to reduce attack surfaces while generating valuable threat insights.
Tracking Prey in the Cyberforest
Explore advanced techniques for tracking and analyzing cyber threats in complex network environments, enhancing your ability to detect and respond to sophisticated attacks.
The Expanding Universe of Cyber Threats
Explore cyber threat intelligence as a solution for managing the rapidly expanding threat landscape, prioritizing threats, and providing actionable insights to decision-makers in enterprise security.
Learning How to Smurf with Honeypots
Explore how honeypots can enhance blue team skills, covering topics like Cyber Threat Intelligence, DevSecOps, and Attack Modeling to improve cybersecurity operations.
Facebook - The Deep & Dark Web For Threat Actors In Asia
Exploring Facebook's role as a platform for cyber criminals and hacktivists in Asia, examining its similarities to the dark web and its appeal for organizing illicit activities.
Industroyer - Crashoverride - Zero Things Cool About a Threat Group Targeting the Power Grid
Análisis detallado del malware Industroyer utilizado en el ciberataque a la red eléctrica de Ucrania en 2016, sus capacidades y el grupo de amenazas detrás del ataque.
Understanding the Cybersecurity Act of 2015
Explore the Cybersecurity Act of 2015, its impact on information sharing, privacy concerns, and legal implications in this comprehensive analysis by Jeff Kosseff.
Hunting the Shadows - In Depth Analysis of Escalated APT Attacks
In-depth analysis of APT attacks targeting Taiwan, showcasing automated detection systems, forensic techniques, and insights into attacker operations. Includes release of collaborative APT classification platform.
Evaluating Commercial Cyber Threat Intelligence
Explore methods for assessing and leveraging commercial cyber threat intelligence to enhance organizational security posture and decision-making processes.
The Value of Design in Cyber Threat Intelligence
Explore design principles in cyber threat intelligence, enhancing communication and impact of intelligence products through visual and written techniques.
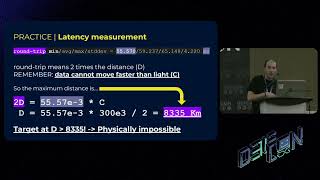
Finding Foes and Yourself with Latency Trilateration
Discover how latency trilateration can revolutionize cyber threat intelligence by geolocating adversary servers through network signal timing measurements and physical principles.
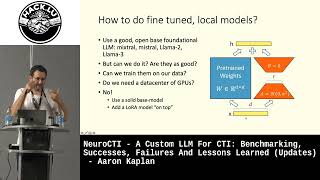
NeuroCTI - A Custom Large Language Model for Cyber Threat Intelligence: Benchmarking, Successes, Failures and Lessons Learned
Explore the development journey of a specialized LLM for Cyber Threat Intelligence, including key benchmarks, outcomes, and critical insights from real-world implementation.
Automating Dark Web CTI Reports with RAG Insight for MISP Sharing
Discover how to automate Cyber Threat Intelligence reports from the dark web using RAG Insight, enabling efficient MISP sharing and enhanced threat detection capabilities.
You Just Got a CTI Program Funded - Now What?
Discover essential strategies and practical steps for successfully implementing a newly funded Cyber Threat Intelligence (CTI) program, from resource allocation to measuring effectiveness.