Transparency in the Software Supply Chain - Making SBOM a Reality
Explore the concept of Software Bill of Materials (SBOM) and its potential to enhance transparency in the software supply chain, discussing benefits, challenges, and implementation strategies.
Testing Your Organization's Social Media Awareness
Explore automated social media intelligence gathering techniques to identify potential targets within organizations and learn strategies for enhancing social media awareness and protection.
Attacking Electric Motors for Fun and Profit
Explore electric motor vulnerabilities and attacks bridging cyber and physical realms. Learn about security risks, attack methods, and protective measures for this critical technology.
Practical Approach to Automate the Discovery and Eradication of Open-Source Software Vulnerabilities
Discover and eradicate open-source vulnerabilities in web applications at scale. Learn Netflix's pragmatic approach to identifying risks, triaging vulnerabilities, and implementing effective remediation strategies.
Attacking and Defending Blockchains - From Horror Stories to Secure Wallets
Explore blockchain security failures and risk mitigation strategies. Learn about wallet types, exchange vulnerabilities, and notable blockchain bugs to enhance your understanding of cryptocurrency protection.
What Cybersecurity Practitioners Can Learn from Honeybees
Explore the fascinating parallels between honeybee colonies and cybersecurity organizations, learning valuable insights for threat detection, risk assessment, and organizational structure.
Remember When We Used to Call It "Information Security"? Let's Go Back to That
Experts discuss shifting focus back to information security, exploring advancements in identity management and encryption to better protect data in an interconnected world.
The Return of Hacktivism - The Insider
Explore how evolving work dynamics and employee mindsets fuel insider hacktivism, impacting corporate data security. Real-world examples illustrate this emerging threat and its implications.
The Rise of the BISO Role
Explore the emerging BISO role, its importance in bridging security and business, and strategies for integrating security across all organizational levels.
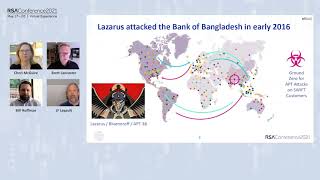
Reducing Payment Fraud with SWIFT Customer Security Controls Framework
Explore SWIFT's Customer Security Program: its impact on reducing payment fraud, enhancing cyber hygiene, and evolving to meet future challenges in the global financial ecosystem.
Cyber Insurance - What Makes a Good Fit for You
Explore cybersecurity insurance essentials, including policy components, data elements for risk assessment, and key security controls. Learn to determine appropriate coverage and understand industry standards.
Bug Bounty Programs - Crowd Sourcing Security
Explore Mozilla's bug bounty program, its history, benefits, and challenges. Learn how to implement similar programs and their advantages over black market alternatives.
The Shuttle Columbia Disaster - Lessons That Were Not Learned
Explore the Columbia disaster's overlooked lessons, examining communication failures, risk management, and organizational issues that led to the tragedy and persist in modern organizations.
Surviving the Modern Compliance Minefield
Navigate the complex landscape of modern compliance with insights on legal actions, data protection, and evolving standards for cybersecurity professionals and organizations.
Does DoD Level Security Work in the Real World
Exploring DoD-level security's real-world effectiveness, risk parameters, and building a culture of security through a comprehensive lifecycle approach.
A Day in the Life of a Security Analyst
Explore a day in the life of security analysts, covering key aspects like governance, compliance, data access, and security controls implementation.
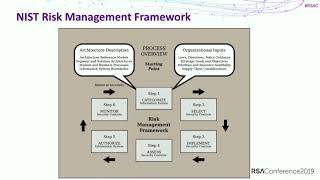
Math Is Hard - Compliance to Continuous Risk Management
Explore strategies for implementing continuous risk management, from gaining management buy-in to selecting metrics and reporting at various organizational levels. Learn quantitative risk analysis methods and practical implementation tips.
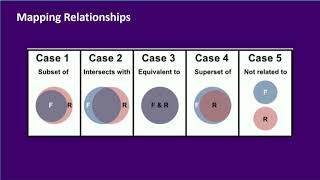
NIST Cybersecurity Framework and PCI DSS
Explore the mapping between NIST Cybersecurity Framework and PCI DSS, understanding similarities, relationships, and benefits for compliance across multiple standards.
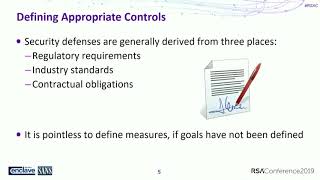
Developing Key Performance Indicators for Security
Learn practical steps to create meaningful key performance indicators for cybersecurity, choose appropriate standards and tools, and effectively communicate risk posture to leadership for improved organizational defense.
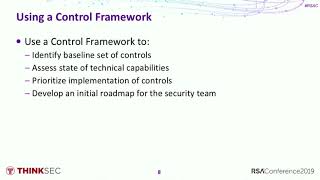
How to Make Sense of Cybersecurity Frameworks
Explore cybersecurity frameworks, their organization, and effective implementation. Learn to simplify complex security concepts and build stronger programs with insights from a CISO.
The Future of Privacy
Explore the evolving privacy landscape, its impact on technology, and future implications. Gain insights on balancing compliance and innovation in this rapidly changing field.