IPv6 First Hop Security in Virtualized Environments
Explore IPv6 first hop security challenges and solutions in virtualized environments, focusing on potential vulnerabilities and effective mitigation strategies.
Unpatchable
Explore hardware vulnerabilities in Apple devices, focusing on the M1 chip's security features and potential exploits. Gain insights into cutting-edge research on device security.
Biohacker - The Invisible Threat
Explore the emerging threat of biohackers with surgically implanted offensive security tools. Learn about this unique cybersecurity challenge and strategies to address augmented humans in your environment.
The Insecure Software Development Lifecycle - How to Find, Fix, and Manage Deficiencies Within an Existing Methodology
Practical techniques for integrating security into existing software development methodologies, addressing deficiencies, and ensuring compliance throughout the SDLC.
Injecting Security into Web Apps
Explore innovative approaches to web application security beyond traditional WAFs, focusing on internal application monitoring and real-time threat detection to prevent zero-day attacks and data exfiltration.
Social Engineering - Setting People into Debug Mode
Explore social engineering tactics and their impact on corporate security, drawing insights from real-world hacks and competition experiences to understand vulnerabilities beyond technological solutions.
Bypassing the Android Permission Model
Explore techniques to bypass Android's permission model, including exploiting insecure storage and interfaces. Learn about security risks and mitigation strategies for developers and users.
Mostrame la Guita! Adventures In Buying Vulnerabilities
Explora las complejidades y desafíos del mercado de vulnerabilidades de seguridad, analizando estrategias de compra, valoración y negociación en este fascinante sector.
Gestionar y responder a incidentes de CyberSec sin morir en el intento
Aprende estrategias efectivas para gestionar y responder a incidentes de ciberseguridad. Descubre técnicas prácticas para mantener la calma y eficacia en situaciones críticas, presentadas por un experto en seguridad informática.
How to Measure the Security of Your Network Protection Devices
Explore methods to quantify network security device performance, efficacy, and risk. Learn to assess defensive appliances for better security design and network protection strategies.
So You Think You Can Patch - The Game Show that Questions Your Security Assumptions
Explore the complexities of security patching through a game show format. Experts discuss challenges, policies, and solutions for effective patch management in modern enterprises.
Handling a Bug Bounty Program from a Blue Team Perspective
Strategies for blue teams to manage bug bounty programs effectively, balancing security needs with researcher experience. Focuses on mitigating operational risks and optimizing defense rules for real threats.
Implementing a Harmonized Shipping Label Generator
Explore the implementation of harmonized shipping labels in the EU, addressing challenges and proposing solutions for this new regulatory requirement.
Cloud Security and Compliance
Comprehensive review of cloud computing security risks, mitigation strategies, and compliance considerations for organizations adopting cloud-based services.
Artificial Intelligence Security and Privacy - Legal Threats and Opportunity
Explore AI's impact on privacy, security, and legal landscapes. Learn about potential risks, opportunities, and efforts to preserve AI integrity from industry experts.
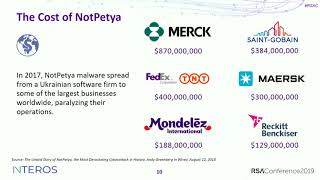
The Power of Ecosystems - A Look Under the Supply-Chain Covers
Explore supply-chain complexities, third-party risks, and nation-state threats in digital ecosystems. Learn to rethink CTI and risk management for today's interconnected business landscape.
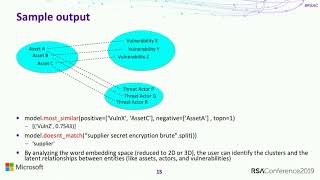
Machine Learning Toolbox for Cybersecurity Risk Management
Explore machine learning techniques for cybersecurity risk assessment, including topic modeling, word embedding, and PCA. Learn to identify unknown risks and profile incidents effectively.
Using Automation to Help Achieve Security in a Multicloud Environment
Explore strategies for automating security in multicloud environments, focusing on critical components, tools, and data utilization to enhance operational security and inform decision-makers.
Moving Security from Cost Center to Revenue Generator
Discover strategies to transform security from a cost center to a revenue generator by communicating its value in financial terms and highlighting revenue enabled by effective security measures.

Hacking the Law - Are Bug Bounties a True Safe Harbor?
Explore the legal risks and challenges of bug bounty programs, examining potential liabilities for hackers and suggesting steps to create safer legal environments for vulnerability disclosure.
Sharks in the Water - Open Source Component Risk and Mitigation
Explore open source component risks and mitigation strategies, focusing on supply chain vulnerabilities, recent hacks, and preventive measures through education and automated tooling.