Tackling Software Supply Chain Security as an Organization - Episode 128
Explore organizational approaches to software supply chain security with experts discussing solutions, initiatives, and best practices for managing risks and improving visibility.
Software Supply Chain Security: Definition and Importance - Episode 1
Explore the key pillars of software supply chain security in this comprehensive podcast episode. Gain insights into problem definition, essential terms, and practical implementation strategies for enhancing your organization's security posture.
The Depth of Cyber Hygiene: Eliminating Reactive Approaches
Explore layers of cybersecurity, from solutions to human elements. Interact with attendees, review recent cyberattacks, and learn prevention strategies from an experienced expert.
Protecting Small Businesses from Cyber Attacks - Strategies and Real-World Scenarios
Explore attacker strategies, real-world scenarios, and cost-effective measures to protect small businesses from cyber threats. Learn to engage employees through gamification for enhanced security.
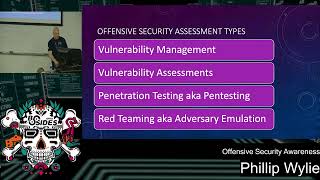
Offensive Security Awareness: Understanding Assessment Types and Methodologies
Demystify offensive security techniques, tools, and assessment types. Gain insights into vulnerability management strategies and learn to choose the right approach for your organization's security needs.
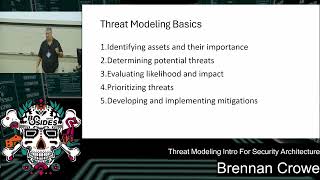
Threat Modeling Introduction for Security Architecture
Aprende a integrar el modelado de amenazas en revisiones anuales de gobernanza y arquitectura de seguridad. Explora conceptos clave como vectores de ataque, superficies de ataque y ciclos de vida de ataques.
The Fault in Our Metrics: Rethinking How We Measure Detection and Response
Rethink detection and response metrics with a practical framework, new maturity model, and visual examples. Learn to measure capabilities effectively and tell a compelling story using micro-purple testing techniques.
DCMS' Approach to Software Security and Resilience Policy
Explore DCMS' approach to software security and resilience policy with insights from Naomi Gilbert, Head of Cyber Resilience Policy at the Department of Culture Media & Sport.
The Iceberg - How to Mitigate Risks in Your OSS Projects
Explore strategies to mitigate risks in open-source software projects and understand the expanding attack surface in modern development environments.
Open Source Supply Chain Security for Enterprises
Explore enterprise-level open source supply chain security strategies with insights from JPMorgan Chase's Product Security Director.
The Myriad Paths to Improving Open Source Security
Explore diverse approaches to enhance open source security with expert insights from Rory McCune at SOOCon23 Security.
Do You Know the Health of Your OSS Dependencies? Introducing OSSF Scorecard API
Explore the OSSF Scorecard API to assess and improve the health of your open-source software dependencies, enhancing overall security.
Modelling Threats Out in the Open Source - SOOCon23 Security
Explore open-source threat modeling techniques to enhance software security and identify potential vulnerabilities in your projects.
Financial Institutions Net-Zero Standard Overview
Explore the Financial Institution Net-Zero Standard draft, its key components, and how to contribute to its finalization.
Let Devs Be Devs Without Sacrificing Security
Explore flexible, secure CI pipelines using Tekton, Chains, and Enterprise Contract to balance developer innovation with robust security measures for various software targets.
Exploring a Risk Approach to Software Supply Chain Security
Explore software supply chain security through a risk-based approach, focusing on open source vulnerabilities and process improvements to mitigate supplier risks.
Rules of Engagement for Forking a Dependency
Explore guidelines for forking dependencies when facing security vulnerabilities, balancing community responsibility with timely fixes.
Desmoplakin Cardiomyopathy: Understanding DSP-Type ARVC
Explore groundbreaking research on DSP cardiomyopathy, including risk factors, patient involvement, and future goals for improved understanding and treatment.

Can LLMs Keep a Secret? Testing Privacy Implications of Language Models
Explore privacy risks of interactive LLMs, examining evaluation frameworks and proposing research directions for improved privacy auditing and mitigation strategies.
Development of Asset Mapping External Attack Tool
Explore an in-house tool for unified asset visibility, vulnerability mapping, and attack surface analysis in complex multi-cloud environments, tailored for Red Hat standards.
Evolution of Cooperative Problem Solving in an Artificial Economy
Explore the flaws in rational actor models and their real-world implications in artificial economies through cooperative problem-solving evolution.