Managing Vulnerabilities in Open-Source Dependencies
Learn strategies to secure open-source dependencies, evaluate software composition analysis tools, and shift from reactive to proactive security postures in product development.
The Ripple Effect: Measuring Impact Beyond Numbers
Explore sustainable change through social impact initiatives, focusing on high-impact communication campaigns and fostering a culture of giving for lasting societal transformation.
Hunting Down the Monsters Hidden in Your Software Supply Chain
Uncover and mitigate hidden threats in your software supply chain. Learn effective strategies to enhance security and protect against vulnerabilities.
Looking at Security with Cat Eyes - The OpenKAT Project
Explore integrated security projects bridging technical checks, compliance, automated warnings, and non-repudiation in the OpenKAT initiative.
Security Keynote - Open Source Software and Cybersecurity
Explore cybersecurity insights and strategies with Dr. Allen Friedman's keynote address on critical security challenges and solutions in the digital landscape.
The Fault in Our Metrics - Rethinking How We Measure Detection and Response
Rethinking cybersecurity metrics: Learn to develop meaningful measurements for detection and response capabilities, avoiding pitfalls of traditional metrics and motivating teams effectively.
Building a Security Audit Logging System on a Shoestring Budget
Learn to build a robust, security-focused audit logging system for fast-growing companies with limited resources. Discover cost-effective strategies and lessons from combining software engineering and hacker culture.
Demystifying SBOMs: Strengthening Cybersecurity Defenses
Explore Software Bill of Materials (SBOMs) as a crucial tool for enhancing cybersecurity, identifying vulnerabilities, and managing software supply chain risks in organizations.
Effective Security on a Tight Budget
Discover strategies for maintaining robust security with limited resources, focusing on principles and practices to overcome budget constraints in challenging economic times.
PirOps - What 18th-Century Piracy Can Teach Us About SecOps
Explore historical pirate strategies and their surprising relevance to modern SecOps, drawing insights from 18th-century Caribbean piracy for today's security practices.
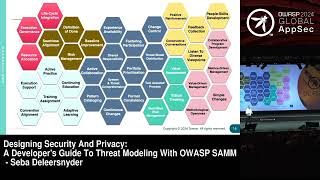
Designing Security and Privacy - A Developer's Guide to Threat Modeling with OWASP SAMM
Learn threat modeling techniques using OWASP SAMM to enhance security and privacy in software development, empowering developers to identify and mitigate potential risks effectively.
Managing Vulnerability Overload with OWASP Tools and Strategies
Discover OWASP's strategies for managing overwhelming security vulnerabilities, enhancing your ability to prioritize and address critical threats effectively.
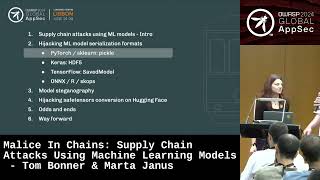
Malice in Chains - Supply Chain Attacks Using Machine Learning Models
Explore potential supply chain vulnerabilities in machine learning models and learn strategies to mitigate risks in AI-driven systems.
OWASP IoT Security Testing Guide (ISTG)
Comprehensive guide for IoT security testing, covering methodologies and best practices to identify vulnerabilities and enhance device protection in the interconnected world.
Paved Roads to Express RBAC in Threat Models
Learn effective techniques for incorporating Role-Based Access Control (RBAC) into threat modeling, enhancing security design and risk assessment for software systems.
Cryptographic Governance - Software Supply Chain Security with CBOM
Explore software supply chain security using Cryptographic Bill of Materials (CBOM) for enhanced governance and risk mitigation in development processes.
Modern Application Security vs. GenAI Applications: Is Your AppSec Ready?
Explore the intersection of modern application security and generative AI, assessing readiness for emerging challenges in the evolving tech landscape.
OWASP Dependency Track - Fortifying the Software Supply Chain
Explore strategies to secure software supply chains using OWASP Dependency Track, a powerful tool for identifying and mitigating vulnerabilities in third-party components.
5 AppSec Stories and What We Can Learn From Them
Explore real-world application security incidents and extract valuable lessons to enhance your cybersecurity practices and prevent similar vulnerabilities in your own systems.
Assessment of Violent Ideations - Psychiatry Project ECHO
Explore assessment techniques for violent ideations with Dr. Colleen Lillard, gaining insights into psychiatric evaluation and risk management strategies.
War Stories - Fighting Ransomware Operators
Insights into combating ransomware from a cybersecurity expert, sharing real-world experiences and strategies for incident response and threat mitigation.