Android and iPhone Risks and Solutions
Explore mobile security risks and effective solutions for Android and iPhone devices, enhancing your understanding of smartphone vulnerabilities and protection strategies.
Values-Based Leadership - Philanthropy and the Private Sector
Explore how Starbucks CEO Howard Schultz and his wife Sheri blend corporate leadership with philanthropy, focusing on initiatives for veterans and youth employment opportunities.
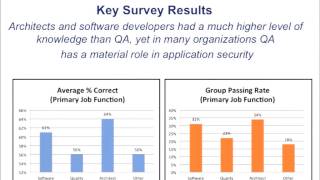
Can AppSec Training Really Make Developers Security-Smart?
Explore the effectiveness of AppSec training for developers through a year-long survey, revealing surprising insights on knowledge retention and practical application in software security programs.
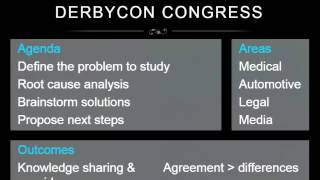
The Cavalry Is Us - Cybersecurity Activism in the Internet of Things Era
Exploring cybersecurity challenges in IoT and the need for collective action. Calls for researchers and professionals to shape the future of digital security and address emerging threats.
Intelligence-Led Cybersecurity - Balancing Global Operations, Risk, and Speed
Experts discuss global cybersecurity challenges, balancing risk and speed in intelligence-led operations, and the interplay between public and private sectors in addressing cyber threats.
Can AppSec Training Really Make a Smarter Developer?
Explores the effectiveness of AppSec training for developers through a year-long survey, revealing surprising insights on knowledge retention and its impact on application security strategies.
Seeing Around Corners - The Intelligence Professional's Challenge
Intelligence experts discuss strategies for anticipating and addressing unforeseen threats and challenges in national security, offering insights on navigating uncertainty in a complex global landscape.
Open Source in Safety Critical Applications
Explore the role of open source software in safety-critical systems with insights from Kate Stewart of The Linux Foundation.
Shift-Left to Address OS Vulnerabilities and Compliance for Cloud Native Applications
Inject security early in software development to address vulnerabilities before production, focusing on OS vulnerabilities and compliance for cloud-native apps.
How to Secure Your App With AppSweep
Learn to scan and secure your app against vulnerabilities using AppSweep, a powerful tool for identifying and addressing security issues in mobile applications.
Engineering Privacy and User Identity Protection from the Start
Discover essential guidelines for prioritizing privacy and user identity protection in project development, ensuring compliance with regulations and safeguarding sensitive information.
Revisiting Total Cost of Ownership for External Dependencies
Explore unaccounted risks of external dependencies in software development with Paul Vixie. Learn strategies to mitigate vulnerabilities and improve security practices in IoT and beyond.
Understanding the Impact of Critical Vulnerabilities in Critical Infrastructure: A Detective Story
Explore strategies for assessing and mitigating critical infrastructure vulnerabilities, focusing on novel threats and their potential ecosystem-wide impacts across various sectors.
VEXing Open Source Security - Vulnerability Data for Everything
Explore the Vulnerability Exchange Format (VEX) standard for improving vulnerability management in open source projects and enterprise software security.
Antitrust Laws and Open Technology Project Participation
Explore antitrust and competition law implications in open source collaborations, understanding risks and best practices for legal compliance in multi-company tech projects.
Composing the Ultimate SBOM - Creating Accurate and Modular Software Bill of Materials
Explore a modular approach to creating accurate Software Bills of Materials (SBOMs) using Micro-SBOMs, enhancing software security and compliance tracking beyond traditional post-build methods.
What's in a Name - Vulnerabilities, SBOMs, and the Challenge of Software Identity
Explore software identity challenges in supply chain security, examining existing naming standards, potential risks, and collaborative solutions for effective vulnerability management.
Securing Your Open Source Supply Chain
Explore software supply chain security threats and learn from SUSE's journey to secure open source codebases. Gain insights on certifications, processes, and tools for enhancing supply chain protection.
SBOMs: Essential for Embedded Systems
Explore the importance of Software Bill of Materials (SBOM) in embedded systems, regulatory expectations, and implementation in open source projects for improved cybersecurity and risk management.
Dynamic Scheduler Over FreeRTOS
Explore dynamic scheduling in FreeRTOS, covering design considerations, implementation components, and state machines. Learn to optimize real-time task management for embedded systems.
Dependencies: Do's and Don'ts - Managing Application Dependencies Securely
Learn best practices for managing dependencies in software development, balancing security risks with benefits to team velocity and business value. Discover preventive measures to minimize vulnerabilities.