Kubernetes Blue - Green Deployments in an Event Based Architecture
Explore challenges and solutions for implementing Blue/Green deployments in Kubernetes within an event-based architecture, focusing on CI/CD pipelines and risk mitigation strategies.
Why Building Your Ship with Raw Materials is a Bad Idea
Explore software bill of materials (SBOMs), open source compliance, and best practices for secure, robust application development in the face of new regulations and vulnerabilities.
How We Build and Mitigated Our Spring Boot Applications to Kotlin
Transforming Spring Boot from Java to Kotlin: strategies, improvements, and best practices for migrating large codebases, with live coding demonstrations and practical tips.
Supply Chain Security for OpenSource Projects
Explore supply chain security for open-source projects, covering potential threats, attack points, free tools, and strategies to protect against cyber attacks in software development.
Take Risks But Don't Be Stupid
Explore responsible risk-taking in DevOps through effective pre-production environments. Learn techniques for building powerful testbeds with minimal resources, balancing experimentation and efficiency.
Cloud Security Made for the EU - Securing Data & Applications
Explore confidential computing and real-time compliance for ultimate data security in EU cloud transitions. Learn key strategies to satisfy data protection regulations and address CISO concerns.
It's Not All Fun and Games - Cyber Threats to Professional Sports
Explore cybersecurity challenges in professional sports with CISOs from NBA, NFL, and NHL. Learn about threats, defense strategies, and collaboration with law enforcement.
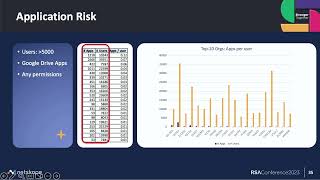
The Dark Underbelly of 3rd-Party Application Access to Corporate Data
Explore the hidden risks of third-party app access to corporate data, with real-world insights and practical strategies for prevention, detection, and risk mitigation in cloud environments.
Preparing for the New Era of Cybersecurity Disclosure
Explore new cybersecurity disclosure mandates and their impact on companies. Learn how transparency in reporting risks and incidents can benefit organizations and the marketplace.
Conducting a Pre-Mortem on the Next Zero Trust Breach
Explore future Zero Trust breaches through a pre-mortem analysis, examining potential vulnerabilities and attack vectors in 2028's cybersecurity landscape to enhance current defensive strategies.
Managing the Mobile Endpoint Attack Surface
Explore risk management for enterprise mobility, focusing on mobile threats and mitigation strategies. Learn from NCCoE's analysis of common mobile device security threats.
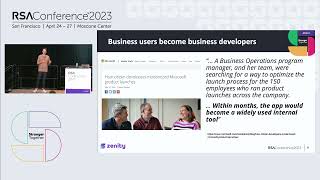
Credential Sharing as a Service - The Dark Side of No Code
Explore attack techniques exploiting low-code apps in enterprises, revealing vulnerabilities throughout the cyber kill chain and highlighting the security risks of non-IT app development.
Regulation and Risk When Your Customer's Browser Leaks Data
Explore data protection challenges in browsers, regulatory expectations, and strategies to manage risks associated with customer data leaks in web and mobile environments.
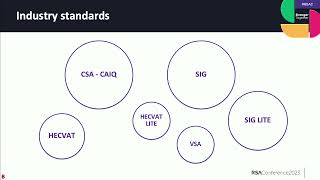
Your Third-Party Risk Management Program Is Bad and You Should Feel Bad
Challenging traditional approaches to third-party risk management, this talk inspires new strategies for security leaders to enhance effectiveness and resource allocation in risk assessment processes.
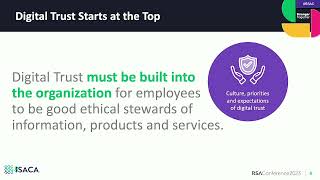
The Digital Trust Gap - How Cyber Pros Break Silos to Advance Digital Trust
Explore how cybersecurity professionals can collaborate across IT functions to strengthen digital trust, leveraging privacy, quality, risk management, and governance for enhanced enterprise and consumer confidence.
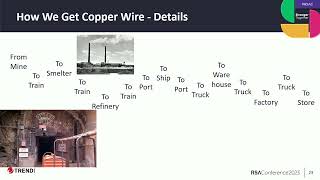
Responding to Supply Chain Vulnerabilities – A Maritime Perspective
Explore cybersecurity risks in ports and shipping, analyzing vulnerabilities and discussing potential solutions for improved detection and response in maritime infrastructure.
Better Risk Assessment for Cyber Insurance - How Will We Get There
Explore the challenges in cyber insurance risk assessment and learn about emerging solutions, including improved data points and continuous evaluation methods for more accurate coverage.
Cybersecurity in the Boardroom - The Impact of the Latest SEC Proposal
Explore the impact of SEC's cybersecurity expertise requirement for boards and learn how CISOs can prepare for potential board positions in public, private, and non-profit organizations.
4 Ways IoT Devices Are Creating Privacy Implications for Organizations
Explore IoT device privacy risks and learn strategies to identify and secure devices that handle confidential data, with insights from a principal solutions architect.
Data Privacy Concerns - A Risk Based Approach to De-Identification
Explore a comprehensive approach to data de-identification, covering risk scores, certification processes, and key business outcomes in response to new privacy regulations.

Code as Risk
Explore how code itself can be a source of risk in software development. Learn strategies to reduce vulnerabilities, improve security, and create more robust systems through better coding practices.