The Road to Compliancy Success Plus Plus
Explore strategies for achieving and maintaining compliance in information security, with insights on overcoming challenges and implementing effective practices.
Bad Advice - Unintended Consequences and Broken Paradigms - Think Act Different
Explore unconventional thinking in information security, challenging common practices and paradigms to develop more effective strategies and solutions for modern cybersecurity challenges.
Are You a Beefeater Focused on Protecting Your Crown Jewels
Explore strategies for safeguarding critical assets in cybersecurity, drawing parallels to the historic role of Beefeaters protecting the Crown Jewels.
All of Your Compliance Needs with One Methodology
Comprehensive methodology for streamlining compliance processes across multiple frameworks, enhancing efficiency and reducing redundancy in organizational security practices.
Adopting a Risk-Based Threat Model to Secure Your Defenses and Regain Control of Your Critical Data
Adopt a risk-based threat model to enhance defense strategies and regain control of critical data, improving overall security posture and resilience against cyber threats.
Exercising with Threat Models
Explore practical threat modeling techniques to enhance cybersecurity strategies and identify potential vulnerabilities in systems and networks.
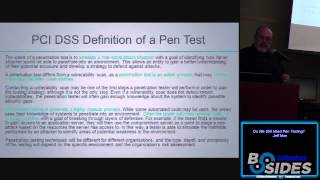
Do We Still Need Pen Testing - Jeff Mann
Explore the relevance and goals of penetration testing in modern cybersecurity, examining its effectiveness, methodologies, and evolving role in protecting digital assets.
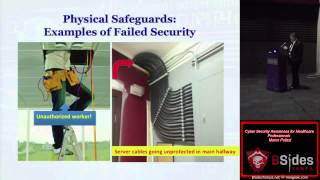
Cyber Security Awareness for Healthcare Professionals
Explore cybersecurity essentials for healthcare professionals, covering real-world incidents and best practices to protect sensitive patient data and medical systems.
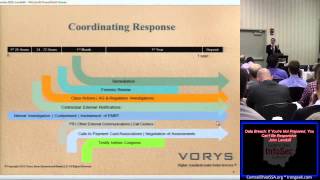
Data Breach - If You're Not Prepared, You Can't Be Responsive
Learn strategies for data breach prevention, mitigation, and response planning. Discover key steps for the first 24-70 hours post-breach, including internal communications, investigations, and remediation.
Presenting Security Metrics to the Board
Learn effective strategies for presenting security metrics to executive boards, focusing on clear communication, risk quantification, and tailoring your approach to board expectations.
Exploring the Relationship between Compliance and Risk Management
Explore the interconnection between compliance and risk management in information security, focusing on strategies to align regulatory requirements with effective risk mitigation practices.
Were At War - Why Aren't You Wearing A Helmet
Explore cybersecurity challenges and strategies in today's digital landscape, emphasizing the critical need for proactive defense measures and heightened awareness in information security.
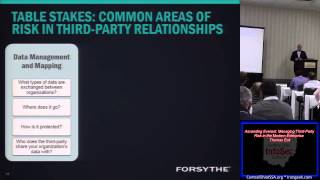
Ascending Everest - Managing Third Party Risk in the Modern Enterprise
Explore strategies for managing third-party risk in modern enterprises, drawing parallels with ascending Mount Everest to illustrate challenges and solutions in IT security.
Building an Industrial Controls Cybersecurity Framework - Critical Infrastructure
Explore building a cybersecurity framework for industrial controls in critical infrastructure, covering key concepts, standards, and executive orders.
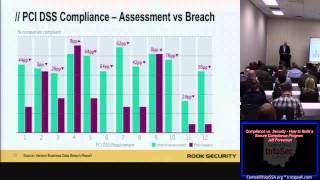
Compliance vs Security - How to Build a Secure Compliance Program
Explore building a secure compliance program, balancing regulatory requirements with effective security measures. Learn from real-world breaches and gain practical insights for program development.
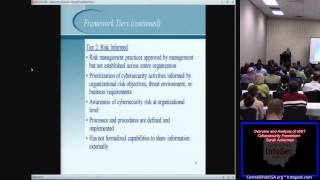
Overview and Analysis of NIST Cybersecurity Framework
Comprehensive analysis of the NIST Cybersecurity Framework, exploring its key components, implementation strategies, and practical applications for enhancing organizational security posture.
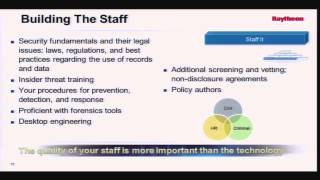
Building a Successful Insider Threat Program
Comprehensive guide to establishing an effective insider threat program, covering monitoring, strategy, documentation, and implementation for enhanced organizational security.
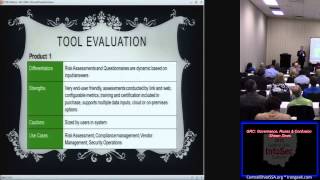
GRC Governance Ruses Confusion
Explore effective GRC governance strategies, avoiding common pitfalls and focusing on practical, business-aligned approaches for successful implementation and evaluation.
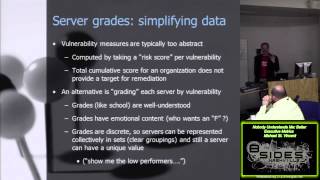
Nobody Understands Me Better - Executive Metrics
Explore effective metrics for communicating security insights to executives. Learn to present data visually, focus on business impact, and tell compelling stories that drive action and support.
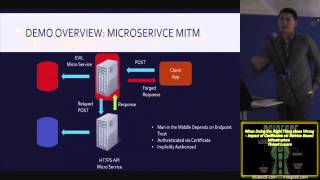
When Doing the Right Thing Goes Wrong - Impact of Certificates on Service Based Infrastructure
Explore the impact of certificates on service-based infrastructure, covering trust chains, implicit trust, and potential risks. Learn about certificate authorities and strategies for secure implementation.
Corporate Governance for Fun and Nonprofit
Explore non-profit governance essentials, including roles, responsibilities, and legal duties of officers and board members. Learn to navigate corporate structures effectively.