Docker Storage: Designing a Platform for Persistent Data
Learn to design and implement persistent storage solutions for Docker containers, enhancing data management and application reliability in containerized environments.
Enabling High Assurance and Sensitive Container Workloads with Encrypted Images
Explore encrypted container images to protect sensitive code and data, enforce security policies, and control execution environments for high-assurance workloads in enterprise settings.
Automating the DoD Container Hardening Pipeline
Explore DoD's automated container hardening pipeline, reducing vulnerabilities by up to 95% while maintaining functionality. Learn methodologies for instrumenting, testing, and optimizing containers to meet strict security standards.
Patterns That Protect - Securing Workloads in Automated Deployments
Learn strategies for securing external workloads in automated deployments, including vetting binaries, selecting providers, and utilizing open-source tools to enhance control and visibility.
Verifiable End-to-End Secure OCI Native Machines
Explore a secure toolchain for verifiable workloads using signed OCI images, ensuring tamper-proof boot processes and authenticated communication with hosts.
SecurityPerf - A New Open-Source Framework for Benchmarking Linux Security Solutions Performance
Explore SecurityPerf, an open-source framework for benchmarking Linux security solutions' performance impact. Learn about its containerized approach, supported services, and real-world applications.
Empathetic Approach to Containerized Deployments - Making Products Available for Everyone
Explore diverse containerized deployment approaches, from one-click solutions to customizable options, enhancing user adoption and product accessibility for various technical skill levels.
Design of an Open Source, Modular, 5G Capable, Container-based Scientific Data Capture Hexacopter
Explore the design of an open-source, modular hexacopter for scientific data capture, featuring 5G capability, container-based architecture, and versatile sensor integration for professional use.
A Checklist for Security from Container to Kubernetes - An End-to-End Overview
Comprehensive overview of container and Kubernetes security, covering lifecycle, supply chain, infrastructure, features, and potential attacks. Practical insights for robust cloud-native security implementation.
What We Learned Dissecting the World's Most Popular Containers
Explore insights from analyzing popular containers, covering size, complexity, package landscape, and security vulnerabilities to enhance container management and optimization strategies.
From Database in Container to DBaaS on Kubernetes
Explore the evolution of database deployment, from containerization to Database-as-a-Service on Kubernetes, with insights on best practices and industry trends.
Improving Container Security with System Call Interception
Explore advanced container security using system call interception, focusing on unprivileged containers, selective action monitoring, and practical applications in LXD.
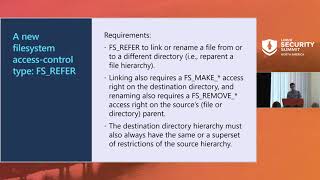
Landlock Update: File Reparenting and Network Rules Support
Explore Landlock's latest updates: file reparenting improvements and new network access controls for enhanced app and container security in Linux systems.
Enforcing a Secure Supply Chain on Kubernetes
Explore implementing and enforcing a secure supply chain in Kubernetes using open-source projects, including Sigstore keyless workflow and signature verification policies.
How We Built Ubuntu Distroless Containers
Explore the creation of Ubuntu distroless containers, understanding principles, benefits, and techniques for building secure, minimal-footprint images from scratch using standard tools.
Implementing Container Privilege Escalation Detection Using eBPF for Cloud Native Security
Explore eBPF-based techniques for detecting and preventing container privilege escalation in cloud environments, with practical implementation examples and real-world applications.

Vcluster - Creating Virtual Kubernetes Clusters Inside Kubernetes
Explore virtual Kubernetes clusters with vcluster: learn implementation, benefits, and applications for developers, testers, and DevOps specialists. Includes technical details and live demo.
Buildpacks+ - A Gradual Move to Cloud Native Image Builds
Explore AppsFlyer's journey to standardize OCI image builds using Buildpacks, focusing on risk mitigation and gradual adoption of cloud-native practices for seamless deployment.
Docker Security Insights - Vulnerabilities and Best Practices
Explore Docker security vulnerabilities, countermeasures, and best practices for production environments. Learn about container risks, secrets management, content trust verification, and open-source library considerations.
Containers: Attack and Defense Strategies
Explore container security vulnerabilities and defense strategies with experts Rohit Pitke and Emmanuel Law in this OWASP Foundation presentation.
Securing Containers on the High Seas
Strategies for secure container implementation, focusing on infrastructure, architecture, tooling, policies, and processes. Explores container lifecycle security from development to production.