Kubernetes Infrastructure SIG - Introduction and Recent Updates
Explore recent advancements in Kubernetes infrastructure, including artifact distribution and contributor experience improvements. Learn about future developments and cross-collaboration efforts.
Experience with Hard Multi-Tenancy in Kubernetes Using Kata Containers
Explore Databricks' implementation of hard multi-tenancy in Kubernetes using Kata Containers, addressing challenges, trade-offs, and cloud provider heterogeneity for secure serverless platforms.
Kubernetes Networking 101: An Overview of Popular Options
Explore popular Kubernetes networking options like Calico, Flannel, and Weave. Learn their features, use cases, and comparisons to make informed decisions for your Kubernetes environment.
Least Privilege Containers: Keeping a Bad Day from Getting Worse
Explore strategies for reducing container privileges, enhancing security through unprivileged users and minimal images, and implementing design changes to segment permissions and prevent future vulnerabilities.
Multi-DB on Kubernetes Multi-Cluster - Session 9
Explore strategies for deploying and managing multi-database systems across Kubernetes multi-cluster environments, enhancing scalability and resilience in cloud-native architectures.
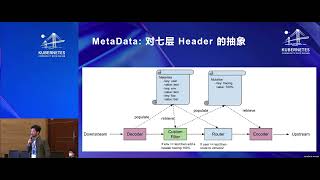
K8s Multi-Cluster Multi-Protocol Security with Aeraki - Session 7
Explore multi-cluster and multi-protocol security in Kubernetes with Aeraki, focusing on advanced techniques for robust and scalable cloud-native environments.
Exploring Cloud Native Platform Engineering - Session 5
Dive into cloud native platform engineering concepts and best practices, focusing on multi-cluster environments and their implementation in modern infrastructure.
Kubernetes Security Implementation Landscape
Explore Kubernetes security implementation strategies and best practices with expert Zhang Jintao, gaining insights to enhance your cloud-native infrastructure protection.
Container Patching: Making It Less Gross Than the Seattle Gum Wall
Explore strategies for efficient container patching, including prevention, detection, fixing, and monitoring. Learn about opensource tools and best practices to streamline the process and meet security requirements.
Hands-on Hacking Kubernetes and Ways to Prevent It
Hands-on workshop exploring Kubernetes vulnerabilities and prevention strategies. Demonstrates remote code execution exploit and teaches mitigation techniques for enhanced container security.
Unpacking Open Source Security in Public Repositories and Registries
Explore security risks in popular open-source projects and public registries. Learn about common misconfigurations, vulnerabilities, and best practices to safeguard your systems when using public resources.
Get Your Security Priorities Straight - Identifying Workloads Under Real Threat with Context
Discover a security prioritization system for Kubernetes workloads based on the MITRE framework, helping differentiate real threats from potential ones in various contexts.
From the Cluster to the Cloud: Lateral Movements in Kubernetes
Explore techniques for lateral movement from Kubernetes containers to cloud resources, covering RBAC misconfigurations, authentication methods, and real-world incidents. Learn prevention and detection strategies.
Windows HostProcess Containers for Configuration and Beyond
Explore Windows HostProcess Containers for efficient Kubernetes cluster management, including CNI implementation, debugging, and on-demand monitoring. Learn practical examples and novel approaches.
Implementing Private 5G Networks for Enterprises with Kubernetes
Explore private 5G networks for enterprises: benefits, components, and Kubernetes orchestration. Learn about cloud-native network functions and special requirements for supporting networking traffic.
Tutorial: So You Want to Develop a Cluster API Provider
Hands-on tutorial for developing a fully CAPI conformant Cluster API provider from scratch, covering key functionalities and best practices for various infrastructure environments.
Containerd and Friends Update: What's New in Runtimes
Explore the latest developments in containerd, including sandboxes, CRI and CNI improvements, and new Rust-based projects. Learn about architectural enhancements and the growing ecosystem of non-core projects.
What's New with SIG Windows
Explore SIG-Windows updates, including HostProcessContainers, KubeProxyNextGen support, and performance testing advancements for Kubernetes on Windows environments.
How SIG Release Cooks Trustworthy Artifacts From Raw Source Code - Kubernetes Build Process
Explore how Kubernetes SIG Release transforms source code into trusted artifacts, focusing on SLSA compliance, community-controlled infrastructure, and expanded artifact signing.
Finding the Needles in a Haystack - Identifying Suspicious Behaviors with eBPF
Explore how AWS uses eBPF to identify security risks in Kubernetes, including malicious activities and communication with known threats. Learn advantages, challenges, and practical applications.
Kubernetes v1.26 Release Overview
Explore the latest features and improvements in Kubernetes v1.26, enhancing container orchestration capabilities for cloud-native applications.