Protecting Sensitive Code with Encrypted Container Images on Kubernetes
Explore encrypted container images for Kubernetes, protecting sensitive code and trade secrets. Learn about image encryption, OCI specs, and DevSecOps integration for enhanced security.
Running Untrusted Code with gVisor - Container Security and Sandboxing
Explore gVisor, an open-source sandbox runtime for enhanced container security. Learn its architecture, use cases, and advantages over other approaches, with a demo of a minimal serverless platform using gVisor and Kubernetes.
Upgrade Images by Digging Out and Automatically Fixing Vulnerabilities
Explore techniques for enhancing container image security through vulnerability scanning, policy controls, and automated fixes. Learn how to protect operating environments and ensure secure distribution channels.
Gatekeeper - Flexible, Shareable Policy for Kubernetes
Explore flexible, shareable Kubernetes policies with Gatekeeper. Learn to implement, customize, and contribute rules for security, legal, and operational requirements across your software lifecycle.
Protect Containerized Applications with System Call Profiling
Explore system call profiling for containerized application security. Learn to develop accurate profiles, monitor runtime behavior, and detect anomalies with low performance overhead and false positives.
Breaking and Fixing Dockerized Environments
Comprehensive analysis of Docker security vulnerabilities and best practices for securing containerized environments, covering image security, runtime protection, and ecosystem tools.
Attack Tree Vignettes for Containers as a Service Applications - AppSecEU 2016
Explore attack tree vignettes for Containers as a Service applications, enhancing your understanding of security vulnerabilities and mitigation strategies in cloud environments.
LXD Internals - UbuConLA 2015
Explore LXD container technology internals, architecture, and implementation details in this in-depth technical presentation from UbuConLA 2015.
Idmapped Mounts
Explore idmapped mounts with Christian Brauner from Canonical, learning about their implementation, use cases, and impact on Linux container security and user namespace isolation.
Restricted Address Spaces for Container Security
Explore container security through restricted address spaces, focusing on vulnerabilities, namespace management, and performance implications in Linux systems.
Secure Your Supply Chain: Adding a Software Bill of Materials to Containers for Improved Vulnerability Scanning
Learn to enhance container security by implementing Software Bill of Materials (SBOM), improving vulnerability scanning, and adopting best practices for a more robust supply chain.
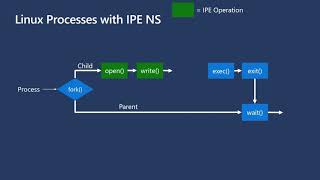
IPE Namespaces - Targeted Enforcement of Container Isolation
Explore targeted enforcement of CI with IPE Namespaces, covering updates, motivations, and practical demonstrations. Learn about namespace properties, isolation, and management techniques.
Kubernetes Security: Using Open Source Tools to Secure Open-by-Default Systems
Explore open-source security tools and frameworks for Kubernetes, covering compliance, threat detection, and network segmentation to enhance your cluster's protection.
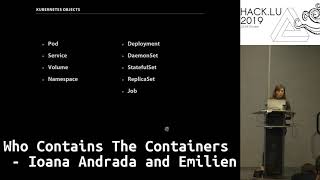
Who Contains the Containers
Explore container orchestration, management, and security with experts Ioana Andrada and Emilien. Gain insights into best practices for efficient and secure container deployment.
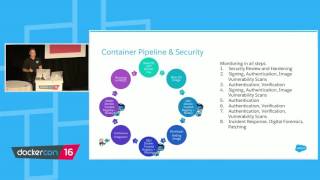
Securing the Container Pipeline at Salesforce - Docker Use Case
Securing Docker containers at Salesforce: infrastructure, pipeline security, monitoring, forensics, and automation for rapid containerization while maintaining data sensitivity and customer trust.
Secure Substrate: Least Privilege Container Deployment
Explore Docker's approach to secure container deployment using least privilege principles, focusing on preventing privilege escalation and unauthorized access in distributed systems.
New Features in Docker Datacenter - Engine 1.13 and Security Scanning
Explore Docker Datacenter's latest enhancements: improved security features, enhanced usability, and streamlined installation process. Learn about secrets management, scanning, and role-based access control.
Trust Your Containers in Production - Docker Image Management and Security
Learn to implement an end-to-end management and security pipeline for Docker images, ensuring safe and efficient deployment of containers from development to production.
Securing Containers - One Patch at a Time
Explore CVE-2016-9962: discovery, implications, and resolution. Dive into kernel boundaries, system calls, and address space randomization for enhanced container security.
What Have Syscalls Done for You Lately? - Exploring Container Security
Explore syscalls, their role in container setup, and how to enhance deployment security by limiting syscall usage. Learn about seccomp, AppArmor, and microservices security advantages.
Docker Engine 1.10 Security Enhancements - Online Meetup
Dr. Diogo Mónica discusses major security enhancements in Docker Engine 1.10, including user namespacing, seccomp profiles, and authorization plugin system for improved container isolation and access control.