Creating Secure Node.js Docker Images - Best Practices and Optimization
Learn to build optimized and secure Node.js Docker images with production-grade guidelines, addressing pitfalls and insecurities in Dockerfile directives for Docker-based applications.
Docker Build: Build Secure Containers with Docker and Snyk
Learn to secure containers using Snyk Vulnerability Scanning integrated with Docker Desktop and Docker Hub. Discover a workflow for building safer, more robust containerized applications.
My Container Image Has 500 Vulnerabilities - Now What?
Learn strategies to address and mitigate vulnerabilities in container images, enhancing security practices for Docker deployments.
Top Dockerfile Security Best Practices
Learn essential Dockerfile security practices to enhance container safety and protect your applications from vulnerabilities and potential attacks.

Do Not Ignore .dockerignore - Optimizing Docker Builds
Optimize Docker builds and enhance security by leveraging .dockerignore files effectively. Learn best practices and implementation strategies.
Breaking Containers to Improve Kubernetes Security - Workshop
Hands-on exploration of container vulnerabilities in Kubernetes clusters, demonstrating potential security breaches and providing practical solutions to enhance container and cluster security.
Container Image Vulnerability Management - Strategies and Best Practices
Practical guide to addressing container image vulnerabilities, covering base image selection, Dockerfile optimization, code dependency checks, and advanced techniques like multistage builds.
Notary - State of the Container Supply Chain
Explore container supply chain security with Notary v2, addressing challenges, discussing progress, and examining future roadmaps for enhanced artifact management and policy enforcement.
One Large Cluster or Lots of Small Ones - Pros, Cons and When to Apply Each Approach
Explore the pros and cons of using multiple small Kubernetes clusters versus a single large shared cluster, and learn about solutions to address their limitations for informed decision-making.
How to Promote the Use of Best Practices and Automate Security Policies
Explore container security automation in CI/CD pipelines, focusing on vulnerability scanning, admission controls, and runtime security using tools like OPA and Kubernetes Admission Controls.
Scratch Containers and the Supply Chain Trouble
Explore scratch containers, their benefits in reducing vulnerabilities, and potential challenges in software composition analysis. Learn about security implications for containerized applications.
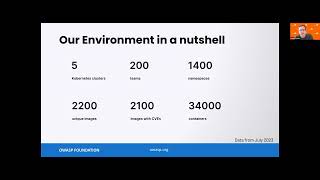
CVE Overload: Scaling Container Vulnerability Scans
Strategies for scaling container vulnerability scans: risk assessment, streamlined triage, automation, and data-driven insights to manage CVEs effectively in large-scale environments.
K8s Post-Exploitation: Privilege Escalation, Sidecar Container Injection, and Runtime Security
Explore post-exploitation scenarios in Kubernetes, including privilege escalation, sidecar container injection, and runtime security. Learn detection techniques and security measures to protect your cluster.
Cleaning up Vulnerable Images from Kubernetes Nodes
Explore Eraser, an open-source solution for automating the scanning and removal of vulnerable images from Kubernetes nodes, enhancing supply chain security in cloud-native environments.
Wolfi: Introduction to the Linux Undistro for Building Small, Up-to-Date, CVE-Free Cloud Images
Discover Wolfi, an innovative Linux 'undistro' for creating small, secure cloud images with minimal attack surfaces and reduced CVE threats. Learn its architecture and tools for keeping software updated.
Wolfi - A Secure-by-Default Distro for Curing Container CVE Chaos
Explore Wolfi, a Linux distribution for building secure, minimal containers. Learn packaging techniques with apko and melange to create vulnerability-free containers and improve your Docker image security.
Reducing Alert Fatigue with Container Scans: Correlate, Prioritize and Filter Based on Usage
Strategies to manage container vulnerabilities: correlate with runtime data, prioritize based on usage, and filter false positives for efficient security in multi-container applications.
Hardening Against Kubernetes Hacks - Live Demo
Explore a real-world Kubernetes cluster takeover through remote code execution, and learn effective mitigation strategies to enhance your system's security against such threats.
Docker Scout - Securing the Complete Software Supply Chain
Explore Docker Scout's real-time vulnerability detection, remediation suggestions, and policy evaluation for enhanced software supply chain security across the entire development lifecycle.
Mastering the Container Security Model - Best Practices and Tools
Explore container security best practices, from building secure images to runtime monitoring. Learn to prevent vulnerabilities, optimize applications, and leverage tools like Docker Scout and Sysdig for enhanced cloud-native security.
Kubernetes Exposed - Seven Hidden Secrets That Will Give You Pause
Descubre secretos ocultos de Kubernetes, desde pods en espacios de nombres inexistentes hasta trucos de seguridad inesperados. Aprende a fortalecer tus sistemas y evitar sorpresas en la gestión de contenedores.