Malware Buried Deep Down the SPI Flash - Sednit's First UEFI Rootkit Found in the Wild
Uncover Sednit's groundbreaking UEFI rootkit campaign, exploring its sophisticated techniques for deep system compromise and implications for cybersecurity in high-profile attacks.

Return of Bleichenbacher's Oracle Threat - ROBOT
Explore the resurgence of a critical TLS vulnerability affecting major vendors and websites, and learn why RSA PKCS #1 v1.5 encryption should be phased out.
New Norms and Policies in Cyber-Diplomacy
Explore evolving cyber-diplomacy landscape, discussing UN consultations, private sector initiatives, and potential new norms in international cybersecurity following 2016 negotiations collapse.
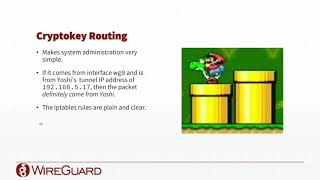
WireGuard - Next Generation Secure Network Tunnel
Explore WireGuard, a modern VPN protocol offering improved security, performance, and simplicity compared to traditional options like IPsec and OpenVPN. Learn about its innovative design and benefits.
A Deep Dive into macOS MDM - and How it Can Be Compromised
Explore macOS MDM vulnerabilities, including bootstrapping stages, IPC flows, and network security. Includes live demo of potential nation-state actor exploit on new Mac devices.
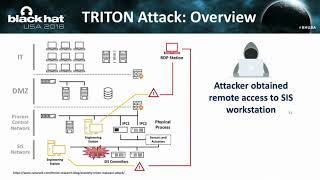
How TRITON Disrupted Safety Systems & Changed the Threat Landscape of Industrial Control Systems
Insights into TRITON attack framework targeting industrial safety systems, exploring its unprecedented impact on cyber-warfare and critical infrastructure protection. Analyzes implications for future threats.
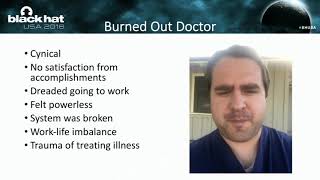
Mental Health Hacks - Fighting Burnout, Depression and Suicide in the Hacker Community
Strategies for addressing mental health challenges in the hacker community, focusing on burnout, depression, and suicide prevention. Emphasizes the importance of recognizing and treating psychological issues.
Tales from the NOC - Going Public in Asia
Insider look at designing and securing Black Hat Asia's network infrastructure. Explore behind-the-scenes challenges, experiences, and evolving designs from the Network Operations Center team.
XOM-Switch - Hiding Your Code from Advanced Code Reuse Attacks in One Shot
XOM-switch: A security tool enabling XOM on Linux apps using PKU, protecting against code reuse attacks without source code or heavy binary rewriting. Enhances application security effortlessly.
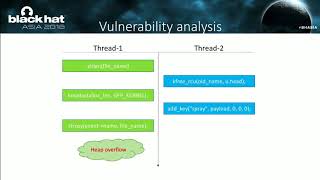
Breaking Android Kernel Isolation and Rooting with ARM MMU Features
Explore a new Android rooting solution, ReVent, exploiting a Use-After-Free vulnerability in 3.18 Linux kernels. Learn about breaking kernel isolation and ARM MMU features for device security.
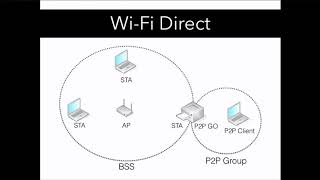
Wi-Fi Direct to Hell - Attacking Wi-Fi Direct Protocol Implementations
Explore Wi-Fi Direct vulnerabilities in Android, HP printers, and Samsung Smart TVs. Learn about protocol architecture, discovery, connection processes, and frame formats. Includes PoC and fingerprinting tool release.
Lost in Transaction - Process Doppelgänging
Explore Process Doppelgänging, a stealthy attack technique that evades security solutions. Learn its advantages over Process Hollowing and understand its detection challenges.
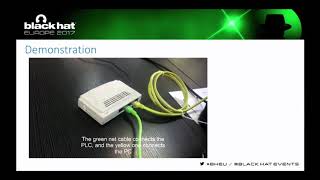
The Spear to Break the Security Wall of S7CommPlus
Unveiling vulnerabilities in S7CommPlus protocol, demonstrating potential security breaches in industrial control systems and proposing countermeasures for enhanced protection.
How to Hack a Turned-Off Computer, or Running Unsigned Code in Intel Management Engine
Explore vulnerability detection and exploitation in Intel Management Engine, bypassing protection mechanisms to run unsigned code on powered-off computers.
GDPR and Third Party JS - Can It Be Done?
Explore GDPR compliance challenges for third-party JavaScript, examining privacy implications and potential solutions for data protection in web development.
Remote Timing Attacks on TPMs - AKA TPM-Fail
Uncovers vulnerabilities in Trusted Platform Modules through timing analysis, revealing potential security risks in hardware-based cryptographic systems used across various computing platforms.
Operation Chimera - APT Operation Targets Semiconductor Vendors
Analysis of APT attacks on semiconductor industry, focusing on Taiwan. Explores threat actors, campaigns, and security status, highlighting potential global supply chain impacts.
Routopsy - Modern Routing Protocol Vulnerability Analysis and Exploitation
Explore vulnerabilities in dynamic routing and redundancy protocols, learn about common misconfigurations, and discover techniques for network attacks and discovery in this comprehensive analysis.
Industrial Protocol Gateways Under Analysis
Explore security vulnerabilities in industrial protocol gateways, examining cross-vendor issues and potential impacts on industrial facilities in the context of Industry 4.0 interconnectivity.
About Directed Fuzzing and Use-After-Free - How to Find Complex & Silent Bugs
Explore directed fuzzing techniques for targeted vulnerability detection, focusing on bug reproduction and patch-oriented testing to uncover complex and silent software flaws.
Virtually Private Networks
Explore the security implications of remote access solutions and VPNs for enterprise mobile workforces, examining potential vulnerabilities and challenges.