Android Pentesting
Learn Android architecture, analysis types, and SSL pinning bypass methods to kickstart your journey into Android penetration testing. Gain practical insights and tool knowledge for mobile security assessment.
CVE-2018-9206 Workshop
Hands-on workshop exploring CVE-2018-9206 file upload vulnerability in Docker. Learn about causes, patches, and bypasses for this security flaw through practical exploitation exercises.
Hunting Android Malware with Importance Of Yara
Explore Android malware hunting using YARA framework. Learn techniques to identify and track malicious apps, even without direct access, and discover methods for detecting similar variants in the wild.
AI vs. Pandemic
Explore how artificial intelligence is being leveraged to combat pandemics, discussing innovative applications and potential future developments in healthcare.
Red, Purple, and Blue Team Activity Using Azure
Hands-on workshop exploring Red, Blue, and Purple team activities using Azure components. Learn container deployment, routing, attack simulation, detection, and prevention techniques in a practical cybersecurity setting.
Technical Breakdown of Magecart - The Digital Bank Robbery
Detailed analysis of Magecart attacks on e-commerce sites, exploring how attackers steal credit card data through client-side JavaScript and strategies to protect against these threats.
Dangling Packages Leading to RCE
Explore dependency confusion attacks and how unclaimed packages in project files can lead to remote code execution. Learn about real-world vulnerabilities and mitigation strategies.
Defending Enterprise Cloud Infrastructure - A Hacker's Perspective
Explore cloud infrastructure security from a hacker's perspective. Learn overlooked attack vectors, defense mechanisms, and critical baseline practices to protect enterprise cloud environments at scale.
The State of Malware from the Eye of the Tiger
Comprehensive overview of global malware trends in 2019, focusing on India and the subcontinent. Explores attack methods, vulnerabilities, and successful malware strategies from basic to advanced threats.
Shack On The Beach
Adam Laurie explores reverse engineering of secure embedded systems in electronic communications, sharing insights from his extensive experience as a security consultant and DEFCON senior staff member.
Andromeda - GUI Based Dynamic Instrumentation Toolkit Powered by Frida
Explore Andromeda, a GUI-based toolkit for dynamic app analysis. Learn about class enumeration, method hooking, and runtime memory analysis features that enhance mobile security research and penetration testing.
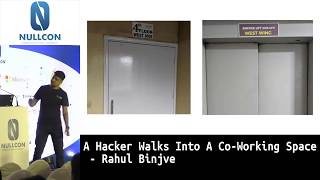
A Hacker Walks Into A Co-Working Space
Explore security vulnerabilities in co-working spaces, including unpatched devices, entry systems, and surveillance cameras. Learn about potential risks and the importance of prioritizing cybersecurity in shared workspaces.
Getting to $10,000 - The Variables at Play in Determining Bounty Awards
Explore factors influencing high-value bug bounty awards with Microsoft's Bug Bounty Program manager, including key strategies for maximizing payouts in cybersecurity research.
Interview with Robert Baptiste aka Elliot Alderson
French security researcher Robert Baptiste discusses Aadhaar data breaches, responsible disclosure, and collaborating with governments to address security issues in this insightful interview at nullcon Goa 2019.
DDoS Mitigation
Explore DDoS attack trends, attacker motivations, and defense strategies. Learn effective mitigation practices to protect your organization from disruptive cyber threats.
Guide on Setting Up IoT Testing Lab
Learn to set up an IoT testing lab with affordable tools, debunk common misconceptions, and gain insights into IoT pentesting from an experienced security researcher.
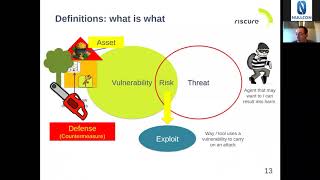
Secure Code Development
Learn secure coding practices for embedded systems in content protection and mobile payments, focusing on real-world asset protection techniques and best practices for software security.
Cybersecurity and Privacy from the Global Lens
Explore global perspectives on cybersecurity and privacy with Eva Galperin, addressing current challenges and future implications for digital safety and personal data protection.
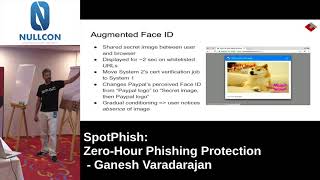
SpotPhish - Zero-Hour Phishing Protection
Explore a whitelist-based browser technique for zero-hour phishing protection, complementing traditional blacklist approaches in the ongoing arms race against phishing attacks.
Security Through Obscurity and Fear
Explore mobile app security flaws in government-developed applications, uncovering overlooked vulnerabilities and their potential impacts on user privacy and data protection.
Expanding Exploitation Beyond X86 and ARM
Comparative study of Xtensa architecture for IoT devices, exploring differences from ARM for security researchers. Covers assembly instructions, security mechanisms, gadget searching, and post-boot persistence techniques.