A Little Less Conversation, A Little More ActionScript
Techniques for in-depth reverse engineering of Flash, mapping ActionScript to undocumented counterparts, and analyzing vulnerabilities in Adobe Flash Player for improved exploit research.
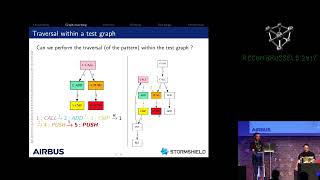
GRAP - Define and Match Graph Patterns Within Binaries
Herramienta para detectar patrones en código binario mediante coincidencia de grafos. Permite definir firmas personalizadas para identificar variantes de malware y extraer información valiosa.
Transforming Open Source to Open Access in Closed Applications
Exploring security risks of integrating open-source components in closed applications, focusing on Adobe Reader's XSLT engine. Techniques for auditing and finding vulnerabilities are demonstrated.
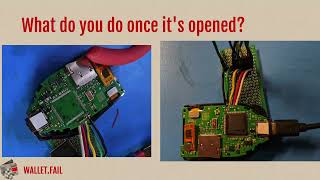
Hacking the Most Popular Cryptocurrency Hardware Wallets
Explore vulnerabilities in popular cryptocurrency hardware wallets with experts Thomas Roth and Dmitry Nedospasov, uncovering potential security risks and attack vectors.
Using WPP and TraceLogging Tracing to Facilitate Dynamic and Static Windows
Explore advanced Windows tracing techniques using WPP and TraceLogging for enhanced dynamic and static analysis in cybersecurity investigations.
X Ray Reverse Engineering
Explore advanced X-ray reverse engineering techniques with expert George Tarnovsky, uncovering hidden hardware secrets and enhancing your security analysis skills.
Burned in AshesBaseband Fairy Tale Stories
Exploring remote protocols in Baseband, reverse engineering methodologies, and bug discovery in mobile communication systems.
Snow Crashing Virtual Reality - 2019 Edition
Exploring security flaws in VR games leading to remote code execution, highlighting privacy concerns and the need for developers to prevent abuse in online AR/VR communities.
Mining Disputed Territories - Studying Attacker Signatures
Explore attacker dynamics and signatures in cyber conflicts, leveraging insights for proactive defense and enhanced situational awareness in the cybersecurity landscape.
The Unseen Dangers of Bloatware
Explore critical vulnerabilities in pre-installed software on Dell and Lenovo PCs, examining the security risks posed by bloatware and the balance between convenience and user safety.
The Road to Qualcomm Trust Zone Apps Fuzzing
Explore Trusted Execution Environment vulnerabilities in Qualcomm's TEE, reverse engineering techniques, and fuzzing methods for TrustZone apps in mobile device security research.
MINimum Failure - Stealing Bitcoins with Electromagnetic Fault Injection
Electromagnetic fault injection attack on Trezor Bitcoin wallet reveals recovery seed without physical tampering. Explores vulnerability, demonstrates attack method, and discusses countermeasures for hardware wallets.
Unveiling the Underground World of Anti-Cheats
Explore the ongoing battle between cheat developers and anti-cheat technologies in gaming. Learn about bypassing techniques and tools for testing anti-cheat software effectiveness.
The Last Generic Win32K KASLR Defeat in Windows
Detailed exploration of Windows kernel security, focusing on KASLR defeats, heap vulnerabilities, and recent changes in RS4. Insights into potential exploits and current Windows KASLR state.
Attacking Hexagon Security Analysis of Qualcomm's ADSP
Explore Qualcomm's Hexagon ADSP security, architecture, and exploitation techniques. Learn reverse engineering methodologies for proprietary systems and mitigations bypass on Android devices.
Reversing and Exploiting Broadcom Bluetooth
Insights into reverse engineering Broadcom Bluetooth firmware, including InternalBlue framework, patching techniques, and discovered vulnerabilities CVE-2018-19860 and CVE-2019-6994.
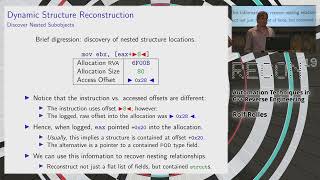
Automation Techniques in C++ Reverse Engineering
Explore automated dynamic analysis techniques for C++ reverse engineering, focusing on structure usage, function argument types, and inheritance relationships through DLL injection.
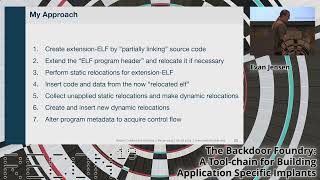
Backdoor Foundry - A Toolchain for Building Application Specific Implants
Explore the creation of application-specific implants using ELF files. Learn about executable containers, software build lifecycle, and advanced techniques for backdoor development in this in-depth technical presentation.
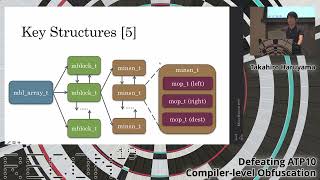
Defeating APT10 Compiler-level Obfuscation
Explore techniques to automatically de-obfuscate APT10's ANEL malware, focusing on opaque predicates and control flow flattening. Learn to modify IDA Pro plugins for effective malware analysis.
The Path to the Payload - Android Edition
Uncover sophisticated Android malware techniques: obfuscation, anti-analysis, encrypted configs, and fake commands. Learn to reverse-engineer and reveal hidden payloads in this advanced security deep-dive.
Vectorized Emulation - Putting It All Together
Explore vectorized emulation's potential in fuzzing, leveraging AVX-512 for parallel VM execution, enhanced code coverage, and hardware-accelerated taint tracking for improved vulnerability detection.