Cantact - An Open Tool for Automotive Exploitation
Explore CANtact, an open-source tool for automotive network analysis. Learn to view, decode, and manipulate CAN bus traffic for reverse engineering and security testing of vehicle systems.
Hacking a Professional Drone
Explore vulnerabilities in professional drones and learn how to exploit them to take control. Discover practical fixes and remediation approaches for these security compromises.
PLC-Blaster - A Worm Living Solely in the PLC
Demonstration of a self-contained PLC worm targeting Siemens S7-1200 PLCs, showcasing network scanning, self-propagation, and remote control capabilities while evading detection.
Android Commercial Spyware Disease and Medication
Explores Android vulnerabilities exploited by spyware and proposes a detection method using fuzz testing to mitigate risks and protect user privacy on smartphones.
Automated Dynamic Firmware Analysis at Scale - A Case Study on Embedded Web Interfaces
Automated framework for discovering vulnerabilities in embedded web interfaces through dynamic firmware analysis. Validates effectiveness on 1925 firmware images from 54 vendors, uncovering critical security flaws.
The Kitchen's Finally Burned Down - DLP Security Bakeoff
Explore flaws in Data Loss Prevention solutions, including administrative interfaces and inspection engines, to understand their capabilities and shortcomings in protecting sensitive information.
Su-A-Cyder - Homebrewing Malware for IOS Like a BO$$
Hands-on workshop for developing iOS malware using the su-A-Cyder framework. Learn techniques to create and execute malware samples on Apple devices, exploiting recent policy changes.
Automated Detection of Firefox Extension-Reuse Vulnerabilities
Discover a novel extension-reuse vulnerability in Firefox and learn about CROSSFIRE, a static analyzer that detects these vulnerabilities and generates exploit templates for rapid proof-of-concept creation.
The Security Wolf of Wall Street - Fighting Crime With High-Frequency Classification
Explore real-time threat detection using machine learning on massive DNS data. Learn about Avalanche stream processing and NLP-Rank for automated phishing detection at scale.
The Tactical Application Security Program - Getting Stuff Done
Practical approach to application security: lightweight team, agile methods, and operational excellence. Covers assessments, bug handling, and private bug bounty programs, with actionable advice for managers and practitioners.
Numchecker - A System Approach for Kernel Rootkit Detection
Explore NumChecker, a VMM-based framework for detecting kernel rootkits using Hardware Performance Counters. Learn about its implementation, effectiveness, and security analysis.
Multivariate Solutions to Emerging Passive DNS Challenges
Explore emerging challenges in passive DNS threat intelligence and learn multivariate solutions to overcome them, enhancing your ability to identify related malicious domains effectively.
Removing Roadblocks to Diversity
Insightful discussion on strategies to attract, retain, and promote women and minorities in cybersecurity, addressing industry challenges and sharing personal experiences to foster inclusivity and diversity.

Behind the Scenes of iOS Security
Explore iOS security mechanisms including HomeKit, Auto Unlock, iCloud Keychain, Data Protection, and JIT hardening. Learn about Apple's innovative approaches to protect user data and enhance mobile security.
HTTP Cookie Hijacking in the Wild - Security and Privacy Implications
Explores security vulnerabilities in websites with partial HTTPS deployment, revealing how cookie hijacking can expose sensitive user data and functionality across major online platforms.

AirBnBeware - Short Term Rentals Long Term Pwnage
Explore network security risks in short-term rentals, including attacks and defenses for both renters and property owners. Learn practical countermeasures to protect against potential threats in the sharing economy.
A Lightbulb Worm
Explore the potential for worms in smart light networks, focusing on Philips Hue's security measures and advanced techniques for hacking IoT devices.
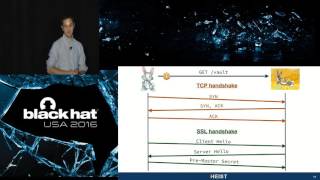
HEIST - HTTP Encrypted Information can be Stolen Through TCP-Windows
Unveils HEIST, a browser-based attack exploiting SSL/TLS vulnerabilities without network access. Demonstrates how to leak cross-origin response sizes, enabling compression-based attacks and sensitive information extraction from popular websites.
The Year in Flash
Explore notable Flash vulnerabilities and exploits from the past year, including attack surfaces, common vulnerability types, and future trends in Flash security.
Pangu 9 Internals
Explore iOS 9 jailbreak internals, vulnerabilities, and exploitation techniques used in Pangu 9. Learn about system service flaws, code execution methods, and persistent code signing bypass.
Breaking FIDO - Are Exploits in There?
Explore FIDO authentication's vulnerabilities, potential exploits, and protective measures for enterprises in this comprehensive analysis of the protocol's security landscape.