The Weakest Element of Acquiring Bank Infrastructure
Exploring vulnerabilities in Terminal Management Systems for card payments, revealing potential security risks in acquiring bank infrastructure and POS terminals.
SAP RCE - The Agent Who Spoke Too Much
Explore SAP vulnerabilities: authentication bypass, OS command injection, and privilege escalation. Learn to decrypt sensitive files, manipulate security reports, and implement protective measures.
Hacking the DevOps Butler - From Nothing to Admin
Explore Jenkins vulnerabilities and exploitation techniques, focusing on two critical flaws that allow unauthenticated attackers to gain admin access and control entire infrastructures.
Jackpotting Fortune-500 Treasuries
Unveiling critical vulnerabilities in ERP systems, demonstrating how attackers can manipulate financial processes and exploit Oracle's ERP for unauthorized monetary gains without detection.
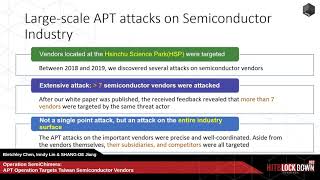
Operation SemiChimera
Análisis detallado de ataques APT a la industria de semiconductores en Taiwán, enfocándose en Operation SemiChimera. Explora técnicas, tácticas y motivaciones de los atacantes, ofreciendo insights para mejorar la ciberseguridad del sector.
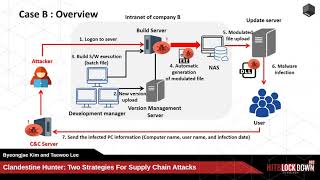
Two Strategies for Supply Chain Attacks
Explore two supply chain attack strategies by BARIUM APT group, analyzing real-world cases and their tactics. Learn defensive measures against these sophisticated cyber threats.
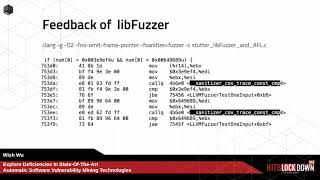
Exploring Deficiencies in Automatic Vuln Mining Technology
Exploring deficiencies in automatic vulnerability mining tools and proposing a new technique to improve software security through analysis of popular tools and creation of challenging example codes.
Common Flaws in ICS Network Protocols
Análisis de vulnerabilidades comunes en protocolos de red ICS, incluyendo públicos y privados. Demuestra ataques potenciales como inyección de comandos y sniffing de tráfico sin cifrado en infraestructuras críticas.
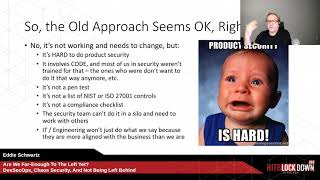
DevSecOps, Chaos Security, and Not Being Left Behind
Exploring DevSecOps and Chaos Security Engineering to integrate business, development, and security teams for effective product security and staying ahead of adversaries.
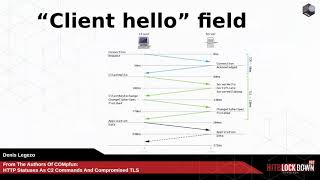
HTTP Statuses as C2 Commands and Compromised TLS
Explore innovative malware techniques using HTTP statuses as C2 commands and compromising TLS encryption. Learn about COMPFun's evolution and its impact on cybersecurity.
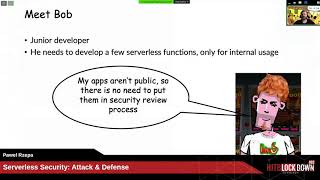
Serverless Security - Attack & Defense
Explore serverless security vulnerabilities and defenses across AWS, Azure, and GCP. Learn about dependency poisoning, validation errors, and insecure defaults with practical demos and prevention strategies.
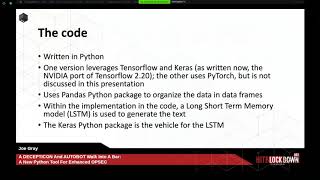
Python for Enhanced OPSEC
Python-based tool for enhancing OPSEC by autonomously posting on social media, using NLP and ML to mimic user behavior. Ideal for those needing to abandon targeted accounts without alerting adversaries.
How to Hack Medical Imaging Applications via DICOM
Explore critical security vulnerabilities in DICOM servers, protocols, and libraries used in medical imaging systems. Learn to identify and fix bugs in the DICOM ecosystem.
Exploring and Exploiting the SQLite
Explore SQLite vulnerabilities, auditing strategies, and fuzzing techniques. Learn about Magellan 2.0, shadow tables, and bypassing defense mechanisms for remote code execution in Chrome and SQLite binaries.
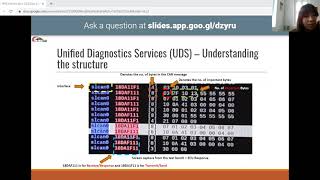
Car Hacking
Explore car hacking essentials: CAN types, UDS, ISO TP, MOST/LIN/Flexray/Automotive Ethernet protocols. Gain insights from industry experts in this virtual lab on automotive cybersecurity.
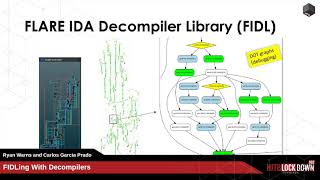
FIDLing with Decompilers
Explore decompilation basics, popular tools, and the Hex-Rays Decompiler. Learn about FIDL, a new library simplifying decompiler API usage, with practical examples and demos.
Zen - A Complex Campaign of Harmful Android Apps
Explore Android malware techniques, from repackaging apps to sophisticated rooting trojans. Learn about click fraud, exploit bundling, and persistence mechanisms used by malicious actors.
Secret Flaws of In-DRAM RowHammer Mitigations
Unveiling secret flaws in DRAM RowHammer mitigations, exploring Target Row Refresh implementation, and introducing TRRespass: a RowHammer fuzzer for creative hammering patterns to bypass protections.
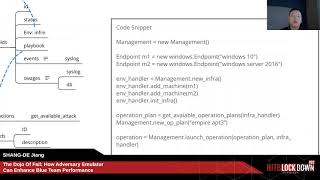
How Adversary Emulation Can Enhance Blue Team Performance
Explore adversary emulation to enhance blue team performance, addressing cybersecurity expert shortages and evolving attack methods. Learn to design attack playbooks and test security products effectively.
Bugrank - A Community Bug Bounty Platform
Introducing Bugrank: an open-source community bug bounty platform. Explore its design, architecture, and functions. Learn how to set up your own bug reporting system for enhanced cybersecurity.
Army of Undead - Tailored Firmware Emulation
Explore automated firmware emulation techniques for embedded systems, covering root filesystem location, architecture identification, and emulation methods using open-source tools and scripts.