War Stories on Embedded Security Pentesting IoT Building Managers and How to Do Better
Explore embedded security vulnerabilities in IoT building managers, learn pentesting techniques, and discover best practices for improving IoT security in this insightful talk.
Not a Security Boundary - Bypassing User Account Control
Explore UAC bypass techniques, integrity levels, and security monitoring. Learn about registry manipulation, file operations, and PowerShell scripting for enhancing Windows security knowledge.
Aiding Static Analysis - Discovering Vulnerabilities in Binary Targets through Knowledge Graph
Explore advanced techniques for vulnerability detection in binary targets using knowledge graphs, static analysis, and specialized tools like Binary Ninja and Kraken.
Tracing Adversaries - Detecting Attacks with ETW
Explore advanced threat detection using ETW, covering process tracking, PowerShell monitoring, and file I/O analysis for enhanced cybersecurity defenses.
An Introduction to Writing Win32 Shellcode
Learn to write Win32 shellcode, covering memory, registers, testing, generation, and stagers. Gain practical skills for creating and executing custom shellcode.
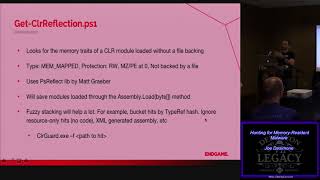
Hunting for Memory Resident Malware
Explore techniques for detecting memory-resident malware, including API analysis, post-breach detection, and CLR hooking. Learn why memory hunting is crucial in cybersecurity.
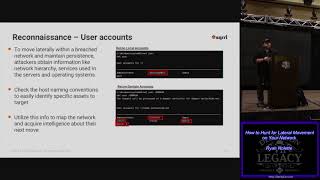
How to Hunt for Lateral Movement on Your Network
Learn techniques to detect and analyze lateral movement in network security, covering reconnaissance, privilege escalation, and credential theft, with practical datasets for effective monitoring.
Windows Rootkit Development - Python Prototyping to Kernel Level C2
Explore kernel-mode drivers for network traffic control, TCP connection handling, and proxy manipulation. Learn weaponization and deployment strategies for advanced Windows rootkit development.
Rapid Incident Response with PowerShell
Learn essential PowerShell techniques for rapid incident response, focusing on preparation, identification, and containment strategies to effectively handle cyber attacks like NotPetya.
Hidden Treasure - Detecting Intrusions with ETW
Explore intrusion detection using ETW, covering event capture, real-time solutions, and practical examples. Learn to identify malicious activities and optimize event monitoring for enhanced cybersecurity.
Surviving the Modern Compliance Minefield
Navigate the complex landscape of modern compliance with insights on legal actions, data protection, and evolving standards for cybersecurity professionals and organizations.
I Simulate Therefore I Catch - Enhancing Detection Engineering with Adversary Simulation
Enhance detection engineering skills through adversary simulation techniques, focusing on prevention controls, resilience validation, and automated simulation for improved cybersecurity.
Red Team Level Over 9000 - Fusing the Power of NET With a Scripting Language of Your Choosing
Explore advanced red teaming techniques by combining .NET with scripting languages, covering concepts like IronPython, WebAssembly, and PowerShell for enhanced offensive capabilities.
Endpoint Detection Super Powers on the Cheap with Sysmon
Discover cost-effective endpoint detection techniques using Sysmon, enhancing your cybersecurity capabilities with powerful tools and strategies.
Old Tools New Tricks - Hacking WebSockets
Explore WebSocket hacking techniques, from basic concepts to advanced exploits, using various tools and methods for secure testing and vulnerability assessment.
Confessions of an IT OT Marriage Counselor
Explore challenges, threats, and misconceptions in industrial control systems with insights on bridging IT and OT for enhanced cybersecurity in critical infrastructure.
NET Manifesto - Win Friends and Influence the Loader - Casey Smith
Explore CLR binding, manifests, and side-by-side loading in .NET. Learn about fusion logging, profilers, and dynamic wrappers for enhanced understanding of .NET internals.
Red Team Methodology - A Naked Look
Explore red team methodology, covering pre-engagement, external and internal tactics, infrastructure automation, and effective communication for comprehensive security assessments.
Full Steam Ahead Serverless Hacking 101
Explore serverless hacking techniques, including environment setup, demonstrations, and common vulnerabilities like SQL injection and cross-site scripting in this comprehensive tutorial.
Kerberoasting Revisited
Explore advanced Kerberoasting techniques, encryption types, and defenses. Learn about the "tgtdeleg" trick and Rubeus for improved Kerberoasting in this cybersecurity deep dive.
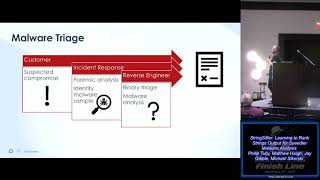
Learning to Rank Strings Output for Speedier Malware Analysis
Explore techniques for efficient malware analysis using string ranking, featuring gradient boosted decision trees and the StringSifter tool for faster threat assessment.