Breaking VSM by Attacking SecureKernel
Explore vulnerabilities in Windows 10's SecureKernel, potentially compromising Virtualization-Based Security. Learn exploitation techniques and the process of finding and fixing critical security flaws.
Practical Defenses Against Adversarial Machine Learning
Explore real-world attacks on ML systems, from recommendation engines to email filters, and learn practical defense strategies against adversarial machine learning threats.
Detecting Access Token Manipulation
Demystifying Windows access token manipulation attacks and providing effective detection strategies for defensive practitioners in enterprise environments.
Mind Games - Using Data to Solve for the Human Element
Discover data-driven techniques to effectively reduce human risk in cybersecurity, challenging traditional training approaches and focusing on behavioral change strategies.
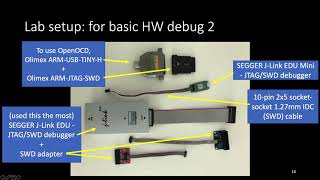
Finding New Bluetooth Low Energy Exploits via Reverse Engineering Multiple Vendors' Firmwares
Explore Bluetooth Low Energy vulnerabilities through firmware reverse engineering, uncovering remote code execution exploits at the protocol's lowest levels without authentication or pairing.
Election Security - Securing America's Future
Explore the US government's efforts to secure elections, including intelligence sharing, cybersecurity services, and collaboration with state and local officials to protect against malicious activities.
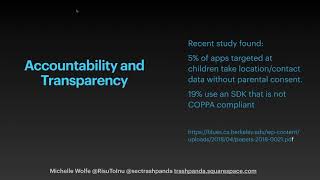
EdTech - The Ultimate APT
Explore the privacy and security risks of educational technology implementation in schools, highlighting concerns and potential actions for improvement.
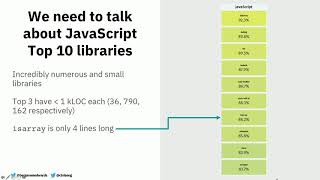
The Devils in the Dependency - Data Driven Software Composition Analysis
Análisis de datos sobre el uso de bibliotecas de código abierto en aplicaciones, examinando vulnerabilidades, dependencias y patrones de actualización para mejorar la seguridad del software.
Decisions and Revisions - The Ever Evolving Face of the Black Hat NOC
Explore the evolution of Black Hat's network operations, including equipment choices, regional adaptations, and cybersecurity insights from global events. Gain insider knowledge on network deployment and attendee behavior trends.
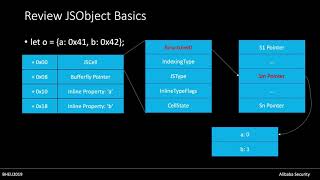
Thinking Outside the JIT Compiler - Understanding and Bypassing StructureID Randomization with Generic and Old-School Methods
Explore generic methods to bypass StructureID Randomization, gaining arbitrary Read/Write ability without relying on JIT compiler-related techniques. Learn innovative approaches to inspire better security mitigations.
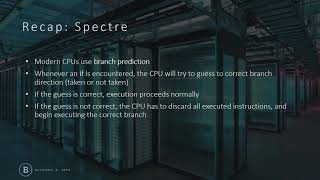
Bypassing KPTI Using the Speculative Behavior of the SWAPGS Instruction
Unveiling a new speculative execution attack exploiting SWAPGS instruction, bypassing existing CPU and kernel protections. Explores side-channel vulnerabilities and their implications for system security.
Practical Side-Channel Attacks Against WPA-TKIP
Explore practical side-channel attacks against WPA-TKIP in Wi-Fi networks, analyzing vulnerabilities and countermeasures in this widely-used legacy protocol.
Fatal Fury on ESP32 - Time to Release Hardware Exploits
Methodical exploration of defeating ESP32 security features using low-cost hardware techniques, including voltage glitching and analog side-channels, with implications for IoT device security.
Alexa, Hack My Serverless Please
Explore serverless security risks, focusing on event injection attacks across various platforms. Learn to identify and mitigate vulnerabilities in cloud-based applications.
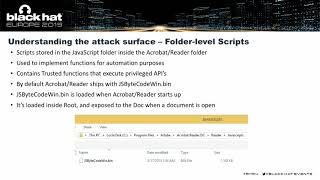
Tackling Privilege Escalation with Offense and Defense
Explore privilege escalation in JavaScript engines, focusing on offensive techniques and defensive strategies. Learn about vulnerabilities, attack surfaces, and security model improvements.
How to Break PDF Encryption
Learn techniques to break PDF encryption, analyze vulnerabilities, and understand the structure of encrypted documents for enhanced security awareness.
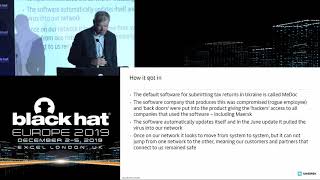
Implementing the Lessons Learned From a Major Cyber Attack
Explore lessons from Maersk's 2017 NotPetya cyber-attack, focusing on recovery strategies, resilient infrastructure, and evolving security principles for modern threats.
What the Fuzz
Explore cutting-edge fuzzing technologies, their potential, and future developments through demos, CVEs, and research insights from experts in the field.
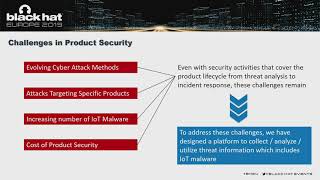
Understanding the IoT Threat Landscape
Explore IoT threat landscape, malware analysis, and Panasonic's approach to developing resilient products and an IoT SOC. Learn about security testing and the IoT Intelligence Platform.
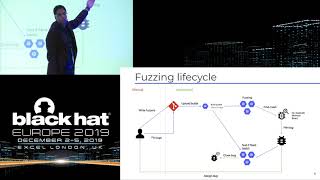
ClusterFuzz - Fuzzing at Google Scale
Explore Google's massive fuzzing infrastructure, ClusterFuzz, and learn how it finds thousands of security vulnerabilities across Google products and open-source projects.
Is Your Mental Health for Sale?
Explore the hidden world of data tracking on mental health websites, uncovering privacy risks and ethical concerns in online depression tests and advertising practices.