Mobile Hacking - Gustavo "Puky" Sorondo: Mobile Hacking Tips - Ekoparty Security Conference - 2020
Consejos y trucos para testear la seguridad de aplicaciones móviles, incluyendo tráfico remoto, certificados SSL, apps híbridas y un caso práctico de hackeo a Starbucks.
#Eko2020 Bounty Hunters | Adrian Pedrazzoli: XSS de -1 a 0
Aprende técnicas básicas para detectar XSS, tipos, recursos necesarios y ejemplos de hallazgos en programas de Bug Bounty. Incluye recomendaciones prácticas para cazadores de recompensas.
Blue Team - Generando Visibilidad y Respondiendo Ante Ciberamenazas Desde un SOC
Metodología para detectar y responder ante ciberamenazas en organizaciones, abordando visibilidad, priorización y automatización desde un SOC. Incluye servicios, componentes y herramientas para una gestión eficaz.
Social Engineering - Emiliano Piscitelli: Pretextos y el Metodo P.I.C.O - Ekoparty Security Conference - 2020
Descubre cómo crear pretextos efectivos en ingeniería social utilizando el Método P.I.C.O. Aprende de ataques reales y mejora tus habilidades en esta charla de la Ekoparty Security Conference.
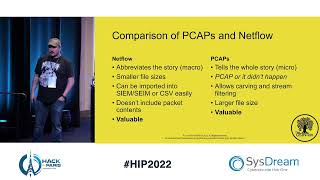
NetflOSINT- Taking an Often-Overlooked Data Source and Operationalizing It - Joe Gray - Hack in Paris
Explore NetflOSINT: Leveraging overlooked Netflow data for efficient network forensics. Learn extraction techniques, analysis methods, and tools to enhance threat hunting and intelligence gathering.
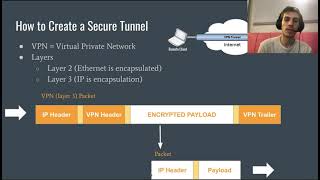
All Roads Lead to OpenVPN Pwning Industrial Remote Access Clients - Sharon Brizinov - Hack in Paris - 2021
Uncover critical vulnerabilities in industrial remote access solutions using OpenVPN, potentially leading to remote code execution. Learn about the risks and implications for cybersecurity.
Exploits in Wetware - R. Sell - Hack in Paris - 2019
Discover social engineering tactics, real-world attacks, and protective strategies. Learn about OSINT techniques, vishing strategies, and methods to safeguard organizations against evolving threats in this eye-opening presentation.
All Your GPS Trackers Belong to Us - C. Kasmi, P. Barre - Hack in Paris - 2019
Explore security vulnerabilities in GPS trackers, including traffic analysis, SMS configuration exploitation, protocol reverse engineering, and GPS signal spoofing. Learn about privacy risks and potential attack scenarios.
In NTDLL I Trust - Process Reimaging and Endpoint Security Solution Bypass - E. Carroll - Hack in Paris - 2019
Explore a new defense evasion technique, Process Reimaging, exploiting Windows OS vulnerabilities to bypass endpoint security solutions like Windows Defender. Learn attack vectors, weaponization, and protection recommendations.
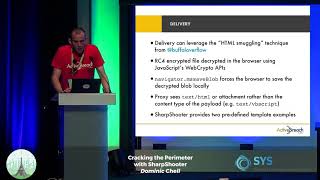
Cracking the Perimeter with SharpShooter - Dominic Chell - Hack in Paris - 2019
Explore advanced payload generation techniques for red team engagements, including bypassing endpoint protections and evading sandboxing through innovative methods like XML stylesheets and COM.
IronPython... OMFG - Marcello Salvati - Hack in Paris - 2019
Explore dynamic .NET runtime access using Python, bypassing PowerShell restrictions for stealthy offensive operations in Windows environments.
Social Forensication: A Multidisciplinary Approach to Successful Social Engineering - J.Gray - Hack in Paris - 2019
Explore innovative social engineering techniques, including memory image analysis and rogue Wi-Fi attacks, along with defensive strategies and ethical considerations for cybersecurity professionals.
Abusing Google Play Billing for Fun and Unlimited Credits! - G. Lopes - Hack in Paris
Explore vulnerabilities in Google Play Billing API, analyzing real-world examples and demonstrating how attackers can bypass payment processes in popular Android games through reverse engineering.
Sneaking Past Device Guard - Philip Tsukerman - Hack in Paris - 2019
Explore techniques to bypass Windows 10's Device Guard, including VBA, trusted documents, and alternative execution vectors. Dive into internals of scripting engines and host processes.
Knockin' on IPv6's Doors - Fernando Gont - Hack in Paris - 2018
Exploring IPv6 security policies and their mismatches with IPv4, revealing real-world implications for dual-stacked sites through a wide-scale evaluation project.
From Printed Circuit Boards to Exploits: Pwning IoT Devices Like a Boss - Damien Cauquil - Hack in Paris - 2018
Explore hardware hacking of a Bluetooth smartlock, from circuit board analysis to exploit development, covering electronics basics, reverse engineering, and mobile app vulnerabilities.
Auditd for the Masses - Philipp Krenn - Hack in Paris - 2018
Explore Linux Audit daemon with Auditbeat for centralized event monitoring, file integrity checks, and security breach detection using interactive dashboards and log analysis.
Debate- Hackers, the Media, Truth, Trust & Alternative Facts - Hack in Paris - 2017
Debate on hackers, media, truth, and trust. Explores fact-checking, vulnerability disclosure, fake news, and regaining trust in the digital age. Features expert panel discussion and audience participation.
802.1x Network Access Control and Bypass Techniques - Valerian Legrand - Hack in Paris - 2017
Explore 802.1x network access control, its vulnerabilities, and bypass techniques. Learn why it's not a perfect solution for critical asset protection and how attackers can exploit it.
The Internet of Vulnerabilities - Deral Heiland - Hack in Paris - 2017
Explore IoT security vulnerabilities and research methodologies with insights on ecosystem structures, live demonstrations, and manufacturer collaborations for mitigation strategies.
Beyond OWASP Top 10 by Aaron Hnatiw - Hack in Paris - 2017
Explore 5 dangerous web vulnerabilities beyond OWASP Top 10, covering exploits and mitigations for both developers and pentesters to enhance application security.