Lessons Learned by the WordPress Security Team
Insights from WordPress Security Team's journey: challenges, strategies, and lessons in safeguarding open-source software and educating users on cybersecurity best practices.
Red Teaming a Manufacturing Network - Without Crashing It
Explore techniques for safely red teaming manufacturing networks, including reconnaissance, passive methods, and potential attack vectors, while learning mitigation strategies and best practices.
Active Directory Password Blacklisting
Explore Active Directory password blacklisting techniques, implementation challenges, and testing frameworks for enhanced security in Windows environments.
You're Good and You Should Feel Good
Gain insights on interviewing, career growth, and leadership in cybersecurity. Learn to navigate company culture, contribute effectively, and seize opportunities for professional development.
The Chrome Crusader
Explore Chrome extension vulnerabilities, security considerations, and potential exploits. Learn about architecture, headers, and isolation techniques for safer browsing experiences.
ATT&CKing the Status Quo - Improving Threat Intel and Cyber Defense with MITRE ATT&CK
Explore MITRE ATT&CK framework to enhance threat intelligence and cyber defense strategies. Learn implementation tips, detection techniques, and industry examples for improved security posture.
Hire Ground Kickoff
Practical advice for aspiring cybersecurity professionals on resumes, interviews, and overcoming imposter syndrome. Insights on navigating the competitive entry-level job market.
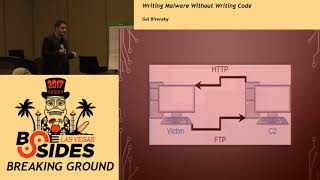
Writing Malware Without Writing Code
Explore techniques for creating malware without coding, covering keyloggers, ransomware, and persistence methods. Learn about ethical hacking and cybersecurity vulnerabilities.
CheckPlease - Payload-Agnostic Sandbox Detection
Explore payload-agnostic sandbox detection techniques, including sleep evasion, encryption, and user activity analysis. Learn to build profiles and implement various detection methods across languages.
Pwning Software-Defined Networking - SDN
Explore software-defined networking vulnerabilities, focusing on OpenFlow, controllers, and REST APIs. Learn to manipulate traffic flow and exploit SDN weaknesses.
YARA-as-a-Service - Real-Time Serverless Malware Detection
Explore real-time serverless malware detection using YARA and Binary Alert. Learn about scalable security tools, features, and implementation for enhanced threat protection.
Zero Trust Networks - In Theory and in Practice
Comprehensive exploration of Zero Trust Networks, covering theory, implementation strategies, key systems, and practical considerations for enhanced network security.
Introduction to Reversing and Pwning
Explore reverse engineering and exploitation techniques, covering low-level programming, memory vulnerabilities, and essential tools for cybersecurity enthusiasts and professionals.
IATC - HHS Task Force
Explore cybersecurity challenges in healthcare with insights on task forces, device manufacturing, disclosure programs, and legacy systems from industry expert Josh Corman.
WAFs FTW! A Modern DevOps Approach to Security Testing Your WAF
Explore modern DevOps approach to security testing Web Application Firewalls (WAFs) using Framework for Testing WAFs (FTW). Learn objective WAF evaluation, rapid prototyping, and continuous testing strategies.
Federated Login CSRF
Explore federated login CSRF vulnerabilities in OpenID Connect and OAuth 2.0, examining attack scenarios, risks, and mitigation strategies for secure identity linking in web applications.
An Agile Framework for Building GDPR Privacy and Data Protection Requirements into SDLC
Agile framework for integrating GDPR privacy and data protection requirements into software development lifecycle, using a tag-based approach to identify and implement necessary features efficiently.
Androsia - A Tool for Securing In Memory Sensitive Data
Innovative tool for securing sensitive data in Android apps through static analysis and bytecode transformation, enhancing defense-in-depth even after compromise.
Where We're Going, We Won't Need Passwords
Explore enterprise-wide multifactor authentication deployment, addressing technical challenges, user experience, and lessons learned for seamless workforce authentication across devices and legacy systems.
Building Secure ASP.NET Core MVC Applications
Explore ASP.NET Core MVC security features, including XSS and CSRF protection. Learn to build robust web applications with modular architecture and cross-platform compatibility.
Fixing Broken Enterprise Threat Models with OWASP Efforts - Commissioning AppSec Professionals for Real Change
Explore how OWASP projects can revolutionize enterprise threat modeling, addressing compliance issues, undefined attack surfaces, and risk distortions to create measurable security impact.