Hacking JavaScript Desktop Apps with XSS and RCE
Explore techniques for auditing Electron apps, understanding XSS in desktop environments, and exploiting vulnerabilities to achieve remote code execution in JavaScript-based applications.
Mr. Lord Goes to Washington, or Applying Security Outside the Tech World
Insights on applying enterprise security practices to political organizations, addressing phishing, best practices implementation, and disinformation campaigns. Valuable for SMBs and tech product developers.
In Curation We Trust - Generating Contextual and Actionable Threat Intelligence
Optimizing threat intelligence with MISP: Learn to curate, contextualize, and automate TI feeds for actionable insights, reducing false positives and enhancing SOC, IR, and malware analysis collaboration.
Understanding the Discipline to Optimize Cyber Defense Collaboration
Explore the Cyber Threat Intelligence Analyst role, its competencies, and how it intersects with other cybersecurity disciplines to enhance collaboration and organizational security posture.
The Story Continues - Hacking Some More Secure Portable Storage Devices
Exposé sur les failles de sécurité des dispositifs de stockage portables "sécurisés" avec chiffrement matériel AES, démontrant leur vulnérabilité malgré les promesses des fabricants.
INCONTROLLER - New Malware Developed to Target Industrial Control Systems
Analysis of INCONTROLLER: a rare and dangerous state-sponsored malware targeting industrial control systems, with focus on its components, attack scenarios, and implications for cybersecurity professionals.
LOLDocs - Sideloading in Signed Office Files
Exploring innovative phishing techniques using code side-loading in signed Office documents, focusing on vulnerabilities in Microsoft-signed add-ins and their potential exploitation for malicious purposes.
I Am Become Loadbalancer, Owner of Your Network
Explore load balancer vulnerabilities, architecture, and post-breach tactics. Learn about high-profile exploits, device deployment, and how to navigate these critical network components for both offensive and defensive purposes.
Adaptive Adversaries
Explore the evolution of cyber threats and defense strategies, focusing on adaptive adversary techniques and the future of cybersecurity. Learn to build more effective defenses against sophisticated attacks.
Defeating EDRs Using Dynamic Invocation in C#
Explore advanced techniques for bypassing Endpoint Detection and Response systems using Dynamic Invocation in C#, enhancing your understanding of cybersecurity vulnerabilities and defenses.
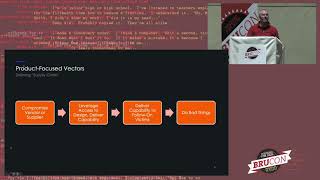
A Critical Assessment of Supply Chain Intrusion Vectors
Critical analysis of supply chain attacks, distinguishing between modification and third-party compromise. Explores functionality, execution, and defensive measures, providing insights for risk assessment and mitigation strategies.
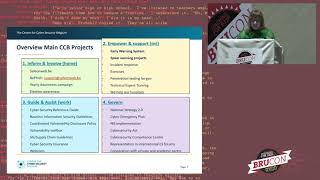
How to Make Belgium One of the Least Cyber Vulnerable Countries
Découvrez la nouvelle stratégie cybersécurité belge visant à protéger le pays, ses entreprises et ses citoyens, ainsi que son alignement avec les initiatives européennes.
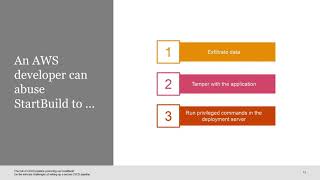
The Risk of CI - CD Pipeline Poisoning via CodeBuild
Explore CI/CD pipeline vulnerabilities in AWS services, focusing on CodeBuild abuse. Learn how small decisions can compromise security, bypass controls, and potentially lead to pipeline poisoning.
Visibility Beyond Perimeters - Detecting C2 at Time of Execution
Innovative network-based threat detection technique providing real-time alerting without endpoint software. Leverages internet infrastructure to detect malicious activity across organizational boundaries, augmenting existing EDR solutions.
PIC Your Malware
Explore advanced techniques for building and hiding custom malware, including position independent code and automated payload generation, to evade detection by security products and analysts.
Hacktivism During a Global Pandemic
Explore hacktivism's evolution from website attacks to shaping policies and protecting hospitals during crises. Discover the impact of idealistic tech enthusiasts in addressing global challenges.
Black Ops of TCP/IP 2011
Explore advanced TCP/IP techniques and vulnerabilities with renowned security expert Dan Kaminsky in this thought-provoking keynote address from BruCON 0x03.
Incident Response in the Cloud - Foggy with a Ray of Sunshine
Explore challenges and solutions for incident response in cloud environments, focusing on logging options, visibility issues, and automated response techniques for improved security operations.

Atomic Threat Coverage - Being Threat Centric
Atomic Threat Coverage framework: Automatically generate actionable analytics to combat threats based on MITRE ATT&CK model, unifying detection, response, mitigation, and simulation for efficient security operations.
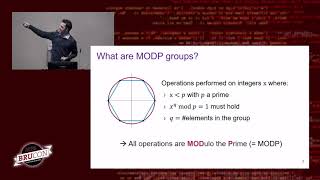
Weaknesses in WPA3's Dragonfly Handshake
Uncovers critical vulnerabilities in WPA3's Dragonfly handshake, demonstrating password partitioning attacks and discussing practical implications for Wi-Fi security. Explores countermeasures and assesses WPA3's effectiveness as a modern security protoco…
Defeating Bluetooth Low Energy 5 PRNG for Fun and Jamming
Uncover vulnerabilities in Bluetooth Low Energy 5's PRNG, enabling sniffing and jamming of BLE 5 connections. Learn to exploit weaknesses and use updated tools for IoT security testing.