Abusing Security Products to Bypass Windows Protections
Unveiling critical vulnerabilities in security products that allow bypassing Windows protections. Explores impact, solutions, and provides a validation tool for system security.
Planning Effective Red Team Exercises
Learn best practices for planning and executing effective red team exercises, including scenario design, objective setting, and rules of engagement to simulate real adversaries and provide maximum value to clients.
Case Study in Using Bad Malware Design Against Attackers
Explore how poor design choices in malware can be exploited by defenders, featuring case studies like AlienSpy/JSocket. Learn strategies to disable malware globally by leveraging vulnerabilities in their implementation.
APT Reports and OPSEC Evolution
Explore how advanced threat actors adapt to security innovations and APT reports, and discover strategies for improving cybersecurity defenses.
IoT on Easy Mode - Reversing Embedded Devices
Discover the ease of embedded device hacking in IoT, exploring techniques beyond x86/x64 architectures. Learn essential tools and justifications for specialized equipment in this insightful security talk.
Sharing is Caring - Understanding & Measuring TI Sharing Effectiveness
Explore threat intelligence sharing effectiveness through data analysis, open-source projects, and proposed metrics for improving sharing communities and platforms.
The Ransomware Threat - Tracking the Digital Footprints
Explore ransomware's evolution, prevention strategies, and digital footprint tracking techniques to enhance cybersecurity and protect businesses from evolving threats.
Mobile App Corporate Espionage
Explore real-world corporate espionage techniques using hidden behaviors in mobile apps, focusing on data risk threats and out-of-band communications for leaking sensitive information.
Why Can't We Have Nice Things - Conflict Resolution in InfoSec
Explore conflict resolution in InfoSec, understanding why conflicts often escalate and learning strategies to resolve disagreements productively without burning bridges.
Metabadger - Automating IMDS Protection at Scale in AWS
Discover Metabadger, an open-source tool for upgrading EC2 instances to IMDSv2, preventing SSRF-based credential theft. Learn how Salesforce automated IMDS protection at scale in AWS.
Emerging Best Practices in Software Supply Chain Security - What We Can Learn from Google, the White House, OWASP, and Gartner
Explore emerging best practices in software supply chain security, analyzing guidelines from major organizations to compile key strategies for mitigating risks in deployment pipelines.
Developing a Baseline Security Standard for Endpoint Devices
Explore the development of baseline security standards for endpoint devices in a Zero Trust Network implementation, focusing on OS security capabilities and threat vector identification.

If You’re Not Using SSH Certificates You’re Doing SSH Wrong
Discover why SSH certificates outperform traditional keys for secure access. Learn about their benefits and implementation in this concise, eye-opening talk on modern SSH practices.
RadRAT - An All-in-One Toolkit for Complex Espionage Ops
Uncover RadRAT: a sophisticated, undetected malware with remote access capabilities, lateral movement, and evasion mechanisms for targeted attacks and information exfiltration in large networks.
Deconstructing APT28's XAgent for OSX
Detailed analysis of APT28's XAgent malware for macOS, exploring its advanced spying capabilities including keylogging, screen capture, and data exfiltration from iOS backups.

WebAuthn - How to FIDO
Explore FIDO2 WebAuthn for phishing-resistant, passwordless authentication. Learn implementation strategies for stronger user protection on websites and applications.
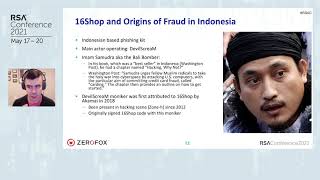
My Phishing Kit Burnbook
Explore phishing kit ecosystems, organized crime groups, and PhishPond tool for detection and analysis in this cybersecurity deep dive.
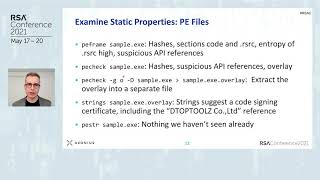
Analyzing Windows Malware on Linux - Getting Started Tips and Examples
Practical session on using free Linux tools for Windows malware analysis, featuring the REMnux toolkit. Learn essential techniques for incident response and SOC analysis.
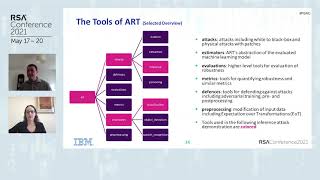
Evasion, Poisoning, Extraction, and Inference - Tools to Defend and Evaluate
Explore tools for defending AI against evasion, poisoning, extraction, and inference attacks. Learn to evaluate and protect machine learning models before deployment.

CVSS Scores Are Dead - Let’s Explore 4 Alternatives
Explore limitations of CVSS scores and benefits of risk-based vulnerability scoring, examining alternatives like EPSS, SSVC, and VPR for more comprehensive threat assessment.
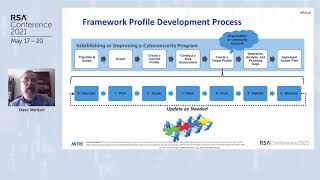
Three’s Company - Unpacking and Settling in with Three NIST Frameworks
Explore how NIST's Risk Management, Cybersecurity, and Privacy Frameworks complement each other to enhance enterprise risk management and improve organizational security posture.