
Hacking the Law - Are Bug Bounties a True Safe Harbor?
Explore the legal risks and challenges of bug bounty programs, examining potential liabilities for hackers and suggesting steps to create safer legal environments for vulnerability disclosure.
The SecDevOpronomicon - Arcane Secrets for Scaling Your Company’s Security
Uncover arcane secrets for scaling security efforts in fast-paced development environments. Learn high-value engineering techniques, custom analyses, and CI/CD pipeline integration to enhance SecDevOps practices.
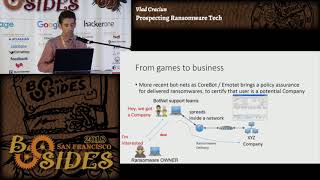
Prospecting Ransomware Tech
Análisis detallado de las tecnologías y tendencias de ransomware en 2017, explorando mezclas de técnicas maliciosas, métodos de propagación y algoritmos de cifrado utilizados por diversas familias de malware.
Machine Learning - Too Smart for its Own Good
Explore machine learning limitations through a steampunk model, revealing why neural nets generate false positives without complex mathematics.
Your Secrets are Showing - How to Find if Your Developers are Leaking Secrets
Discover tools and techniques to identify and prevent sensitive information leaks in source code repositories, both within corporate networks and on public platforms.
I Can Read Your Mind
Uncover mind-reading techniques used by psychics and con artists. Learn cold reading, body language interpretation, and verbal tricks to spot deception and even perform convincing "psychic" demonstrations.
Mapping the Penetration Tester's Mind - 0 to Root in 60 Min
Gain insight into penetration testing methodology, from project initiation to reporting. Learn how testers approach engagements and acquire knowledge to select the right professional for your security needs.
Hacking the Bank - Figuring Out What the Cost of Hacks May Be
Exploring the financial impact of cyber breaches, including accounting discrepancies, disclosure issues, and real-world case studies. Offers insights on improving cost estimation and accounting for hacking attacks.
The End of Security Stupidity
Experts discuss the end of ineffective practices in information security, predicting a shift towards more meaningful certifications, better training, and effective solutions to combat cyber threats.
Yet Another Type of Application Layer Denial of Service Attack
Explore a novel Application Layer DoS attack exploiting slow data acceptance by clients. Learn about attack vectors, detection methods, and mitigation strategies for this overlooked vulnerability.
Sharks in the Water - Open Source Component Risk and Mitigation
Explore open source component risks and mitigation strategies, focusing on supply chain vulnerabilities, recent hacks, and preventive measures through education and automated tooling.
Managing the Assets of Your Security Career
Strategies for career growth in cybersecurity: improving influence, visibility, and promotion chances through effective stakeholder management and asset tracking techniques.
How to 10X Your Company's Security - Without a Series D
Discover actionable strategies to dramatically enhance your company's security posture without significant financial investment. Learn from distilled insights and lessons from DevSecOps and modern AppSec experts.
What's New or Not in 2020 - Are We Making Progress on the Intractable Security Problems
Insightful keynote examining the progress and challenges in Information Security over the past decade, highlighting achievements and persistent issues facing professionals in the field.
2FA in 2020 and Beyond
Explore the modern 2FA landscape with data-driven analysis, comparing security strength and user experience of various authentication methods like SMS, soft tokens, push, and WebAuthn.
How to Write Like It's Your Job
Practical advice for security professionals on improving technical writing skills, from starting to finishing, with tools and tips for presenting professional work.
Privacy Nightmares while Using ML - AI in Your Applications
Explore privacy challenges in ML/AI applications and learn about a framework that integrates data security with machine learning technologies to address potential nightmares.
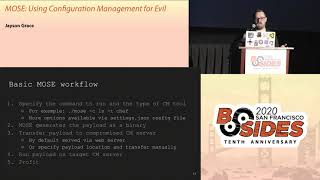
MOSE - Using Configuration Management for Evil
Explore MOSE, a post-exploitation tool for leveraging configuration management servers to compromise associated agents en masse, simplifying large-scale system takeovers.
K-Rail - A Tool to Manage K8s Securely at Speed
Explore offensive and defensive scenarios in Kubernetes security, and learn about k-rail, a tool for mitigating risks and managing configurations securely at scale.
Lessons from DevSecOps Trenches
Panel discussion with security team leads sharing insights on building and scaling security programs, exploring successes, failures, and practical strategies in DevSecOps implementation.
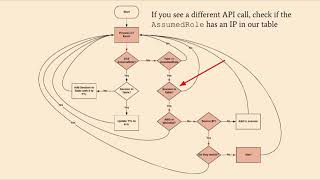
DevSecOps State of the Union
Comprehensive overview of DevSecOps best practices, tools, and methodologies. Distills insights from industry leaders to help AppSec teams improve security integration, automation, and culture.