A New Secret Stash For Fileless Malware
Explores advanced fileless malware techniques using Windows event logs for code hiding and infection. Reveals new methods to conceal shellcode and manipulate logging functions.
PAM Maturity From Zero Trust To Least Privilege
Panel discussion on PAM maturity, exploring the journey from zero trust to least privilege. Industry experts share insights on implementing effective privileged access management strategies in modern cybersecurity landscapes.
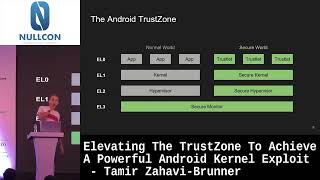
Elevating the TrustZone to Achieve a Powerful Android Kernel Exploit
Explore a novel Android kernel exploitation technique using TrustZone to bypass security mitigations, achieve 100% reliability, and create a versatile exploit applicable across devices and versions.
Software Defined Snort With Barnyard & Pulled Pork For NIDPS
Explore software-defined networking for enhanced network security, focusing on DDoS defense and traffic programming using Snort and its dependencies to mitigate WAF bypass attempts.
Unlocking Security Collaboration With Cyber Threat Intelligence
Panel discussion exploring how CXOs can leverage cyber threat intelligence for enhanced security collaboration and proactive defense strategies in today's evolving threat landscape.
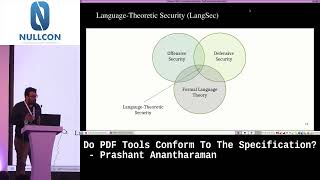
Do PDF Tools Conform to the Specification
Explore a novel type checker enforcing PDF specifications, uncovering deviations in tools and contributing to improvements in the PDF 2.0 standard. Learn about SPARTA and PDFFixer for enhanced PDF file management.
Cloud Services for Financial Inclusion - Possibilities and Challenges
Panel discussion exploring cloud services' potential and challenges for financial inclusion, featuring insights from cybersecurity experts and industry leaders.

Raining CVEs on WordPress Plugins with Semgrep
Leveraging Semgrep to identify vulnerabilities in WordPress plugins, reducing false positives, and automating XSS validation. Includes demos on custom rule creation and the XSSBomb tool.
Consumer Bug Bounty Panel - Tech Bug Bounty Panel - Hear from the Program Managers
Panel discussion with program managers sharing insights on running bug bounty programs, challenges faced, and best practices for organizations.
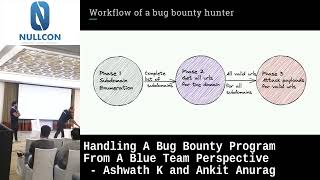
Handling a Bug Bounty Program from a Blue Team Perspective
Strategies for blue teams to manage bug bounty programs effectively, balancing security needs with researcher experience. Focuses on mitigating operational risks and optimizing defense rules for real threats.
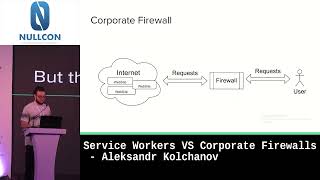
Service Workers vs Corporate Firewalls
Explore how service workers can be exploited to bypass corporate firewalls, potentially compromising network security. Learn about this innovative attack vector and its implications.
Wohnungsbot - An Automation-Drama in Three Acts
Explora la automatización de la búsqueda de viviendas en Berlín, cuestionando las relaciones de poder en plataformas online y desafiando narrativas sobre la automatización y sus implicaciones sociales.
Quantum Computing - Are We There Yet?
Explore quantum computing progress, including Google's recent breakthrough, and learn about quantum gates, error correction, and future challenges in building large-scale quantum computers.
Jahresrückblick der Haecksen
Jahresrückblick der Haecksen: Von Femiziden zur Hexenverbrennung, positive Entwicklungen, Kunstgalerie, Integration neuer Mitglieder, Aktivitäten in Chaos-Gruppen und Vorstellung von NIFTI als zentraler Knotenpunkt für FNIT-Gruppen.
Understanding Millions of Gates
Explore IC reverse engineering techniques, focusing on understanding logical gates in chips. Learn about industry motivations, research methods, and potential countermeasures in this accessible introduction.
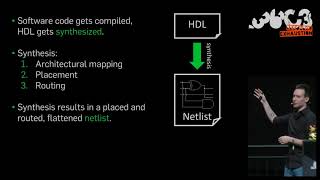
HAL - The Open-Source Hardware Analyzer
Einführung in Hardware-Reverse-Engineering und Vorstellung von HAL, dem ersten Open-Source-Framework zur Analyse von Netzlisten für die Erkennung von Hardware-Manipulationen und Backdoors.
Boot2root - Auditing Boot Loaders by Example
Auditing boot loaders: exploring attack surfaces in secure boot chains, from network protocols to local filesystems. Insights on common vulnerabilities and realistic compromise scenarios.
Unvorstellbare Einzelfälle und neue Phänomene - Kontinuitäten des rechten Terrors
Analyse der Kontinuitäten rechtsextremen Terrors seit 1945, Aufzeigen von Gemeinsamkeiten und Handlungsmöglichkeiten gegen aktuelle Bedrohungen durch rechte Gewalt.
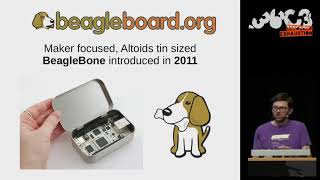
Linux on Open Source Hardware with Open Source Chip Design
Explore open hardware projects for Linux, including BeagleBone and OLinuXino. Learn about RISC-V and free FPGA toolchains for creating libre systems and running Linux on open source chip designs.
15 Jahre Deutsche Telematikinfrastruktur - TI
Überblick und kritische Analyse der deutschen Telematikinfrastruktur nach 15 Jahren Entwicklung: Fortschritte, Herausforderungen und Sicherheitsaspekte der digitalen Vernetzung im Gesundheitswesen.
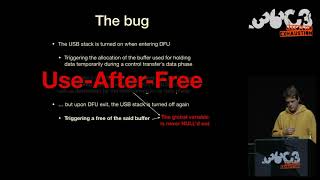
The One Weird Trick SecureROM Hates
Explore the unfixable Checkm8 vulnerability in iPhones' SecureROM, its exploitation for jailbreaking, and implications for iOS security research and device control.