Injecting Security into Web Apps
Explore innovative approaches to web application security beyond traditional WAFs, focusing on internal application monitoring and real-time threat detection to prevent zero-day attacks and data exfiltration.
Hackers - Do We Shoot or Do We Hug?
Exploring the evolving perception of hackers, from threats to potential allies. Discusses bug bounty programs, responsible disclosure, and how companies can leverage hacker expertise for improved security.
Social Engineering - Setting People into Debug Mode
Explore social engineering tactics and their impact on corporate security, drawing insights from real-world hacks and competition experiences to understand vulnerabilities beyond technological solutions.
Are You Watching TV Now? Is It Real?
Análisis de vulnerabilidades en smart TVs con WebOS: estructura, vectores de ataque y escenarios de hacking demostrados en LG WebOS TV.
How to Measure Your Security
Discover techniques to measure and compare the effectiveness of security tools, holding vendors accountable. Learn to evaluate IDS, IPS, A/V, and other detection systems for better cybersecurity decision-making.
The Forbidden Image - Security Impact of SVG on the WWW
Explore SVG's security implications, potential vulnerabilities, and protective measures. Learn about malicious SVG examples and a new filtering tool for safer SVG usage on the web.
A Close Look at Rogue Antivirus Programs
Comprehensive analysis of rogue security software, examining characteristics, behavioral patterns, and potential benefits. Explores methods to differentiate from legitimate antivirus programs and investigates the financial aspects behind these products.
Skirack ROP for Masses
Practical introduction to ROP exploitation technique, demonstrating bypass of DEP and ASLR. Includes tool showcase for efficient ROP payload generation.
Project Quebec and Win32 Exploit Development with Pvefindaddr
Explore pvefindaddr plugin for Immunity Debugger, automating Win32 exploit development tasks. Preview Project Quebec's optimizations and new features for enhanced performance.
Locking the Throne Room - ECMA Script 5, a Frozen DOM and the Eradication of XSS
Innovative approach to prevent XSS attacks using ECMA Script 5 features, sealing DOM properties and creating client-side IDS/IPS systems for modern browsers.
Cyberwar 4G - The Coming Smartphone Wars
Explores the challenges of cybersecurity in the era of smartphones, discussing potential threats, government responses, and the need for new defense strategies against mobile-based attacks.
Defensive Nature
Engaging panel discussion featuring cybersecurity experts exploring defensive strategies and the nature of digital threats in today's interconnected world.

Attacking XML Processing
Explore XML security vulnerabilities, from browsers to enterprise solutions. Learn about DTD, SVG, XSLT, XPath, and XML databases, with practical examples and PoC code.
Where Are We and Where Are We Going
Explore cybersecurity's past, present, and future with Mikko Hypponen. Delve into malware evolution, criminal tactics, governmental attacks, and emerging threats in this insightful keynote address.
Got Your Nose - How to Steal Your Precious Data Without Using Scripts
Discover sophisticated browser attacks that bypass traditional security measures, stealing sensitive data without using scripts. Learn about markup-based techniques that evade common protections.
HTML5 Something Wicked This Way Comes
Exploring HTML5's security vulnerabilities and advanced UI-Redressing techniques, demonstrating how attackers can exploit seemingly minor flaws in web applications for malicious purposes.
Weapons of Max Destruction
Análisis detallado de Stuxnet y Flame como armas cibernéticas avanzadas, su impacto en la seguridad estatal y las implicaciones para futuros conflictos cibernéticos.
Securing the Internet - You're Doing It Wrong
Strategies for effective cybersecurity communication: engaging management, empowering employees, and fostering industry collaboration to create a more secure digital environment.
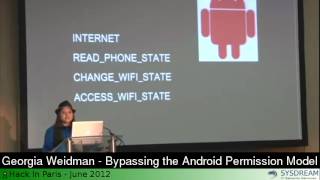
Bypassing the Android Permission Model
Explore techniques to bypass Android's permission model, including exploiting insecure storage and interfaces. Learn about security risks and mitigation strategies for developers and users.
Results of a Security Assessment of the Internet Protocol Version 6
Comprehensive security assessment of IPv6 protocol suite, highlighting vulnerabilities, implementation challenges, and best practices for secure deployment in modern networks.
A Bit More of PE
Explore the intricacies and limits of the PE format, uncovering its peculiarities and pushing boundaries in this detailed examination of file structure weirdness.