Point-of-Sale Malware
Explore point-of-sale malware threats, attack vectors, and defense strategies in this informative webcast. Gain insights to protect retail systems and customer data.
Owning the Routing Table - Part II
Powerful OSPF attack exploiting protocol ambiguity to control routing tables in autonomous systems. Enables network manipulation, DoS, and unauthorized access to information flows. Multi-vendor fix underway.
Spy-Jacking the Booters
Exposé on "booter" DDoS-for-hire services: their operations, vulnerabilities, and impact. Insights into defending against attacks and the criminal ecosystem behind these illicit services.
Hacking, Surveilling, and Deceiving Victims on Smart TV
Explore vulnerabilities in Smart TVs, including remote surveillance and deception techniques. Learn about potential security risks and attack vectors in this emerging technology platform.
Revealing Embedded Fingerprints - Deriving Intelligence - USB Stack Interactions
Techniques for analyzing USB stack interactions to gather intelligence on embedded systems, including OS identification and vulnerability exploitation challenges.
Home Invasion v2.0 - Attacking Network-Controlled Hardware
Explore security risks of network-connected home devices, including potential for physical access and surveillance. Learn about vulnerabilities in smart locks and other IoT products.
Fully Arbitrary 802.3 Packet Injection - Maximizing the Ethernet Attack Surface
Explore novel Ethernet attack techniques using affordable hardware and custom firmware. Learn about frame manipulations, SFD parsing anomalies, and Ethernet Packet-In-Packet injection for enhanced network security testing.
RFID Hacking - Live Free or RFID Hard
Practical guide on RFID hacking techniques, tools, and defenses. Learn to build custom long-range RFID hacking tools using Arduino, steal badge info, clone cards, and exploit vulnerabilities in proximity badge systems.
Rooting SIM Cards
Explore SIM card vulnerabilities and their impact on mobile security. Learn about implementation flaws, potential exploits, and the implications for trusted computing in smartphones and embedded devices.
Truncating TLS Connections to Violate Beliefs in Web Applications
Exploring TLS truncation attacks to exploit web application flaws, demonstrating vulnerabilities in authentication systems and their impact on popular platforms like Helios, Microsoft Live, and Google.
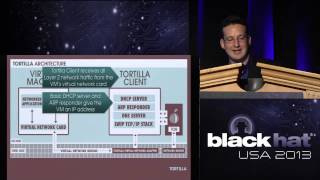
TOR - All the Things
Explore Tortilla, a new tool for securely routing all TCP/IP and DNS traffic through Tor on Windows, enabling anonymous use of any program without additional hardware or VPNs.
BIOS Security
Explore BIOS security vulnerabilities, SRTM manipulation, and trust subversion techniques. Learn about NIST standards and academic solutions for ensuring BIOS integrity.
Just-In-Time Code Reuse - The More Things Change, the More They Stay the Same
Explore advanced exploit techniques undermining fine-grained ASLR through just-in-time code reuse, demonstrating real-world applications and implications for cybersecurity defenses.
Combating the Insider Threat at the FBI - Real World Lessons Learned
Insider threat detection at FBI: multidisciplinary approach combining psychology, technology, and analytics. Lessons from real-world program implementation, focusing on deterrence, behavioral analysis, and predictive techniques.
Compromising Industrial Facilities From 40 Miles Away
Explore vulnerabilities in industrial wireless automation systems, revealing how key distribution weaknesses can be exploited to compromise critical infrastructure from long distances.
Out of Control - Demonstrating SCADA Device Exploitation
Explore SCADA device exploitation in oil and gas pipelines, examining control systems, vulnerabilities, and potential consequences of security breaches in critical infrastructure.
The Outer Limits - Hacking the Samsung Smart TV
Explore vulnerabilities in Samsung Smart TVs, including remote hijacking, userland rootkits, and surveillance capabilities. Learn about attack surfaces, security flaws, and potential fixes for smart platforms.
KickaaS Security with Automation and Cloud
Explore cutting-edge security automation techniques for cloud environments, focusing on resource management, host protection, and identity control.
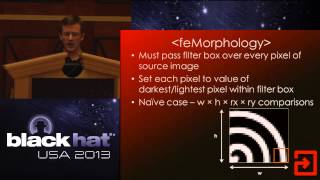
Pixel Perfect Timing Attacks with HTML5
Exploring JavaScript timing attacks to extract sensitive browser data, demonstrating cross-browser vulnerabilities and discussing challenges in fixing these security issues.
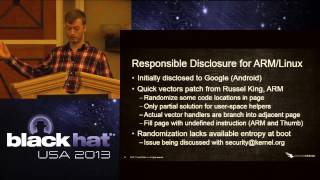
Hacking Like in the Movies - Visualizing Page Tables for Local Exploitation
Visualizing page tables to break ASLR and find vulnerabilities across operating systems. Includes an Android ASLR bypass and insights for Windows, Linux, and iOS.
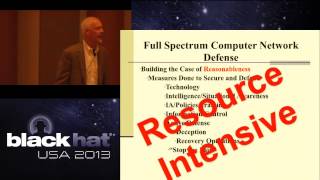
Legal Aspects of Full Spectrum Computer Network - Active Defense
Explores legal implications of active cyber defense, covering technology, information control, and controversial practices. Emphasizes importance of collaboration between security professionals and legal counsel.