Windows 8 Heap Intervals
Explore Windows 8 heap exploitation techniques, memory management changes, and security features. Learn about user-land and kernel-land perspectives, allocation processes, and mitigation strategies.
The Christopher Columbus Rule and DHS
Explore DHS's innovative cybersecurity initiatives, including threat information sharing, research funding, and career opportunities in this talk by Deputy Under Secretary Mark Weatherford.
The Subway Line 8 - Exploitation of Windows 8 Metro Style Apps
Exploring Windows 8 Metro-style app security, AppContainer sandbox, and potential vulnerabilities. Demonstrates techniques to bypass security measures and access restricted resources.
Trust, Security, and Society
Explore trust in society, its importance, and various systems to maintain it. Delve into societal pressures, cooperation strategies, and challenges in our interconnected world.
We Have You by the Gadgets
Explore Windows gadget platform vulnerabilities and attack vectors. Learn about creating malicious gadgets, exploiting legitimate ones, and uncovering flaws in published gadgets.
Hacking with WebSockets
Explore WebSocket vulnerabilities, privacy implications, and security risks. Learn to deploy WebSockets securely and use them in hacking frameworks. Gain insights into HTML5 security challenges.
HTML5 Top 10 Threats - Stealth Attacks & Silent Exploits
Explores top 10 HTML5 security threats, including CORS attacks, clickjacking, XSS, web storage vulnerabilities, and more. Demonstrates real-life examples and discusses defense strategies against emerging attack vectors.
The Info Leak Era on Software Exploitation
Explore advanced techniques for exploiting software vulnerabilities through information leaks, focusing on defeating ASLR and converting various vulnerabilities into effective info leaks.
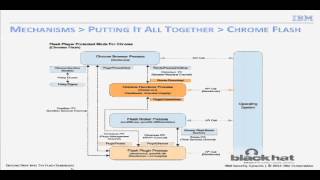
Digging Deep Into the Flash Sandboxes
Explore Flash Player sandbox implementations, their architectures, mechanisms, and security limitations. Learn about potential vulnerabilities and sandbox escape techniques in this in-depth analysis.
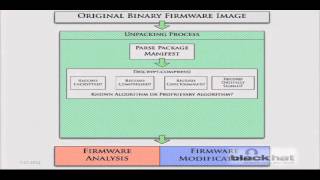
Here Be Backdoors - A Journey into the Secrets of Industrial Firmware
Exploring vulnerabilities in industrial control systems through firmware analysis, revealing backdoors and security flaws in critical infrastructure devices like PLCs, smart meters, and SCADA systems.
When Security Gets in the Way - Pen Testing Apps That Use Certificate Pinning
Explore tools and techniques for defeating certificate pinning in mobile apps during black-box testing, enabling interception of SSL traffic on both iOS and Android platforms.
How Many Bricks Does It Take to Crack a Microcell
Journey through reverse engineering a 3G microcell, covering hardware hacking, kernel reversing, firmware manipulation, software reversing, networking, memory forensics, and social engineering. Insights into successes, failures, and lessons learned.
Hacking the Corporate Mind - Using Social Engineering to Improve Organizational Security Acceptance
Discover social engineering techniques to improve organizational security acceptance, bridging the gap between users and InfoSec teams for better awareness and policy adherence.
PinPadPwn
Explore vulnerabilities in payment terminals, including memory corruption issues and potential attack vectors. Learn about code execution risks and discuss profitable payloads for attackers.
Windows Phone 7 Internals and Exploitability
Comprehensive analysis of Windows Phone 7 security, revealing hidden internals through reverse engineering. Explores potential vulnerabilities and exploitation techniques in the OS and vendor customizations.
Hardware Backdooring is Practical
Explores hardware backdooring through Rakshasa malware, demonstrating permanent BIOS infection, NX bit disabling, and security lowering across various motherboards using open-source components like Coreboot.

SSRF vs Business Critical Applications
Explore SSRF vulnerabilities in business-critical applications, focusing on SAP systems. Learn about XXE Tunneling and its potential to bypass security restrictions, with practical examples and attack scenarios.
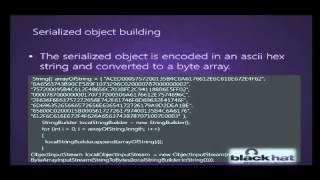
Recent Java Exploitation Trends and Malware
Explore recent Java vulnerabilities, exploitation techniques, and malware trends. Learn about sandbox evasion, multi-platform attacks, and challenges in analyzing obfuscated Java exploits.
CuteCats.exe and the Arab Spring
Analysis of malware targeting activists during Middle Eastern uprisings, exploring distribution methods and impact on digital dissent and online communities.
Smashing the Future for Fun and Profit
Visionary security experts discuss emerging threats, technological shifts, and societal impacts on cybersecurity over the next 15 years, offering insights into future challenges and opportunities in the field.
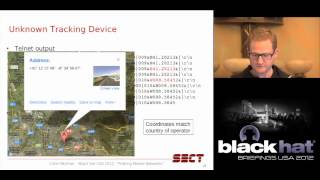
Probing Mobile Operator Networks
Explore techniques for probing cellular networks, uncovering diverse connected devices, and discussing security implications of findings from network investigations.