Passive Bluetooth Monitoring in Scapy
Explore passive Bluetooth monitoring in Scapy using Python extensions and Ubertooth dongle, enabling interactive observation and development of Bluetooth auditing and pentesting tools.
Web Tracking For You
Explore advanced web tracking techniques for identifying and monitoring potential security threats, covering active and passive fingerprinting, user unmasking, and cross-platform implementation.
iOS Application Security Assessment and Automation - Introducing SIRA
Automated iOS app security assessment tool SIRA demonstrated, revealing common flaws in AppStore products. Explores risks, testing methods, and future improvements for mobile app security.
SQL Injection to MIPS Overflows - Rooting SOHO Routers
Explore SQL injection techniques to exploit buffer overflows and gain root access to Netgear routers, including file extraction and live demonstration of vulnerabilities in SOHO devices.
Ghost is in the Air - Traffic - Security Aspects of ADS-B and "Flying" Technology
Explore security vulnerabilities in ADS-B technology and potential threats to air traffic control systems, including practical demonstrations of data injection and visualization techniques.
Legal Aspects of Cyberspace Operations
Explore legal frameworks for cyberspace operations, including network security, defense, exploitation, and attack. Gain insights into recent incidents and their legal classifications.
Easy Local Windows Kernel Exploitation
Discover reliable techniques for exploiting common local Windows kernel vulnerabilities across multiple versions, including previously challenging exploits.
Torturing OpenSSL
Explore hardware vulnerabilities in secure systems through a side-channel attack on RSA signatures, demonstrating how induced faults can compromise software-secure systems and extract private keys.
Sexy Defense - Maximizing the Home-field Advantage
Proactive defense strategies: intelligence gathering, modeling, and expanding defender roles. Maximize existing resources for effective security posture against penetration testers and red teams.
PRNG Pwning Random Number Generators in PHP Applications
Techniques for exploiting randomness vulnerabilities in PHP applications, focusing on password reset token predictability and demonstrating account takeover through PRNG prediction.
How Analysis of EC Consumption of Embedded Systems Could Lead to Code Reversing
Practical approach to reverse engineering embedded systems through power analysis. Explores experimental protocol, tools, and techniques for extracting code without physical access to internal components.
Exploiting the Jemalloc Memory Allocator - Owning Firefox's Heap
Explore jemalloc memory allocator's architecture, attack vectors, and novel exploitation techniques, focusing on Mozilla Firefox's heap and its security implications.
Targeted Intrusion Remediation - Lessons From The Front Lines
Explore strategies for combating persistent cyber threats, focusing on inhibiting attacker activities, enhancing detection capabilities, and improving rapid response techniques for effective intrusion remediation.
Owning Bad Guys and Mafia with Javascript Botnets
Explore mitm attacks on anonymous services and learn to create JavaScript botnets for analyzing connections, uncovering activities of malicious actors behind these services.
Don't Stand So Close To Me - An Analysis of the NFC Attack Surface
Explora la seguridad de NFC en dispositivos móviles, analizando protocolos, vulnerabilidades y posibles ataques. Incluye demostraciones prácticas de explotación y recomendaciones para mejorar la protección.
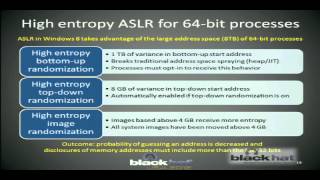
Exploit Mitigation Improvements in Windows 8
Explore Windows 8's advanced security features and exploit mitigation improvements, including enhanced ASLR, heap protection, and kernel safeguards, designed to thwart modern attack techniques.
File Disinfection Framework - Striking Back at Polymorphic Viruses
Explore an open-source framework for combating polymorphic viruses through advanced static analysis and emulation. Learn innovative techniques for file disinfection, malware analysis, and incident response.
Find Me in Your Database - An Examination of Index Security
Explore Oracle indexing architecture, new flaws, and forensic aspects. Learn to identify issues in custom applications and understand the security implications of database indexing.
Errata Hits Puberty - 13 Years of Chagrin
Exploring the attrition.org Errata project's 13-year journey as an IT and security industry watchdog, including insights into its history, process, impact, and future direction.
eEye BootRoot
Explore advanced rootkit techniques and boot-level system manipulation with eEye BootRoot, presented by security experts Derek Soeder and Ryan Permeh.
Attacking Web Services - Next Generation of Vulnerable Enterprise Apps
Explore vulnerabilities in enterprise web services and learn advanced techniques for identifying and exploiting security flaws in next-generation applications.