AttackGNN: Red-Teaming GNNs in Hardware Security Using Reinforcement Learning
Discover how reinforcement learning can generate adversarial examples to challenge GNN-based hardware security systems, demonstrating vulnerabilities in IP piracy detection and Trojan identification methods.
Shesha: Multi-head Microarchitectural Leakage Discovery in New-generation Intel Processors
Discover how Shesha framework automates detection of transient execution attacks in Intel processors, exploring new vulnerabilities in instruction set extensions and cryptographic implementations.
ZenHammer: Rowhammer Attacks on AMD Zen-based Platforms
Discover the first successful Rowhammer attack implementation on AMD Zen processors, exploring reverse engineering techniques, synchronization methods, and exploitation of DDR4/DDR5 memory vulnerabilities.
Formalizing and Benchmarking Prompt Injection Attacks and Defenses
Explore a systematic framework for understanding and evaluating prompt injection attacks on LLM applications, including analysis of 5 attack types and 10 defense mechanisms across multiple models.
BUDAlloc: Defeating Use-After-Free Bugs by Decoupling Virtual Address Management from Kernel
Discover how BUDAlloc improves memory safety by detecting use-after-free bugs through virtual address management separation, offering better performance and reduced memory overhead compared to existing solutions.
Go Go Gadget Hammer: Flipping Nested Pointers for Arbitrary Data Leakage
Explore a novel Rowhammer exploit technique targeting nested pointer dereferences in code patterns, demonstrating enhanced data leakage capabilities and improved attack primitives in Linux kernel security.
Attacks on Shared State in Multi-User Augmented Reality Applications
Explore security vulnerabilities in multi-user AR applications, focusing on shared state attacks, their implications, and potential defense strategies for protecting augmented reality frameworks.
SpecLFB: Eliminating Cache Side Channels in Speculative Executions
Discover how SpecLFB leverages Line-Fill-Buffer to eliminate cache side-channel vulnerabilities in speculative executions, offering an efficient defense mechanism with minimal performance impact.
A Binary-level Thread Sanitizer - Why Sanitizing on the Binary Level is Hard
Explore the challenges and solutions of binary-level thread sanitization through BINTSAN, a novel approach for detecting data races in Linux x86-64 targets without source code access.
Yes, One-Bit-Flip Matters! Universal DNN Model Inference Depletion with Runtime Code Fault Injection
Explore FrameFlip, a groundbreaking attack method that depletes DNN model inference through single-bit fault injections, demonstrating universal effectiveness across major machine learning frameworks.
DMAAUTH: A Lightweight Pointer Integrity-based Secure Architecture to Defeat DMA Attacks
Explore a lightweight pointer integrity-based architecture that provides enhanced DMA attack protection while maintaining performance, demonstrated through FPGA implementation and cross-architecture evaluation.
Measuring Structural Limitations of Deepfake Media Datasets - A Systematic Review
Explore structural limitations in deepfake media datasets, examining metrics, generation techniques, and class distributions to understand their impact on detection systems and research reproducibility.
A Taxonomy of C Decompiler Fidelity Issues
Explore a comprehensive analysis of C decompiler output fidelity issues, examining defects beyond missing names and types to improve reverse engineering effectiveness in security analysis.
What IF Is Not Enough? Fixing Null Pointer Dereference with Contextual Check
Discover how CONCH improves null pointer dereference fixes by incorporating contextual checks, achieving 85%+ patch accuracy through innovative intraprocedural and interprocedural analysis techniques.
Neural Network Extraction Through Physical Side Channels - A Systematic Review
Explore physical side-channel analysis attacks on deep neural networks, examining threat models, attack methodologies, and practical limitations for model extraction and input recovery on hardware accelerators.
Exploiting Online Games - Security Issues in MMORPGs and Virtual Economies
Delve into online gaming security vulnerabilities, cheating mechanisms, and protective measures with insights from gaming security expert Gary McGraw, exploring privacy concerns and bot creation in MMORPGs.
Dr. Strangevote - How I Learned to Stop Worrying and Love the Paper Ballot
Explore California Secretary of State Debra Bowen's compelling analysis of electronic voting systems and her advocacy for paper ballots as a secure, reliable voting method.
Computer Security and Electronic Voting Systems - Security Challenges and Solutions
Explore the critical intersection of computer security and electronic voting systems through expert insights on vulnerabilities, verification technologies, and essential safeguards for trustworthy elections.
A World Where We Trust Hard-Won Lessons in Security Research, Technology, and People
Discover key principles for transforming security research into real-world impact, bridging academic innovation with practical implementation through hard-won lessons and case studies in software safety.
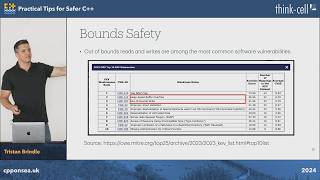
Practical Tips for Safer C++ - Writing Bug-Free and Efficient Code
Discover practical strategies for writing safer, more reliable C++ code without compromising performance, featuring expert techniques for bug detection and prevention in everyday programming.
What We Can Learn from Aviation Industry Security Controls
Explore fascinating parallels between aviation safety and cybersecurity principles, drawing insights from air crash investigations to enhance security control implementations and risk management.