Scaling the Security Wall: Agile Threat Modeling for Complex Systems
Discover practical approaches to agile threat modeling for large-scale systems, focusing on cloud architectures, SDLC integration, and cost-effective security strategies.
Physical Attacks Against Smartphones: Android Security Vulnerabilities and Exploits
Discover physical attack vulnerabilities in Android smartphones, from Recovery mode exploits using SD cards to USB stack weaknesses in secondary bootloaders for achieving root access and code execution.
Retro Exploitation - Vintage Computing as a Vulnerability Research Playground
Explore vulnerability research and exploit development through vintage computing, focusing on the Commodore Amiga platform and practical demonstrations of retro software exploitation techniques.
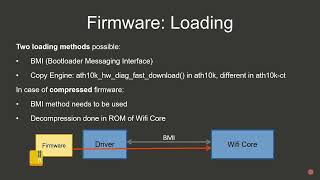
Unlocking Hidden Powers in Xtensa-based Qualcomm WiFi Chips
Dive into firmware modification techniques for Xtensa-based Qualcomm WiFi chips, exploring architecture, patching methods, and security research possibilities using the Nexmon framework.
Revolutionizing ELF Binary Patching with Shiva - Advanced Techniques and Solutions
Discover revolutionary ELF binary patching with Shiva - a JIT system enabling developers to write complex patches in C code, transforming how we maintain and secure legacy software without source code access.
Getting a Migraine - Unique System Integrity Protection Bypass on macOS
Delve into advanced MacOS security exploitation, exploring System Integrity Protection bypass techniques, undeletable malware creation, and essential detection strategies for security teams.
Backdoor in the Core - Altering Intel x86 Instruction Set at Runtime
Dive into groundbreaking research on Intel CPU microcode manipulation, exploring techniques for persistent modifications and potential security implications through microcode backdoors in x86 instruction sets.
Attacking and Securing the Google Pixel Modem - Security Analysis and Vulnerabilities
Dive into mobile security as Android Red Team reveals their offensive evaluation techniques and findings on Pixel device modems, focusing on baseband vulnerabilities and protective measures.
Abusing CAN Bus Specifications for DoS Attacks in Embedded Systems
Explore CAN bus protocol vulnerabilities in automotive systems, focusing on how attackers can exploit metadata fields and protocol specifications to create denial-of-service attacks in embedded systems.
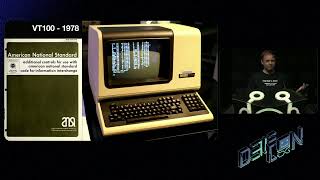
Terminally Owned - 60 Years of Terminal Escape Code Vulnerabilities
Explore terminal security vulnerabilities across platforms, from ASCII's escape character origins to modern exploit techniques, revealing critical remote code execution risks and defense strategies.
Breaking BMC: The Forgotten Key to the Kingdom - Security Vulnerabilities in Baseboard Management Controllers
Dive into the security vulnerabilities of Baseboard Management Controllers (BMC), exploring exploit chains and firmware implants in NVIDIA hardware with AMI MegaRAC BMC implementation.
Bootsquad: Introduction to Secure Boot Exploitation and Defense
Dive into the world of cybersecurity and virtual reality as Joe Mast presents Bootsquad, exploring innovative security concepts and challenges in the DCGVR Village at DEF CON 31.
Bug Hunting in VMware Device Virtualization - Security Vulnerabilities and Attack Surfaces
Delve into VMware device virtualization security, exploring USB system vulnerabilities, SCSI device emulation, and VMKernel design flaws through real-world bug hunting experiences and discoveries.
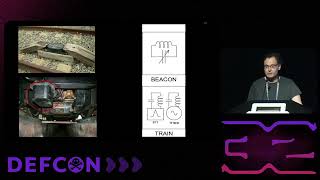
Abusing Legacy Railroad Signaling Systems - Security Vulnerabilities and Threats
Uncover critical vulnerabilities in railway signaling systems through an analysis of accessible hardware tools and their potential impact on train operations, with focus on Spanish infrastructure.
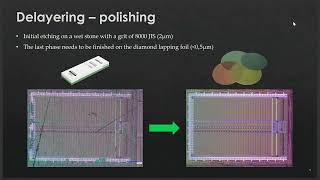
Nano Enigma: Uncovering the Secrets in eFuse Memories
Dive into the fascinating world of eFuse memory security, exploring physical extraction techniques from basic decapsulation to advanced SEM analysis for accessing encrypted data storage.
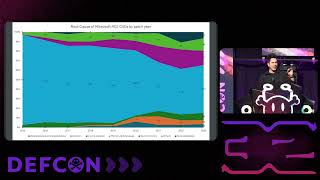
The Rise and Fall of Binary Exploitation - A Technical Analysis of Memory Safety and Exploit Mitigations
Explore the evolution of binary exploitation, memory safety challenges, and modern protection mechanisms in operating systems, focusing on Windows security mitigations and their effectiveness.
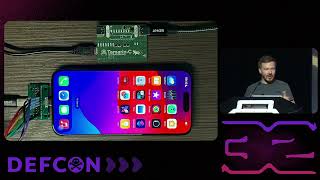
Hacking Apple's USB-C Controller: From JTAG Access to Code Execution on iPhone 15
Dive into advanced hardware hacking techniques to exploit Apple's ACE3 USB-C controller, using reverse engineering, side-channel analysis, and fault injection to gain code execution access on iPhone 15.
WHAD: A Framework for Wireless Protocol Hacking and Analysis
Discover WHAD, a versatile framework for wireless protocol hacking that enables hardware interoperability and simplified tool development for security researchers exploring wireless vulnerabilities.
Enabling Enterprises for DevSecOps Without Fighting the Silos - A Strategic Approach
Discover practical strategies for implementing DevSecOps in enterprise silos, focusing on people, processes, and tools to enhance business KPIs and foster cultural transformation.
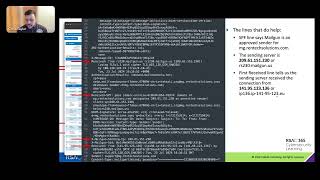
Digital Forensics and Technical Analysis of Phishing Email Campaigns
Dive into comprehensive digital forensics techniques for analyzing phishing emails, from examining suspicious attachments to investigating malicious websites and understanding SOC response protocols.
Product Security Topologies - Применение Team Topologies для повышения безопасности
Discover how to boost product security using Team Topologies framework, with practical examples for resolving inter-team conflicts and enhancing security practices in Agile environments.