Purple Teaming with OWASP PurpleTeam
Explore OWASP PurpleTeam: a security regression testing tool for web apps and APIs. Learn its journey, architecture, benefits, setup, and various workflows for effective implementation in build pipelines.
Why Checking Infrastructure-as-Code for Misconfigurations Is Not Enough - Comprehensive Cloud-Native Application Security
Explore comprehensive cloud-native app security beyond misconfigurations. Learn dynamic assessment techniques for robust architecture design and compliance in modern software development.
Automated Serverless Security Testing: Delivering Secure Apps Continuously
Explore serverless security risks, traditional testing limitations, and a new automated approach for secure serverless development without scripts or delays.
OWASP ZAP: Introduction to Web Application Security Testing
Explore OWASP ZAP's latest features, including automation, reporting, and out-of-band testing. Learn how this open-source tool enhances web application security through practical demonstrations and updates.
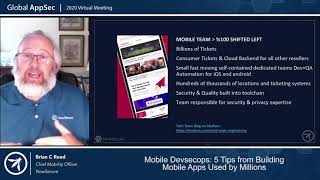
Mobile DevSecOps: 5 Tips for Building Secure Apps Used by Millions
Discover 5 essential tips for implementing Mobile DevSecOps, drawing insights from large-scale app development experiences to enhance security and efficiency in your mobile projects.

OAuth 2.0 and OpenID Connect for Single Page Applications
Explore OAuth 2.0 and OpenID Connect implementation for single-page applications, enhancing security and user authentication in modern web development.
Attacking Microservice Systems: Methods and Practical Tips
Discover methods and practical tips for attacking microservice systems, exploring new security architecture patterns and vulnerabilities specific to this increasingly popular design approach.
The Home Depot's Journey into Cloud Foundry Foundation - 6 Months In
Insights from The Home Depot's journey as a Cloud Foundry Foundation member, exploring strategies, successes, and lessons learned in adopting and contributing to the platform.
Serverless State of the Union - Adoption, Use Cases, and Future Trends
Explore serverless technology's impact, adoption methods, and future potential. Gain insights into open-source projects advancing serverless ecosystems and enabling interoperability.
Future of Tracing - Wish List Edition
Explore the future of tracing in software development with Steven Rosted's visionary insights and wish list for upcoming advancements in this critical field.
Using Coccinelle to Detect and Fix Nested Execution Context Violations
Explore techniques for detecting and fixing nested execution context violations using Coccinelle, enhancing code quality and reliability in Linux kernel development.
Building FAST Data Solutions with DC/OS on Azure
Learn to develop, deploy, and manage FAST data solutions using DC/OS on Azure. Explore stateful containers, Cassandra, Kafka, and third-party workflow management in this demo-rich session.
A Year with Apache Aurora - Lessons from Chartbeat's Migration
Insights on migrating to Apache Aurora for improved resource utilization, consistent deployments, and streamlined development workflow in a real-time web analytics platform.
Automatic Detection of Inadequate Authorization Checks in Web Applications
Automatic detection of missing authorization checks in web apps using static analysis. Explores techniques, real-world applications, and provides remediation suggestions for developers.
OWASP Broken Web Applications - Future Developments Beyond Version 1.0
Explore OWASP's virtual machine with 25+ vulnerable web applications for security training and testing. Learn about project features and future developments in web application security.
HTML5 - Security Risks and Tools in Modern Web Applications
Explore HTML5's security implications, from potential risks to innovative tools for enhanced authentication and session tracking. Learn how new features impact web application security.
Scripting Android Applications for Social Botnet Creation - Network Exploitation Techniques
Explore techniques for scripting Android applications, including APK manipulation, API exploitation, and creating realistic social botnets using JRuby sessions and network data.
OWASP PHP Security Project - Securing Web Applications with PHP Libraries and Tools
Explore secure PHP development with OWASP's project, featuring decoupled libraries and tools for enhanced web application security. Learn encryption, password management, and protection against common vulnerabilities.
How to Choose the Right Database for Your Microservices
Explore database selection strategies for microservices architecture, focusing on optimal performance, scalability, and data management in distributed systems.
Tips and Tricks - Protecting Cloud Infrastructure
Explore best practices for safeguarding cloud infrastructure, focusing on data protection, compliance, and risk management in Linux-based environments.
Building Embedded Drivers for Industrial Communication Using Code Generation
Learn to build embedded drivers for industrial communication using code generation techniques, focusing on challenges, MSpec examples, and integration testing.