Why Secure Development Programs Are Essential for Application Security
Explore integrating application security into development processes, focusing on proactive measures, resource allocation, and adapting to Agile and DevOps methodologies for effective risk management.
The Timing Attacks They Are A-Changin' - Web-based and Browser-based Timing Attack Techniques
Explore evolving timing attacks in web security, from classic cross-site techniques to browser-based methods, and learn effective mitigation strategies.
Making Security Agile in CI/CD Environments
Integrating security into agile development and CI/CD pipelines. Learn strategies to automate security processes, leverage QA tests, and utilize tools for improved productivity in application security.
Security Automation in the Agile SDLC - Real World Cases
Explore real-world examples of implementing successful security automation in fast-paced development environments, focusing on agile methodologies, DevOps, and continuous integration for secure software delivery.
Unlocking Threat Modeling - Participatory Session on Security Architecture Assessment
Participatory session demystifying threat modeling for security assessment. Learn risk evaluation, architectural decomposition, and appropriate views to enhance system security from the start.
Serverless Security for DevOps and Defenders
Explore serverless architecture's impact on DevOps and security with James Wickett. Learn how this emerging technology enhances defense strategies and streamlines development processes.
Continuous Security: Bringing Agility to the Secure Development Lifecycle
Bringing agility to secure development: Learn strategies for integrating continuous security practices into your development lifecycle, enhancing both speed and safety in software creation.
An SDLC for the DevSecOps Era
Explore an SDLC tailored for the DevSecOps era with insights on integrating security into modern development practices and organizational culture.
Dissecting Browser Privacy
Explore browser privacy with a senior security engineer from Brave, covering key issues and advancements in protecting user data while browsing the web.
Containerizing Your Security Operations Center
Explore containerizing security operations for improved deployment, maintenance, and collaboration. Learn to build a cloud-based SOC using containers, enhancing visibility and streamlining security workflows.
HTTPS and TLS Security Practices - Front Line Insights 2016
Comprehensive overview of modern HTTPS and TLS security practices, covering protocol vulnerabilities, certificate fundamentals, and best practices for implementing strong encryption in web services.
Everything is Terrible: Building, Configuring, and Securing Software - Three Perspectives
Explore perspectives on building, configuring, and securing software from developers, operations, and security experts. Learn strategies for collaboration, empathy, and optimizing workflows across teams.
Implementing a User-Centric Datastore with Privacy-Aware Access Control for Cloud-Based Data Platforms
Explore user-centric data storage with privacy-aware access control for cloud platforms. Learn about implementation, components, and challenges in this informative talk on secure data management.
Continuous Acceleration: Why Continuous Everything Requires a Supply Chain Approach
Explore the need for a supply chain approach in continuous development practices, emphasizing acceleration and efficiency in modern software security and delivery processes.
Rise of the Machines - How Automated Processes Overtook the Web
Explore how automated processes have dominated web interactions, their impact on security, and strategies to protect against machine-driven threats in modern web environments.
Building a Modern Security Engineering Organization
Practical insights on building modern AppSec and NetSec programs, launching bug bounties, and conducting realistic attack simulations in the era of continuous deployment and DevOps.
Why Your AppSec Experts Are Killing You - Evolving to Continuous Application Security
Explore how to evolve into a "Continuous Application Security" organization using instrumentation-based testing, real-time feedback loops, and innovative tools for improved DevOps integration and portfolio-wide assurance.
SQLViking - Pillaging Your Data
Explore SQLViking, a tool for passive SQL query logging and active TCP injection attacks on databases. Learn about network security vulnerabilities and potential countermeasures.
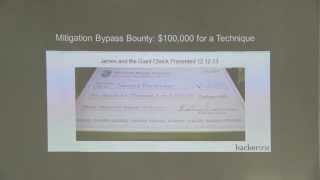
Bounties and the Software Development Life Cycle
Katie Moussouris explores bug bounties, vulnerability disclosure, and their integration into the software development lifecycle. She shares insights on organizational empathy, bounty program implementation, and improving application security.
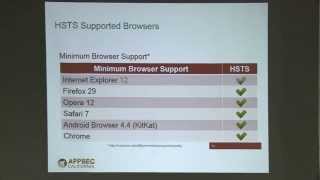
Proactively Defending Your Business Against Security Protocol Attacks - OWASP AppSec California 2015
Explore strategies to proactively defend against security protocol attacks and implementation flaws in HTTPS/SSL/TLS. Learn about recent vulnerabilities, mitigations, and best practices for secure communications.
Medical Device Security: An Infectious Disease - Risks and Vulnerabilities
Explore vulnerabilities in medical devices and healthcare systems, examining potential risks to patient safety and discussing strategies for improving security in the healthcare landscape.