Good Bot, Bad Bot: Characterizing Automated Browsing Activity
Explore Aristeus, a system for deploying honeysites to study malicious bot behavior. Learn about bot traffic patterns, attack strategies, and the importance of understanding automated browsing activity for web security.
Threat Modeling the CI/CD Pipeline to Improve Software Supply Chain Security
Explore threat modeling for CI/CD pipelines to enhance software supply chain security, covering key vulnerabilities, data flow analysis, and mitigation strategies.
Security Chaos Engineering - Turning the Tide in the War on Uncertainty in Cyber Security
Explore security chaos engineering to proactively discover system weaknesses, increase confidence in security mechanisms, and move from subjective assessment to objective measurement through continuous experimentation.
DevSecOps in 2031: How Robots and Humans Will Secure Apps Together
Explore the future of DevSecOps in 2031, where humans and robots collaborate to secure applications. Learn about AI pair programming and innovative approaches to tackle evolving cybersecurity challenges.
Topics of Interest: Developers Struggle with Application Security and How to Make It Better
Explore challenges in application security for developers and learn strategies to improve DevSecOps practices, drawing from real-world experiences at major tech companies.
Securing the Build and Deployment Pipeline - Challenges and Best Practices
Explore challenges in securing build/deployment environments for agile development and DevOps. Learn about potential vulnerabilities in automated processes and strategies to maintain code integrity.
Hack Your APIs in 15 Minutes or Less - Exploiting Shadow APIs and Data Vulnerabilities
Learn to identify and exploit API vulnerabilities, understand hacker techniques, and explore creative methods for data theft in this eye-opening talk on modern cybersecurity challenges.
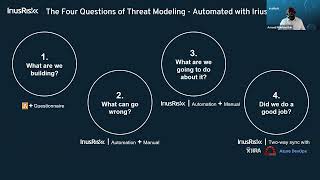
Using IAC to Accelerate Threat Modeling
Explore innovative techniques for accelerating threat modeling using Infrastructure as Code (IAC), enhancing security practices in software development and deployment.
How to Have Visibility and Security of a CI/CD Pipeline
Discover strategies for enhancing visibility and security in CI/CD pipelines, focusing on best practices and tools to safeguard your software development lifecycle.
The Power of DevSecOps in Web3 and Blockchain
Explore DevSecOps principles in Web3 and blockchain, focusing on security integration for decentralized applications and smart contracts development.
Docker for Pentesters
Learn essential Docker techniques for penetration testing, enhancing your cybersecurity skills and improving your ability to identify vulnerabilities in containerized environments.
OWASP WrongSecrets - We Have a Secret for Everyone
Explore common pitfalls in secret management and learn best practices for securing sensitive information in various environments, from local setups to cloud deployments.
Layered Threat Modeling: An Architectural Approach
Explore architectural threat modeling techniques to identify and mitigate security risks in complex systems, enhancing overall application and infrastructure protection.
OWASP DSOMM Project - Introduction to DevSecOps Maturity Model
Explore the OWASP DSOMM Project, a framework for enhancing software security practices and measuring DevSecOps maturity in organizations.
Tour d'Horizon - National Security Threats and Policy Responses
Expert panel discusses current national security threats and potential policy responses, offering insights from former high-level government officials in homeland security, intelligence, and counterterrorism.

vAPI: Vulnerable Adversely Programmed Interface - OWASP API Top 10
Explore and exploit API vulnerabilities using vAPI, a lab environment mimicking OWASP API Top 10 scenarios. Ideal for developers and penetration testers to understand and address common API security issues.
Post-DevOps: What Should We Shift-Left in Application Security?
Exploring post-DevOps challenges in AppSec, focusing on risk profiles, threat response architecture, and operational aspects to enhance security and quality in fast-paced development environments.
Making the Nation Safer Through Cybersecurity - Gen. Keith Alexander's Insights
Retired Gen. Keith Alexander discusses national cybersecurity strategies, government-industry collaboration, and the evolving landscape of cyber threats in a conversation with Walter Isaacson.
Five Philosophies for Building Better Application Logs
Discover five philosophies for creating application logs that enhance breach readiness and forensic capabilities, empowering developers to build more secure and analyzable systems.
Deep Dive: Privacy and Security - What's the Right Balance?
Exploring the tension between privacy and security in technology, featuring experts discussing encryption, data protection, and balancing civil liberties with law enforcement needs.
Managing Risk in the Age of Cyberterrorism
Explore evolving cyberterrorism threats and strategies for managing risks to critical infrastructure, personal data, and intellectual property in our interconnected world.