A DevSecOps Tale of Business, Engineering, and People
Explore DevSecOps through a historical lens, examining its impact on business, engineering, and resilience. Learn from past challenges to build high-performing teams and implement effective DevSecOps strategies.
The Perimeter Has Been Shattered - Mobile and IoT Security Challenges
Explore how mobility and IoT have disrupted traditional enterprise security, examining new threats and the limitations of current defenses. Learn practical strategies to improve mobile and IoT security in the modern landscape.

Jumpstarting Your DevSecOps Pipeline with IAST and RASP
Learn to create an effective DevSecOps pipeline using free tools like IAST and RASP. Gain real-time security feedback, continuous vulnerability analysis, and enhanced attack visibility for improved application security.
Securing the Homeland in the Post-Post 9/11 Era
Explore evolving terrorist threats and homeland security strategies with Secretary John Kelly, discussing current challenges and the administration's plans for safeguarding the nation.
Temporal: Your Company as a Knowledge Graph - The Foundation of Cybersecurity's Future
Explore how Security Knowledge Graphs revolutionize cloud security by mapping entity networks, enabling automated reasoning, and improving data governance across multi-cloud infrastructures.
Preventing an OWASP Top 10 in the World of AI
Explore AI vulnerabilities and security measures in this talk. Learn to protect AI systems, structure AI programs, and implement safeguards like HITL, data classification, and real-time threat monitoring.
Building a Secure Future: Lessons from Past and Present Information Security Challenges
Explore the future of information security, examining past lessons, current challenges, and emerging technologies like quantum cryptography to build a more secure digital world.
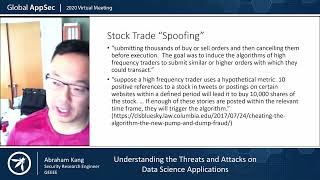
Understanding the Threats and Attacks on Data Science Applications
Explore threats to data science applications, from infrastructure vulnerabilities to attacks on algorithms and developers. Learn to secure your data and protect against emerging risks.
Secure Application Design with High Data Privacy Requirements
Explore secure application design strategies for high data privacy, covering identity management, cryptography, logging, and risk management practices.
Secure React Native Apps Against API Abuse
Aprenda a proteger aplicativos React Native contra abusos de API, explorando vulnerabilidades comuns e implementando estratégias de defesa eficazes para garantir a segurança de seus aplicativos móveis.
Software Supply Chain Lifecycle Management: Reducing Attack Vectors and Enabling Rugged DevOps
Exploring software supply chain lifecycle management to reduce attack vectors and enable rugged DevOps, focusing on IoT security, third-party software risks, and standards-based automation for threat detection.
On the Insecurity of JavaScript Object Signing and Encryption - AppSec EU 2017
Comprehensive analysis of JavaScript Object Signing and Encryption (JOSE) security, revealing critical vulnerabilities in popular libraries and introducing JOSEPH, an automated evaluation tool.
The Privacy Paradox - Balancing Convenience and Personal Data Control
Explore practical strategies to regain control of your personal data online while balancing convenience and privacy in the digital age.
Leaky Processors - Stealing Your Secrets With Foreshadow
Explore the Foreshadow vulnerability in modern processors and its implications for data security. Learn about potential exploits and mitigation strategies.
Machine Learning vs. Cryptocoin Miners
Explore machine learning techniques to detect and combat cryptocurrency mining malware, enhancing cybersecurity defenses against evolving digital threats.

Identity Theft: Attacks on SSO Systems
Explore vulnerabilities in SAML-based SSO systems, including XML signature attacks and user directory flaws. Learn how these issues can lead to identity theft and authentication bypasses in modern organizations.
Creating an AppSec Pipeline with Containers in a Week
Explore the journey of setting up an AppSec pipeline using Docker containers, addressing challenges, managing false positives, and optimizing security tools for seamless integration with development teams.
Monitoring Application Attack Surface and Integrating Security into DevOps Pipelines
Explore methods for calculating and tracking web application attack surface evolution, and learn to integrate security testing into CI/CD pipelines using metrics-based policies.
Securing C Code That Seems to Work Fine
Explore strategies for securing C codebases in high-performance environments, balancing best practices with startup culture. Learn from real-world successes and failures in implementing application security controls.
Juggling the Elephants - Making AppSec a Continuous Program
Strategies for implementing a continuous AppSec program that integrates security initiatives, enables DevOps, and addresses portfolio-wide coverage while prioritizing risks and fostering continuous improvement.
Browser Fingerprints for a More Secure Web - AppSecCali 2019
Explore how browser fingerprints can enhance web security by detecting session roaming and preventing account takeovers, using machine learning to identify anomalies in device configurations.