Defending KA-SAT: Analysis and Response to the 2022 Cyberattack
Delve into the forensic analysis and defense strategies of the 2022 KA-SAT network cyberattack, exploring malware deployment tactics, network-based attacks, and rapid incident response techniques used to protect satellite communications.
Backdoor in the Core - Altering Intel x86 Instruction Set at Runtime
Dive into groundbreaking research on Intel CPU microcode manipulation, exploring techniques for persistent modifications and potential security implications through microcode backdoors in x86 instruction sets.
Breaking into Secure Facilities with OSDP - Vulnerabilities and Exploitation Techniques
Uncover critical vulnerabilities in OSDP security protocols and learn practical exploitation techniques for bypassing encrypted RFID systems through demonstrated pentesting tools and methodologies.
Nine Years of Overlooked MikroTik Pre-Authentication Remote Code Execution Vulnerabilities
Delve into RouterOS's overlooked attack surfaces and discover critical pre-auth RCE vulnerabilities that affected MikroTik devices for 9 years, with insights on detection methodology and security patterns.
Exploiting Cloud Connectivity to Compromise Network-Attached Storage Devices
Uncover critical security vulnerabilities in NAS devices through cloud connectivity exploitation, focusing on WD and Synology systems' authentication weaknesses and remote access vulnerabilities.
When Windows Defender Updates Become a Security Risk
Dive into Windows Defender's architecture and signature update vulnerabilities, exploring how unprivileged users can exploit security flaws to compromise Windows systems and manipulate EDR functionality.
A SSLippery Slope - Unraveling Hidden Dangers of Certificate Misuse
Uncover critical vulnerabilities in digital signature validation systems and learn how attackers can exploit certificate misuse to bypass security measures for signing untrusted code.
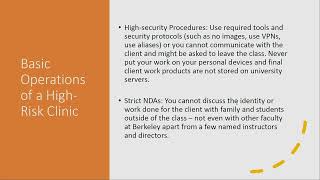
Civil Cyber Defense - Protecting Vulnerable Organizations Against Advanced Threats
Discover how civil cyber defenders protect vulnerable organizations, journalists, and activists using OSINT skills and open-source tools while combating human trafficking and surveillance threats.
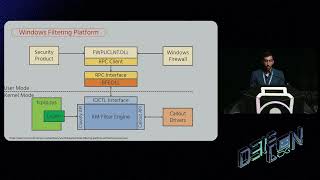
Abusing Windows Filtering Platform for Privilege Escalation - Undetected Attack Techniques
Discover an innovative Windows privilege escalation technique that exploits the Windows Filtering Platform, enabling stealthy system-level access through network traffic manipulation and kernel component abuse.

Advanced ROP Framework - Pushing Return-Oriented Programming to Its Limits
Discover advanced return-oriented programming techniques with ROP ROCKET framework, featuring syscall bypassing, cross-architecture exploitation, and innovative bad byte handling for enhanced security testing.
Defeating VPN Always-On: Security Control Analysis and Bypass Methods
Discover security vulnerabilities in VPN Always-On implementations, exploring bypass techniques and hardening strategies for better network protection and data leak prevention.
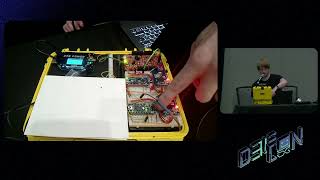
Abusing CAN Bus Specifications for DoS Attacks in Embedded Systems
Explore CAN bus protocol vulnerabilities in automotive systems, focusing on how attackers can exploit metadata fields and protocol specifications to create denial-of-service attacks in embedded systems.
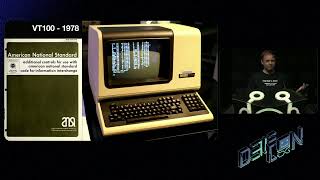
Terminally Owned - 60 Years of Terminal Escape Code Vulnerabilities
Explore terminal security vulnerabilities across platforms, from ASCII's escape character origins to modern exploit techniques, revealing critical remote code execution risks and defense strategies.
Contextualizing The Vulkan Leaks and State-Sponsored Offensive Operations
Explore the implications of the Vulkan files leak, examining Russian cyber capabilities and their connection to global state-sponsored network warfare programs and automated exploitation systems.
What Is a GRC Hacker - Understanding Governance, Risk, and Compliance Security
Discover the role and mindset of GRC (Governance, Risk, and Compliance) hackers in cybersecurity through expert insights and practical perspectives from DEF CON 31.
Bootsquad: Introduction to Secure Boot Exploitation and Defense
Dive into the world of cybersecurity and virtual reality as Joe Mast presents Bootsquad, exploring innovative security concepts and challenges in the DCGVR Village at DEF CON 31.
Grand Theft Actions - Abusing Self-Hosted GitHub Runners for Supply Chain Attacks
Dive into critical security vulnerabilities in GitHub Actions, exploring real-world attacks on self-hosted runners and learning how to prevent supply chain compromises in major open-source projects.
Finding and Exploiting Local Security Vulnerabilities in 1Password for MacOS
Explore critical security vulnerabilities in 1Password's MacOS app, including local vault exploitation, IPC weaknesses, and Chrome extension flaws that could compromise password security.
The Way to Android Root: Exploiting Smartphone GPU
Dive into advanced Android security research exploring Qualcomm Adreno GPU vulnerabilities, exploitation techniques, and kernel-level attacks to achieve root access, with practical mitigation strategies.
Bug Hunting in VMware Device Virtualization - Security Vulnerabilities and Attack Surfaces
Delve into VMware device virtualization security, exploring USB system vulnerabilities, SCSI device emulation, and VMKernel design flaws through real-world bug hunting experiences and discoveries.
BOLABuster - Harnessing LLMs for Automating BOLA Detection
Discover how to leverage LLMs for automated BOLA vulnerability detection in APIs and web applications, exploring BOLABuster's innovative approach to identifying critical security risks at scale.