The New Scourge of Ransomware - A Study of CryptoLocker and Its Friends
Explore the evolution of ransomware, focusing on CryptoLocker and its impact. Learn about threat intelligence responses, infrastructure tracking, and lessons for managing emerging cyber threats.
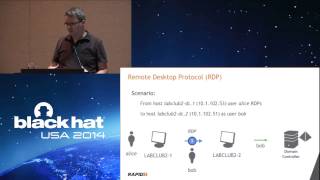
Why You Need to Detect More Than Pass-the-Hash
Explore advanced techniques for detecting compromised credentials beyond Pass-the-Hash, focusing on efficient methods to identify misused or stolen login information.
Investigating PowerShell Attacks
Explore techniques used by attackers to exploit PowerShell for command-and-control, lateral movement, and persistence. Learn to collect and interpret forensic evidence from real-world incidents.
APT Attribution and DNS Profiling
Explore APT attack patterns through DNS profiling, utilizing automated data collection and visualization tools to identify attacker behaviors and potential identities.
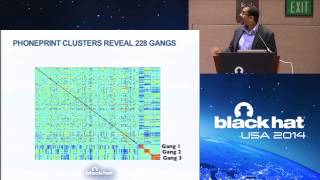
Lifecycle of a Phone Fraudster - Exposing Fraud Activity
Exposing phone fraudsters' tactics in account takeovers through acoustic analysis and graph theory, revealing reconnaissance patterns and providing insights to enhance call center security.
When the Lights Go Out - Hacking Cisco EnergyWise
Explore Cisco EnergyWise vulnerabilities and potential for large-scale blackouts. Learn reverse-engineered protocol details, attack methods, and defense strategies in IP-based energy management systems.
Hacking the Wireless World with Software Defined Radio - 2.0
Explore wireless hacking using software-defined radio. Learn to analyze, reverse engineer, and exploit RF signals in various systems, from pagers to satellites, using open-source tools and affordable hardware.

Point of Sale System Architecture and Security
Explore POS system architecture, integrated payment processing, and security vulnerabilities. Learn attack vectors and mitigation strategies to protect businesses from financial breaches.
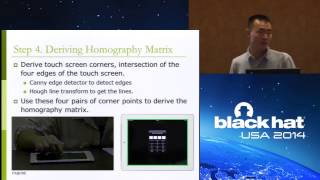
My Google Glass Sees Your Passwords
Innovative computer vision attack automatically recognizes touch screen inputs from a distance, posing significant security risks. Countermeasures include a context-aware privacy-enhancing keyboard for sensitive information.
A Survey of Remote Automotive Attack Surfaces
Comprehensive analysis of remote automotive attack surfaces across various manufacturers, exploring vulnerabilities and potential security improvements in modern vehicles.
The BEAST Wins Again - Why TLS Keeps Failing to Protect HTTP
Explores three new attacks against TLS on the web, revealing vulnerabilities in cryptographic protocols, implementation issues, and HTTPS deployment. Discusses attacker capabilities and mitigation strategies.
48 Dirty Little Secrets Cryptographers Don't Want You to Know
Explore 48 cryptographic attacks through hands-on challenges, covering block ciphers, public key algorithms, and real-world vulnerabilities. Gain practical insights into crypto exploitation across multiple programming languages.
Racing Towards Practical Timing Attacks
Explore practical timing attacks in web applications, focusing on detection, exploitability, and defense. Learn to distinguish theoretical vulnerabilities from real threats using the 'time trial' tool.
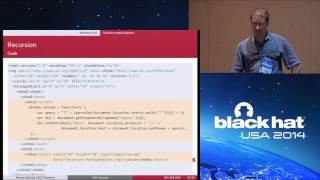
SVG - Exploiting Browsers without Image Parsing Bugs
Explore SVG's hidden potential for web exploitation, including JavaScript execution and external resource imports, challenging traditional browser security assumptions.
The Defense Rests - Automation and APIs for Improving Security
Explore automation and APIs for enhancing security through centralized management, testing, and evidence-driven approaches. Learn to leverage open-source tools and protocols for efficient vulnerability detection and faster recovery.
Control-Alt-Hack - White Hat Hacking for Fun & Profit
Explore ethical hacking through a card game that simulates security audits and consulting. Learn about diverse hacking skills, mission challenges, and cybersecurity concepts in an engaging, entertaining format.
iOS Application Security Assessment and Automation - Introducing SIRA
Automated iOS app security assessment tool SIRA demonstrated, revealing common flaws in AppStore products. Explores risks, testing methods, and future improvements for mobile app security.
Torturing OpenSSL
Explore hardware vulnerabilities in secure systems through a side-channel attack on RSA signatures, demonstrating how induced faults can compromise software-secure systems and extract private keys.
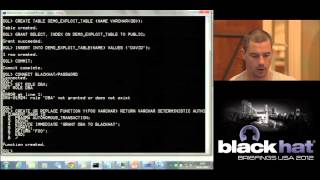
Find Me in Your Database - An Examination of Index Security
Explore Oracle indexing architecture, new flaws, and forensic aspects. Learn to identify issues in custom applications and understand the security implications of database indexing.
Errata Hits Puberty - 13 Years of Chagrin
Exploring the attrition.org Errata project's 13-year journey as an IT and security industry watchdog, including insights into its history, process, impact, and future direction.
Flowers for Automated Malware Analysis
Explore advanced malware obfuscation techniques that bind execution to specific host environments, making automated analysis ineffective. Learn about the arms race between malware authors and security practitioners.