Modern Evasion Techniques
Explore modern evasion techniques for cybersecurity, including Metasploit tips, email controls, Apache ModRewrite, and PowerShell, with practical demonstrations and expert insights.
Aiding Static Analysis - Discovering Vulnerabilities in Binary Targets through Knowledge Graph
Explore advanced techniques for vulnerability detection in binary targets using knowledge graphs, static analysis, and specialized tools like Binary Ninja and Kraken.
Tracing Adversaries - Detecting Attacks with ETW
Explore advanced threat detection using ETW, covering process tracking, PowerShell monitoring, and file I/O analysis for enhanced cybersecurity defenses.
An Introduction to Writing Win32 Shellcode
Learn to write Win32 shellcode, covering memory, registers, testing, generation, and stagers. Gain practical skills for creating and executing custom shellcode.
Windows Rootkit Development - Python Prototyping to Kernel Level C2
Explore kernel-mode drivers for network traffic control, TCP connection handling, and proxy manipulation. Learn weaponization and deployment strategies for advanced Windows rootkit development.
Rapid Incident Response with PowerShell
Learn essential PowerShell techniques for rapid incident response, focusing on preparation, identification, and containment strategies to effectively handle cyber attacks like NotPetya.
Red Team Level Over 9000 - Fusing the Power of NET With a Scripting Language of Your Choosing
Explore advanced red teaming techniques by combining .NET with scripting languages, covering concepts like IronPython, WebAssembly, and PowerShell for enhanced offensive capabilities.
Confessions of an IT OT Marriage Counselor
Explore challenges, threats, and misconceptions in industrial control systems with insights on bridging IT and OT for enhanced cybersecurity in critical infrastructure.
Red Team Methodology - A Naked Look
Explore red team methodology, covering pre-engagement, external and internal tactics, infrastructure automation, and effective communication for comprehensive security assessments.
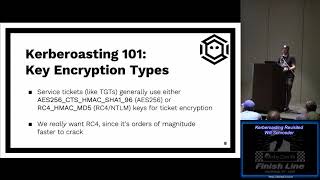
Kerberoasting Revisited
Explore advanced Kerberoasting techniques, encryption types, and defenses. Learn about the "tgtdeleg" trick and Rubeus for improved Kerberoasting in this cybersecurity deep dive.
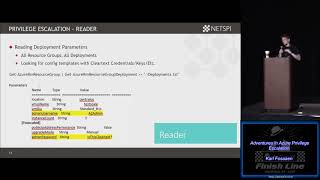
Adventures in Azure Privilege Escalation
Explore Azure privilege escalation techniques, from initial entry to tenant admin access, with practical examples and demonstrations for enhancing cloud security knowledge.
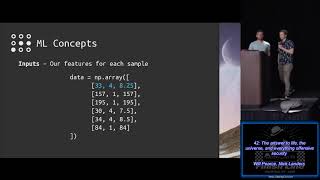
The Answer to Life the Universe and Everything Offensive Security
Explore offensive security through machine learning, sandbox detection, and attack graph theory. Learn about simulation, Q-learning, and adversarial attacks in this comprehensive overview.
Phishing Past Mail Protection Controls Using Azure Information Protection
Explore Azure Information Protection's role in phishing attacks, including features, detection methods, and demos on classification, encryption, and tracking.
Pixel Tracking - How It's Used and Abused
Explore pixel tracking's uses and misuses, including email tracking, online spying, and data leaks. Learn about protection methods and privacy implications.
Early Detection through Deception
Explore early threat detection through deception techniques, including examples of network intrusion, system compromise, and phishing prevention strategies.
Bash Can Get Uglier - Using Bashfuscator to Generate Bash Obfuscation
Explore advanced Bash obfuscation techniques using Bashfuscator, from basic methods to complex strategies like subshells and parameter expansions, enhancing your scripting skills.
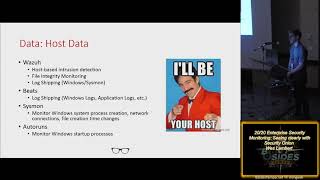
Enterprise Security Monitoring - Seeing Clearly with Security Onion - Wes Lambert
Learn to implement enterprise-level security monitoring using Security Onion, covering tools, data types, interfaces, and deployment strategies for effective threat detection and analysis.
Attacking Azure Environments with PowerShell
Learn to exploit Azure environments using PowerShell, covering data dumping, modules, and various services. Gain insights into escalation techniques and practical demonstrations.
Perfect Storm - Taking the Helm of Kubernetes
Explore Kubernetes security, from container basics to advanced attack techniques and cloud security considerations, with practical insights and defensive strategies.
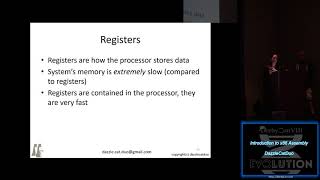
Introduction to x86 Assembly
Learn x86 assembly basics, including registers, memory access, instructions, and system calls. Gain practical skills through examples and a Makefile for assembly programming.
Detecting WMI Exploitation
Learn techniques to detect and prevent WMI exploitation, covering tools, processes, and best practices for enhanced Windows security and threat hunting.