Interact Differently - Get More from Your Tools Through Exposed APIs
Explore how to leverage exposed APIs and plugin interfaces in software tools to enhance functionality, streamline workflows, and create custom solutions for improved efficiency and effectiveness.
Skating on Thin Ice - A Crash Course in Kubernetes and Security
Explore Kubernetes fundamentals, security challenges, and best practices for container orchestration in this crash course, covering clusters, data management, and potential pitfalls.
Monitoring Attack Surface and Integrating Security into DevOps Pipelines
Explore strategies for integrating security into DevOps pipelines, focusing on attack surface monitoring, automated testing, and merging static and dynamic results.
Doing Security in 100 Milliseconds - The Speed of Serverless Computing
Explore serverless computing's impact on security, covering key areas like software supply chain and attack detection. Learn practical approaches and see a demo of building and securing a serverless application.
Hiding From Big Brother Using Distributed Steganography
Learn techniques for hiding data from surveillance using distributed steganography, exploring methods like hidden files, alternate data streams, and encryption combined with steganographic approaches.
Messaging Security Using GlassFish & Open Message Queue
Explore messaging security in GlassFish and Open Message Queue, covering authentication, authorization, encryption, persistence, logging, and monitoring for robust enterprise messaging systems.
Pwning Intranet with HTML 5
Explore HTML5's potential for intranet exploitation using BeEF framework. Learn footprinting, network discovery, port scanning, and inter-protocol exploitation techniques.
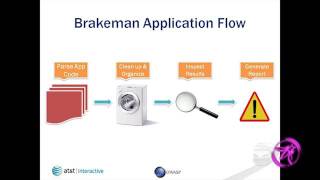
Brakeman & Jenkins - The Duo Detects Defects in Ruby on Rails Code
Explore static analysis tools for Ruby on Rails, focusing on Brakeman and Jenkins integration. Learn about security warnings, code updates, and best practices for detecting defects.
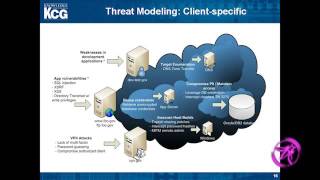
Simplifying Threat Modeling
Simplified approach to threat modeling: identify attack surfaces, visualize users as threats, illuminate assets and trust boundaries, postulate attacks, evaluate impact, and mitigate risks.
Improve Your SDLC with CAPEC and CWE
Enhance software development lifecycle using CAPEC and CWE. Learn threat modeling, design considerations, and security testing techniques to improve application security.
Application Logging in the Era of GDPR
Explore application logging best practices in the GDPR era, covering security, privacy, data protection, and compliance recommendations for developers and operations teams.
A DevOps View of AppSec
Explore DevOps history and its impact on AppSec, charting a path for DevSecOps success through standardization, automation, and Agile principles.
Achieve AI-powered API Privacy Using Open Source
Explore AI-powered API privacy using open-source tools. Learn about Privacy-by-Design, threat modeling, and leveraging deep neural networks to protect customer data in software development.
Securing Modern API and Microservice Based Applications by Design
Learn to secure modern API and microservices architectures with expert insights on key concerns, architectural patterns, and actionable solutions for robust application security.
Micro-services Challenges - Istio to the Rescue
Explore Istio's solutions for micro-services challenges, including traffic management, policy enforcement, and security, to enhance scalability and operational efficiency.
New Age Cloud Security - How to Build Secure Multi-Cloud Applications and Still Sleep Well
Learn to build secure multi-cloud applications with modern techniques. Explore industry trends, development phases, and essential components like TLS, DNS, user management, and data encryption for robust cloud security.
On the Internet, Nobody Knows You're a Dog - Revisiting the Meme After 25 Years
Explore the evolution of online identity verification, from historical trends to current challenges and future opportunities, including AI and ML applications in authentication and access management.
How to Build an Effective Malware Protection Architecture for File Uploads in Modern Web Apps
Explore a novel approach to automated malware analysis for file uploads in web apps, focusing on scalability, performance, and effective detection of malicious content.
Secure Configuration in the Cloud
Explore secure configuration management in cloud environments, focusing on protecting sensitive assets, managing configuration secrets, and implementing best practices for DevOps security.
Running at Light Speed - Cloud Native Security Patterns
Explore cloud native security patterns for containerized microservices, covering multi-tenancy, authentication, authorization, and encryption. Learn architectural guidance for secure software design in cloud environments.
Adapting Your AppSec
Explore strategies for integrating application security into modern development processes without hindering progress. Learn about tooling, assessments, and agile methodologies for effective security implementation.