Discover How EclecticIQ Platform and MISP Go Together
Explore the synergy between EclecticIQ Platform and MISP for enhanced threat intelligence sharing, automated analysis, and streamlined incident response workflows.
Scaling Sighting
Explore efficient data storage and retrieval techniques for large-scale threat intelligence using Sighting, focusing on performance optimization and integration strategies.
Abusing Bash for Windows
Explore techniques for exploiting Bash on Windows, including remote shells, password extraction, and AppLocker bypasses. Learn about security implications and forensic considerations.
Modmob Tools - Home Made Tools to Test Mobile Devices and Monitor Networks
Explore homemade tools for testing mobile devices and monitoring networks, covering interception techniques, firmware analysis, and hardware auditing for enhanced security understanding.
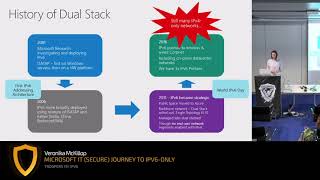
Microsoft IT - Secure Journey to IPv6-Only
Explore Microsoft's transition to IPv6-only networks, covering industry pressures, implementation challenges, and key lessons learned in this technical deep dive.
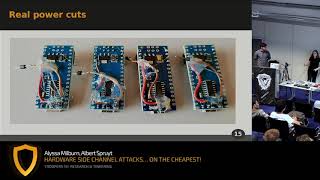
Hardware Side Channel Attacks on the Cheapest
Explore side channel attacks on low-cost hardware, covering power analysis, encryption vulnerabilities, and practical demonstrations. Learn acquisition techniques and countermeasures.
Is 2019 Finally the Year of Linux on the Desktop? And What About v6-Only in WiFi Networks?
Explore IPv6-only networks, their benefits, and challenges through real-world case studies and application testing, including popular gaming and communication platforms.
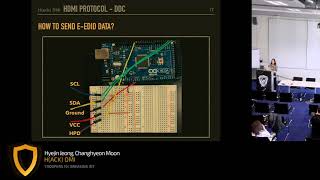
HackDMI
Explore HackDMI: Learn about HDMI protocols, CEC messaging, and ARC. Discover vulnerabilities in HDMI implementations and gain insights into fuzzing techniques for digital media interfaces.
API Security - Is it the New Application Attack Surface and How to Secure at Enterprise Scale
Explore API security challenges, threats, and enterprise-scale solutions. Learn about modern attack surfaces, recent breaches, and effective strategies for protecting sensitive data in API-driven architectures.
The Final Frontier - Automating Dynamic Security Testing
Automating dynamic security testing: strategies for efficient, scalable DAST integration in software delivery pipelines, addressing challenges and trade-offs for seamless DevSecOps implementation.
A Stratagem on Strategy - Rolling Testing into Product Testing
Explore integrating security testing into product testing strategies, enhancing coverage and aligning security with software requirements for more effective quality assurance in the SDLC.
Being a Cyberdefender - Behind the Curtains
Explore the realities of cyberdefense, including incident management, communication challenges, and maintaining work-life balance in this insightful talk by a seasoned professional.
Bypassing Microsoft Defender for Identity
Explore techniques to bypass Microsoft Defender for Identity, executing high-impact attacks across the kill chain while avoiding detection in on-premises Active Directory environments.
Android Malware Targeting Belgian Financial Apps
Explore Android malware's evolution, focusing on banking trojans targeting Belgian apps. Learn about various malware types, their mechanisms, and strategies for protection.
Process Control through Counterfeit Comms
Explore vulnerabilities in PLCs, focusing on discovery methods and how combining minor flaws can lead to device takeover. Learn about SNMP exploitation, memory manipulation, and firmware modification.
Forging Trusts for Deception in Active Directory
Explore forging trusts in Active Directory for deception-based defense. Learn techniques to implant decoy objects, trap adversaries, and enhance network security through live demonstrations.
Hacking Driverless Vehicles
Exploring vulnerabilities in autonomous vehicles: sensors, decision profiles, and potential exploits. Insights into connected vehicle programs and their security implications for future transportation systems.
DYODE - Do Your Own Dyode
Explore DYODE, a low-cost DIY data diode for securing Industrial Control Systems. Learn about its development, components, and applications in file transfer, Modbus data, and remote debugging.
Evading Microsoft ATA for Active Directory Domination
Explore techniques for evading Microsoft ATA in Active Directory environments, including threat detection bypasses, attack chain modifications, and strategies for maintaining domain dominance.
Ant-Forensics AF - Dual Core
Explore anti-forensics techniques for Windows, Linux, and Android, covering memory analysis, encryption, and hardware implants. Learn to protect digital evidence and understand forensic challenges.
Creating REAL Threat Intelligence with Evernote
Explore threat intelligence creation using Evernote, covering data-driven feeds, task management, and open-source intelligence gathering for effective organizational security strategies.