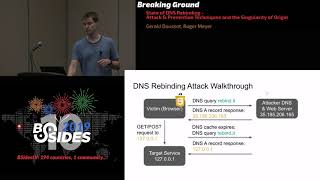
State of DNS Rebinding - Attack & Prevention Techniques and the Singularity of Origin
Explore DNS rebinding attacks, prevention techniques, and the concept of origin singularity. Learn about query analysis, protection bypasses, and practical defense strategies against this web security threat.
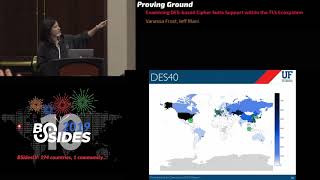
Examining DES-based Cipher Suite Support within the TLS Ecosystem
Explore DES-based cipher suite support in TLS, analyzing prevalence, geographical distribution, and implications for security. Learn why DES persists and how to remove it.
From Email Address to Phone Number - A New OSINT Approach
Explore innovative OSINT techniques to uncover phone numbers from email addresses, enhancing privacy and security investigations with cutting-edge methodologies and tools.
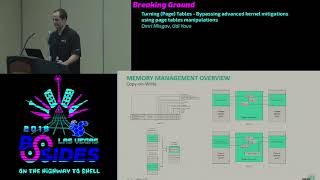
Turning - Page Tables - Bypassing Advanced Kernel Mitigations Using Page Tables Manipulations
Explore advanced kernel exploit techniques using page table manipulations to bypass Windows 10 mitigations. Learn virtualization-based security and memory management concepts.
The Current State of Adversarial Machine Learning
Explore adversarial machine learning's current landscape, including attack types, vulnerabilities, and defense strategies. Gain insights into visual understanding and notable research in this critical field.
Bypassing Antivirus Engines Using Open Sourced Malleable C2 Software, MSFVenom, Powershell and a Bit of Guile
Learn techniques to bypass antivirus using open source tools like Malleable C2, MSFVenom, and PowerShell. Explore examples and scripts for more effective penetration testing and security assessments.
Disabling Encryption to Access Confidential Data
Explore techniques for disabling encryption to access confidential data, including man-in-the-middle attacks, AWS vulnerabilities, and TLS exploits. Learn practical methods and necessary tools for intercepting encrypted communications.
Security and DevOps Are Really Best Friends
Explore the synergy between security and DevOps, focusing on asset management, automation, and best practices for enhanced cybersecurity in modern IT environments.
Abusing Password Reuse at Scale - Bcrypt and Beyond
Explore advanced techniques for exploiting password reuse vulnerabilities, focusing on bcrypt and other hashing methods to enhance cybersecurity knowledge and ethical hacking skills.
Red Teaming a Manufacturing Network - Without Crashing It
Explore techniques for safely red teaming manufacturing networks, including reconnaissance, passive methods, and potential attack vectors, while learning mitigation strategies and best practices.
Active Directory Password Blacklisting
Explore Active Directory password blacklisting techniques, implementation challenges, and testing frameworks for enhanced security in Windows environments.
ATT&CKing the Status Quo - Improving Threat Intel and Cyber Defense with MITRE ATT&CK
Explore MITRE ATT&CK framework to enhance threat intelligence and cyber defense strategies. Learn implementation tips, detection techniques, and industry examples for improved security posture.
CheckPlease - Payload-Agnostic Sandbox Detection
Explore payload-agnostic sandbox detection techniques, including sleep evasion, encryption, and user activity analysis. Learn to build profiles and implement various detection methods across languages.
Pwning Software-Defined Networking - SDN
Explore software-defined networking vulnerabilities, focusing on OpenFlow, controllers, and REST APIs. Learn to manipulate traffic flow and exploit SDN weaknesses.
Zero Trust Networks - In Theory and in Practice
Comprehensive exploration of Zero Trust Networks, covering theory, implementation strategies, key systems, and practical considerations for enhanced network security.
Introduction to Reversing and Pwning
Explore reverse engineering and exploitation techniques, covering low-level programming, memory vulnerabilities, and essential tools for cybersecurity enthusiasts and professionals.
WAFs FTW! A Modern DevOps Approach to Security Testing Your WAF
Explore modern DevOps approach to security testing Web Application Firewalls (WAFs) using Framework for Testing WAFs (FTW). Learn objective WAF evaluation, rapid prototyping, and continuous testing strategies.
An Agile Framework for Building GDPR Privacy and Data Protection Requirements into SDLC
Agile framework for integrating GDPR privacy and data protection requirements into software development lifecycle, using a tag-based approach to identify and implement necessary features efficiently.
Where We're Going, We Won't Need Passwords
Explore enterprise-wide multifactor authentication deployment, addressing technical challenges, user experience, and lessons learned for seamless workforce authentication across devices and legacy systems.
Building Secure ASP.NET Core MVC Applications
Explore ASP.NET Core MVC security features, including XSS and CSRF protection. Learn to build robust web applications with modular architecture and cross-platform compatibility.

Cryptography in the Age of Heartbleed
Cryptography expert discusses challenges in encryption, recent vulnerabilities in web protocols, and securing cryptographic software against sophisticated attackers, emphasizing the need for simplification.