Not Only Frogs Can Hop
Explore novel VLAN hopping methods using SNMP, including live demos and the release of Frogger 2 tool for automated and improved network security testing.
Software Defined Networking - SDN Security
Explore SDN security implications, attack surfaces, and vulnerabilities with live exploit demos. Learn about efforts to enhance SDN controller security and future developments.
2012 In Review - Tor and the Censorship Arms Race
Explore the ongoing battle between Tor and censorship efforts, examining key developments and challenges in online privacy and freedom of information.
When Documents Bite
Explore malicious document attacks, their evolution, and impact on cybersecurity. Learn about real-world techniques and strategies for defending against targeted attacks in enterprise networks.
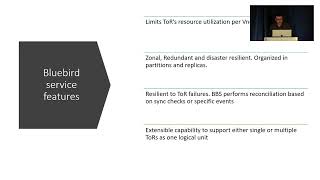
Bluebird - High-performance SDN for Bare-metal Cloud Services
Explore Bluebird, Azure's high-performance network virtualization system for bare-metal cloud services, offering insights into its design, implementation, and real-world performance.
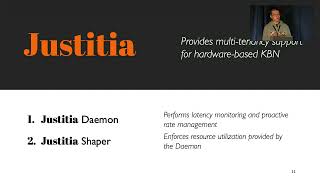
Justitia - Software Multi-Tenancy in Hardware Kernel-Bypass Networks
Explore software multi-tenancy in hardware kernel-bypass networks, addressing challenges in network sharing policies while preserving low latency and CPU efficiency in modern datacenters.
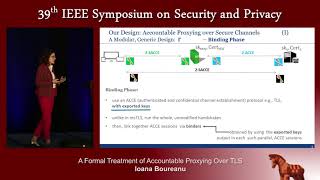
A Formal Treatment of Accountable Proxying over TLS
Formal analysis of accountable proxying over TLS, revealing vulnerabilities in mcTLS and proposing a secure alternative with provable security and practical implementation.
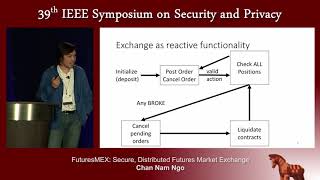
FuturesMEX - Secure, Distributed Futures Market Exchange
Explore a secure, distributed futures market exchange protocol with key operations, security properties, and economic viability considerations for low-frequency trading environments.
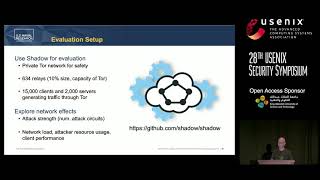
Point Break - A Study of Bandwidth Denial-of-Service Attacks against Tor
Explores bandwidth denial-of-service attacks against Tor, demonstrating feasibility and impact on network performance through experimentation and simulation. Analyzes costs and effects of various attack strategies.
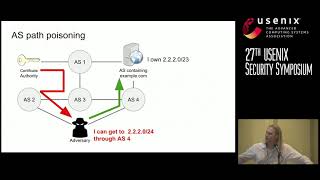
Bamboozling Certificate Authorities with BGP
Análisis de vulnerabilidades en la infraestructura de clave pública y demostración de ataques BGP para obtener certificados falsos, con propuestas de contramedidas para mejorar la seguridad.
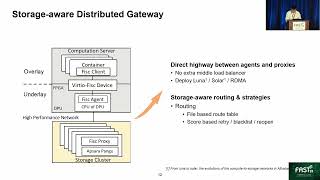
Fisc - A Large-scale Cloud-native-oriented File System
Innovative cloud-native file system addressing challenges in container-based applications. Introduces lightweight client, DPU-based offloading, storage-aware mechanism, and full path QoS for improved performance and resource efficiency.
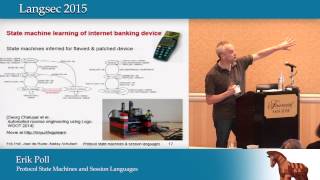
Protocol State Machines and Session Languages
Explores protocol state machines and session languages in security, discussing specification, implementation, and testing challenges. Proposes automated inference of formal specifications to improve security.
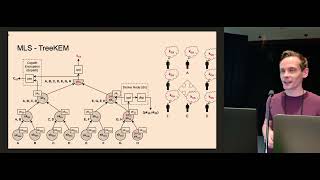
Security Analysis of the MLS Key Derivation
Explore the security aspects of MLS key derivation, focusing on analysis techniques and potential vulnerabilities in this cryptographic process.
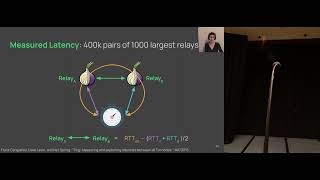
ShorTor - Improving Tor Network Latency via Multi-hop Overlay Routing
Explore innovative techniques to enhance Tor network performance through multi-hop overlay routing, reducing latency and improving user experience while maintaining anonymity.
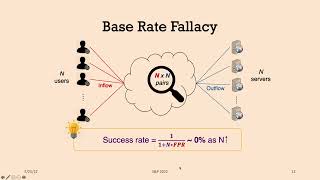
DeepCoFFEA - Improved Flow Correlation Attacks on Tor via Metric Learning and Amplification
Explore advanced flow correlation attacks on Tor using metric learning and amplification techniques, enhancing network security understanding and defense strategies.
BlueMirror - Reflections on Bluetooth Pairing and Provisioning Protocols
Explore Bluetooth pairing and provisioning protocols, focusing on security vulnerabilities and potential exploits in wireless communication systems.
If HTTPS Were Secure I Wouldn't Need 2FA - End User and Administrator Mental Models of HTTPS
Explores misconceptions about HTTPS security among end users and administrators, revealing gaps in understanding and providing recommendations for improved protocol design and user interfaces.
A Security Model and Fully Verified Implementation for the IETF QUIC Record Layer
Explore a verified implementation of IETF QUIC's record layer, examining its security model and implications for network protocol design and verification.
Reproducible Building Network Infrastructure
Explore the design and implementation of a non-commercial ISP network, including Ethernet and IP setup, and learn about migrating to a NixOS-based system for improved reproducibility and management.
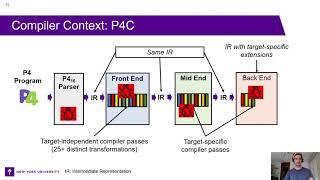
Gauntlet - Finding Bugs in Compilers for Programmable Packet Processing
Explores techniques for detecting bugs in P4 compilers, presenting Gauntlet tool that found 96 new bugs across platforms, leading to fixes and P4 specification changes.
Data Loss Prevention Group Therapy
Explore data loss prevention strategies, pitfalls, and innovative use cases. Learn how to implement effective DLP programs, detect malware, and address common challenges in information security.