Understanding the Cloud Shared Responsibility Model
Experts explain the Cloud Shared Responsibility Model, detailing security duties for providers and users. Learn key elements, debunk misconceptions, and discover best practices for maintaining a secure cloud environment.
Terraform for Platform Engineers: Delivering Value and Managing Infrastructure
Explore how Terraform empowers platform engineers to deliver value, standardize cloud management, and address security, compliance, and financial concerns in infrastructure lifecycle management.
Securely Running Databricks on AWS for Public Sector and Regulated Industries
Explore secure Databricks deployment on AWS for regulated industries, covering compliance, encryption, data governance, and workflow orchestration for stringent security requirements.
Enhancing Enterprise Trusted Data Governance - Integrating Informatica IDMC with Databricks Unity Catalog
Discover how integrating Informatica IDMC with Databricks Unity Catalog enhances data governance, enabling comprehensive metadata management, lineage tracking, and policy enforcement across enterprise data ecosystems.
Gen-Z Critique on SOC 2 Certification - 5 Essential Steps for Startups
Reinterpretation of SOC 2 audits through Gen-Z perspective, highlighting strengths, pitfalls, and 5 essential steps for startup certification. Offers fresh insights on Silicon Valley's security standard.
CISA Certification Training - Understanding the Exam and Its Benefits
Comprehensive overview of CISA certification: benefits, target audience, experience requirements, and exam structure. Ideal for IT professionals seeking career advancement in information systems auditing.
Centralized Policy Management
Explore methods for applying centralized policy at scale, focusing on Open Policy Agent (OPA) and its integration with Kubernetes for improved security and compliance in complex microservices architectures.
Channeling the Potential of Generative AI with API Ecosystems
Explore innovations in Apigee API Management to accelerate development, gain control, and enhance security in generative AI-powered API ecosystems.
Legal Risks and Rights for Developers
Explore legal risks and rights for developers, covering data ownership, copyright, contracts, open source, and data protection, with insights on GDPR and cloud computing implications.

Practical Microservice Security
Explore microservice security challenges and solutions, covering authentication, authorization, API protection, and best practices for building secure distributed systems.
Why Building Your Ship with Raw Materials is a Bad Idea
Explore software bill of materials (SBOMs), open source compliance, and best practices for secure, robust application development in the face of new regulations and vulnerabilities.
Supply Chain Security for OpenSource Projects
Explore supply chain security for open-source projects, covering potential threats, attack points, free tools, and strategies to protect against cyber attacks in software development.
Cloud Security Made for the EU - Securing Data & Applications
Explore confidential computing and real-time compliance for ultimate data security in EU cloud transitions. Learn key strategies to satisfy data protection regulations and address CISO concerns.
Regulation and Risk When Your Customer's Browser Leaks Data
Explore data protection challenges in browsers, regulatory expectations, and strategies to manage risks associated with customer data leaks in web and mobile environments.
Data Privacy Concerns - A Risk Based Approach to De-Identification
Explore a comprehensive approach to data de-identification, covering risk scores, certification processes, and key business outcomes in response to new privacy regulations.
Breaking Up Isn't Hard to Do: Separating Releases from Deploys with Feature Flags
Explore OpenFeature for risk reduction, faster delivery, compliance support, and experimentation in DevOps using vendor-neutral feature flags.
Understanding the Cyber Security Acronym Soup
Demystifying cybersecurity standards: their impact on organizations, IT service providers, and consumers. Learn about compliance, certification, and the implications for development, security, and operations teams.
Easier, Faster, and Safer Open Source Consumption Governance
Discover practical strategies for automating and securing open source consumption while maintaining effective governance and legal compliance in enterprise environments.
Building an Enterprise Scale MLOps Platform - From Development to Deployment
Discover how NatWest built a streamlined MLOps platform to enhance productivity, automate ML workflows, and ensure security compliance in enterprise-scale machine learning operations.
The Telemetry of Trust - Using Attestations to Secure Your Software Development Lifecycle with Open Source Tools
Discover how attestations and cryptographic telemetry can secure software delivery at scale, building trust through verifiable inputs and enabling safer deployment decisions across diverse development environments.
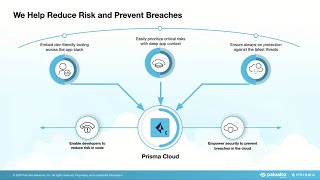
Revolutionizing Cloud Data Security with Palo Alto DSPM and DDR
Master cloud data security essentials with DSPM and DDR, focusing on sensitive data management, real-time monitoring, and compliance in modern cloud environments and AI infrastructure.