The Legal Perspective on Data Security for 2016
Explore legal aspects of data security, including 2015 breaches, enforcement, privacy policies, and international regulations. Learn preparation strategies and compliance measures.
SecOps - Innovating Security in Innovative Organizations
Explore innovative security approaches for modern organizations, focusing on data governance, compliance, and fostering a security-conscious culture.
So You Want to Be a CISO
Explore the role of a CISO, including challenges, responsibilities, and key perspectives in cybersecurity leadership and risk management.
Why Compliance Matters - You've Been Doing It Wrong
Discover why traditional compliance approaches fall short and learn innovative strategies for effective risk management and regulatory adherence.
I Got You - Agilely Compliant yet Insecure
Explore agile compliance and security challenges in software development, uncovering potential vulnerabilities and strategies for balancing speed with robust protection.
Cloud Security Introduction to FedRAMP
Explore cloud security, FedRAMP certification, and key considerations for organizations adopting cloud technologies in this comprehensive introduction.
Emerging Governance Frameworks for Healthcare Security
Explore emerging governance frameworks for healthcare security, addressing challenges, root causes, and strategies for implementing effective risk management and high trust readiness.
Reality Checking Your AppSec Program
Explore strategies to critically assess and improve your AppSec program, focusing on compliance, maturity, education, and validation beyond traditional metrics and assumptions.
So You've Inherited a Security Department - Now What
Learn essential strategies for managing an inherited security department, covering OSINT tools, best practices, and key areas like compliance, user education, and vulnerability scanning.
Information Security and the Law
Explore legal aspects of information security, including compliance, regulations, and legal frameworks affecting cybersecurity practices and policies.
SCAP - A Primer and Customization
Comprehensive overview of SCAP, covering basics, components, tools, and customization techniques for effective security configuration assessment and management.
Hacking the Users - Developing the Human Sensor and Firewall
Develop human sensors and firewalls through effective security awareness training, focusing on phishing, ransomware, and social engineering to enhance organizational cybersecurity.
GRC - What Would You Say You Do Here
Explore governance, risk, and compliance in cybersecurity with insights on effective GRC program implementation and its impact on organizational security posture.
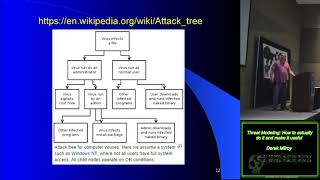
Threat Modeling - How to Actually Do It and Make It Useful
Learn practical threat modeling techniques for effective cybersecurity. Explore various methodologies, tools, and frameworks to identify and mitigate potential risks in software and systems.
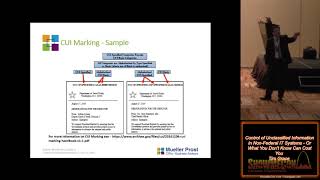
Control of Unclassified Information in Non-Federal IT Systems - Or What You Don't Know
Explore the management of unclassified information in non-federal IT systems, uncovering crucial insights for data protection and compliance in diverse technological environments.
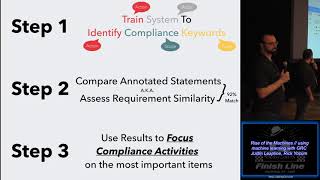
Rise of the Machines - Using Machine Learning with GRC
Explore machine learning applications in Governance, Risk, and Compliance (GRC) to enhance security and streamline processes in this insightful conference talk.
Shifting Container Security Into Overdrive with Prisma Cloud and Computing Edition
Explore container security best practices, focusing on visibility, communication, automation, compliance, and pipeline integration for enhanced protection in containerized environments.
To Space and Beyond - Discussing Fintech
Insights on fintech industry trends, Rapyd's global expansion, and the importance of compliance in finance from Arik Shtilman. Explores SaaS misconceptions and the ubiquity of fintech in major companies.
What's New in gRPC Security for 2023 - Audit Logging and CRL
Explore gRPC Security updates for 2023, focusing on Audit Logging and enhanced CRL behaviors. Learn to implement effective security measures and safeguard systems against emerging threats.
A Long Day's Journey Into Backups
Explore the evolution of enterprise backup solutions, from costly mistakes to efficient systems, with insights on storage optimization, compliance, and future improvements for operations engineers.
Improving the FreeBSD Security Advisory Process
Explore FreeBSD's security advisory process, challenges in handling vulnerabilities, and the role of the security officer team in managing third-party embargoes and timely responses.