Open Policy Agent (OPA) Introduction and Deep Dive
Explore Open Policy Agent (OPA) for cloud-native policy enforcement. Learn about its applications, latest features, and integration with Kubernetes through OPA Gatekeeper.
ZeroTrust Microservices with WebAssembly and WireGuard
Explore zero-trust architectures for cloud computing using WebAssembly and WireGuard. Learn to implement end-to-end encryption and role-based access controls in microservices for enhanced security.
Detecting Cloud and Container Threats - Kubernetes Security
Prepare, detect, and respond to security threats in containers and Kubernetes while maintaining agility. Learn to create perimeters, assess container content, and catch anomalies in fast-paced cloud environments.
Combining Confidential Computing and Cloud Native Security
Explore confidential computing and cloud-native security integration to protect Kubernetes clusters against internal and external threats, using Constellation and Tetragon for enhanced integrity and runtime enforcement.
Running Policy in Hard-to-Reach Places with WASM and OPA
Explore how WebAssembly and Open Policy Agent enable standardized business rule enforcement across diverse environments, from servers to smartphones, with centralized management and instant user feedback.
Design Patterns for OPA and Cloud Native Authorization
Explore cloud-native authorization strategies using Open Policy Agent (OPA), focusing on design patterns for secure and scalable access control in modern distributed systems.
Modern Continuous Delivery Techniques with OPA - Moving Fast When You Can't Break Things
Explore modern Continuous Delivery techniques using OPA in CI/CD pipelines. Discover safe deployment strategies, policy enforcement, and the Continuous Delivery Foundation's role in advancing CD practices.
A CNCF Landscape Overview - From Kubernetes to Open Policy Agent
Explore the CNCF Landscape with Carson Anderson, covering key cloud-native technologies, tools, and projects for modern infrastructure and application development.
Keylime - Bootstrap and Maintain Trust on the Edge, Cloud, and IoT
Explore Keylime's innovative approach to bootstrapping and maintaining trust across edge computing, cloud environments, and IoT devices for enhanced security and integrity.
Securing Your Cloud Native Stack with Policy-as-Code and OPA
Explore policy-as-code and OPA for securing cloud-native stacks. Learn implementation strategies and best practices for robust security in modern infrastructure.
Encrypted Virtual Machine Images for Confidential Computing
Explore encrypted VM images for confidential computing, enhancing data security and privacy in cloud environments.
Fine-grained Authorization in Containerized Environments Using Open Policy Agent
Explore fine-grained authorization using Open Policy Agent (OPA) for containerized environments, focusing on policy enforcement in Kubernetes without modifying core components.
Confidential Containers: The Next Episode in Workload Isolation
Explore advanced container isolation using Kata-CC, leveraging Trusted Execution Environment features for enhanced security in multi-tenant environments through workload attestation and memory encryption.
Tales from the Cloud Native Community
Explore the vibrant cloud native community, its diverse projects, and the collaborative efforts shaping its future. Discover inspiring stories and opportunities to learn, contribute, and collaborate.
Anatomy of a Cloud Security Breach - 7 Deadly Sins
Explore 7 real cloud security breaches, their attack patterns, and defense strategies. Learn key differences between cloud and on-premise threats, and gain actionable insights to protect your cloud infrastructure.
From SBOMs to IBOMs - Know What's Happening in Your Clusters
Explore the importance of Infrastructure Bill of Materials (IBOM) in cloud-native environments, its role in security, and how to leverage it for cost optimization and reducing attack surfaces.
Falco and Atomic Red Team - Real-time Threat Detection in Cloud-Native Systems
Explore real-time threat detection in cloud-native systems using Falco and Atomic Red Team, enhancing security practices for modern infrastructure.
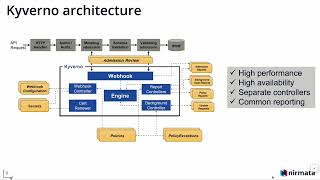
Securely Provisioning Cloud Resources Using Kyverno and Crossplane
Learn to securely provision cloud resources using Kyverno and Crossplane, enhancing your infrastructure management skills and improving cloud security practices.
Securing Norway's Welfare System: Transparent End-to-End Encryption in the Cloud
Explore how Norway's welfare system secures its cloud-based platform, balancing developer convenience, reliability, and security for 1600+ applications on Kubernetes, with focus on transparent end-to-end encryption.
CNL - Supercharge Your Infrastructure Management with OPA
Explore OPA for efficient infrastructure management, enhancing security and compliance across cloud-native environments. Learn implementation strategies and best practices.
What's New with Open Policy Agent Gatekeeper
Explore recent updates and advancements in Open Policy Agent Gatekeeper, enhancing Kubernetes security and policy enforcement capabilities.