Five and a Half Actions to Mitigate Software Supply Chain Threats
Discover five crucial actions to protect your software supply chain from threats, including insights from Commerzbank's use of Google Cloud's Assured OSS.
Removing AWS Policy Review Fatigue with Automated Terraform Resource Analysis
Automate AWS policy control with Terraform resource analysis, reducing security review fatigue and improving developer productivity through early-stage static analysis in IaC pipelines.
DARCC - The 5 Layers of Modern App Security
Explore the DARCC layers of modern app security: Dependency, Access-Control, Runtime, Configuration, and Container. Learn best practices for securing your software supply chain and enforcing policies.
How to Start with DevSecOps on Kubernetes
Explore container security implications and strategies for Kubernetes ecosystems. Learn essential controls and best practices to secure containerized workloads in production environments.
MacGyverOps: Secure Your Development Environment with the Tools Around You
Leverage existing tools to create focused security feedback, minimizing distractions while enhancing development velocity and security in DevOps environments.
The State of DevSecOps in 2023 - Challenges and AI Solutions
Explore DevSecOps failures and AI solutions in 2023. Gain insights from Ashish Rajan's 13+ years of cybersecurity experience, focusing on cloud security and enterprise risk management at scale.
Application-Layer Guarantees for Data Authenticity, Integrity, and Privacy
Explore end-to-end data security in modern distributed applications. Learn to implement authenticity, integrity, and privacy guarantees across complex multi-hop routes and untrusted environments.
Power of AI: DevSecOps and Cloud Artifact Signing Explored - Sessions 1 and 2
Explore AI's impact on DevSecOps and cloud artifact signing. Learn how AI enhances security automation, vulnerability scanning, and threat detection. Discover tools for ensuring trust and integrity in cloud environments.
Exploring Card Games in Threat Modeling - Enhancing Security Posture
Explore innovative card games for threat modeling, including Elevation of Privileges, OWASP Cornucopia, and OWASP Cumulus. Learn how these engaging tools can enhance your organization's security posture through interactive gameplay.
The Impact of Policy-as-Code on the Software Supply Chain
Explore DevSecOps principles for securing the software supply chain. Learn to automate, version, and implement controls as code for resilient software ecosystems.
Exploiting and Fixing Vulnerabilities - A Gamified Approach
Discover how gamification and CTFs make application security tangible for developers in cloud-native environments, addressing risks across code, dependencies, containers, and clusters.
Securing Applications in SDLC and Cloud-Native Web and API Protection - Sessions 1 and 2
Learn secure coding practices, identify vulnerabilities, and integrate security into SDLC. Explore cloud-native WAAP for effective web app and API protection using machine learning.
Mapping Your External Attack Surface: Illuminating Hidden Vulnerabilities
Illuminate hidden assets and vulnerabilities in your external attack surface using powerful reconnaissance tools. Proactively defend your digital perimeter and stay ahead of potential threats.
openCRE.org - A Cloud of Knowledge
Explore openCRE.org, a knowledge cloud for cybersecurity, presented by Spyros Gasteratos at SOOCon23 Security.
DevSecOps Connect - Integrating Security in Development and Operations
Explore DevSecOps principles, secure serverless architectures, enhance WordPress security, and fortify Dart/Flutter projects. Gain insights from industry experts and network with professionals.
What's Next for Security Professionals - Innovations in Threat Prevention and AI-Driven Security
Explore the convergence of security capabilities, AI-driven innovations, and insights from industry leaders to transform your organization's security approach.
Building a Yocto CI Pipeline with KAS, GHActions and AWS
Explore building a Yocto CI pipeline using KAS, GitHub Actions, and AWS for efficient embedded systems development and deployment.
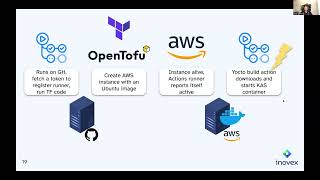
Building a Yocto CI Pipeline with KAS, GitHub Actions, and AWS - YPS 2023.11
Explore CI pipeline creation for Yocto using KAS, GitHub Actions, and AWS. Learn to overcome challenges and implement effective strategies.
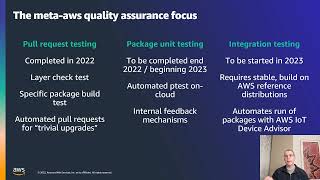
AWS and Yocto Project: Leveraging Open Source for IoT and Embedded Systems
Explore AWS's use of Yocto Project in IoT products, covering software development, integration, and quality assurance for device ecosystems.
Automating Yocto Layer Maintenance with Cloud Managed Services - Thomas Roos
Automate Yocto layer maintenance using cloud services to save time, upgrade software, test recipes, and backport changes efficiently.
Policy-Driven Supply Chain Security with Enterprise Contract
Explore Enterprise Contract for enforcing software supply chain security and compliance. Learn to verify container images, signatures, and attestations using customizable policies.