Secure Your Software Supply Chain Using Observability
Explore techniques for enhancing software supply chain security through observability, focusing on key benefits and practical implementation strategies.
Air Gap: A Short Introduction and Why It Isn't Complicated
Discover the simplicity of Air Gap technology in this concise introduction, demystifying its concepts and applications for easy understanding.
Green Software and Open Hardware: Addressing Ecological Impact in IT
Exploring the ecological impact of software and IT infrastructure, discussing best practices and technologies to reduce the carbon footprint of digital systems and data centers.
CTF Overview and Experience - Preparing for SecurityCon
Prepare for SecurityCon's CTF event with a warm-up session covering container breakouts and Kubernetes misconfigurations. Suitable for all experience levels, learn CTF engagement techniques.
Cloud Native - Protecting Software Supply Chains Using Kyverno
Explore Kyverno's role in safeguarding software supply chains, enhancing security practices, and ensuring compliance in cloud-native environments.
ADHD: Understanding, Awareness, and Inclusivity in Cloud-Native Communities
Exploring ADHD in tech: Neurodivergent speakers share experiences, insights, and tips for recognizing and supporting ADHD in the cloud-native community, promoting inclusivity and awareness.
Securing the Supply Chain with Witness - A Framework for Supply Chain Security
Explore Witness, an open-source framework for supply chain security, its trust model, and implementation in CI pipelines. Learn about attestation collections, policy enforcement, and integration with cloud-native tools.
Towards the Cloud Native Telco: Learning from the Trenches
Insights on cloud-native transformation in telecom, focusing on Kubernetes deployment for 5G Core platforms and addressing key improvement areas for reliable service delivery.
Dissecting the 0-Day Supply Chain Vulnerability in Argo CD
Explore the discovery and implications of a critical 0-day vulnerability in Argo CD, including attack methods, remediation steps, and its impact on the ecosystem.
Making Your Apps and Infrastructure Services Failure-Resilient with Dapr
Explore Dapr's role in enhancing microservices resilience, applying global policies for failure recovery across apps and infrastructure, regardless of deployment location or programming language.
Distributing Supply Chain Artifacts with OCI and ORAS Artifacts
Explore secure distribution of supply chain artifacts using OCI & ORAS Artifacts. Learn about managing artifact relationships, lifecycle management, and evolving registry capabilities for cloud-native environments.

Securing Web Services with Let's Encrypt and Cert Manager
Automate SSL/TLS certificate management for web services using Let's Encrypt and Cert Manager, enhancing security and simplifying deployment in cloud-native environments.
Securing Shopify's Software Supply Chain - Mitigating Supply Chain Attacks
Explore techniques for securing software supply chains, including cloud-based defenses, trust establishment, and malicious behavior detection, drawing from Shopify's experiences.
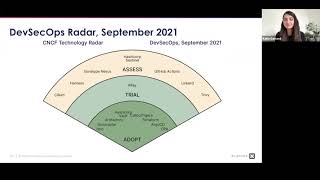
CNCF End User Technology Radar for DevSecOps - September 2021
Explore DevSecOps trends and recommendations from CNCF's End User Community. Gain insights on security solutions, micro-segmentation, and balancing security with developer experience in cloud-native environments.
Certs Magic - Exploring Cloud Native Security Certifications
Explore the world of cloud native certifications with expert Walid Shaari, gaining insights into career advancement and industry-recognized credentials.
Breaking ML Services: Finding Zero-Days in Azure Machine Learning
Uncover critical vulnerabilities in Azure Machine Learning, including credential leaks, information disclosure, and persistence techniques. Learn assessment methods for cloud-based MLaaS platforms and shared responsibility models.
Passwords: Policies, Securing, Cracking, and More
Explore password security essentials, from creating strong policies to understanding cracking techniques. Learn to secure passwords in AD and AAD, and discover why they remain crucial despite MFA adoption.
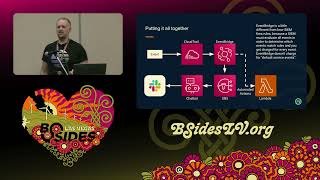
Big SIEM Energy at Micro-SIEM Cost - Building Custom Security Monitoring in AWS
Learn to build a cost-effective micro-SIEM for AWS using EventBridge, CloudTrail, SNS, and ChatBot. Discover how to tailor security monitoring to your specific needs and budget constraints.
Secure Containers and Workloads with Certificates in CI/CD Pipelines
Learn to enhance security in CI/CD pipelines by implementing certificate-based protection for containers and workloads, ensuring robust safeguards for cloud-native applications.
NVMe: New Vulnerabilities Made Easy - Exploiting Cloud Storage Protocols
Exploring pre-auth remote vulnerabilities in NVMe implementation, emphasizing the importance of SCA tools in production pipelines and showcasing discoveries in Linux kernel and NVIDIA.
Threat Model Report: Security Considerations for Hardening Declarative GitOps on Kubernetes with Argo CD
Explore security considerations for hardening Argo CD deployments in Kubernetes, focusing on mitigating misconfigurations and implementing best practices to enhance GitOps workflows.