Fantastic AWS Attacks and Where to Find Them
Explore AWS attack techniques and build effective cloud defenses using the ATT&CK framework. Learn to create and operationalize detections for enhanced AWS infrastructure security.
The Bucket List - Experiences Operating S3 Honeypots
Insights from operating S3 honeypots: Discover who's hunting for exposed buckets, their methods, and how to protect your AWS assets through monitoring and defensive strategies.
Building an Effective Intrusion Detection Program
Learn to build an effective intrusion detection program using affordable tools. Covers cloud apps, endpoints, network security monitoring, and crowdsourced incident response to catch breaches quickly.
Make Alerts Great Again
Strategies for creating effective, actionable security alerts: improving signal-to-noise ratio, standardizing definitions, and implementing self-service tools to enhance team efficiency and incident response.
The GCP Metadata API - Security Considerations, Vulnerabilities, and Remediations
Explore GCP Metadata API security: risks, attacks, defenses, and best practices. Learn about service accounts, Kubernetes, and Cloud Build implications for your organization's cloud infrastructure.
All Your Containers Are Belong to Us
Explore container orchestration security risks, focusing on exposed management nodes and APIs. Learn implications, recommendations, and see demonstrations of potential exploits in popular platforms.
The Secure Metamorphosis - Streaming Logs with Kafka and TLS
Explore Kafka's TLS configuration for secure, high-performance log streaming. Learn best practices, authentication methods, and troubleshooting techniques for a robust messaging system.
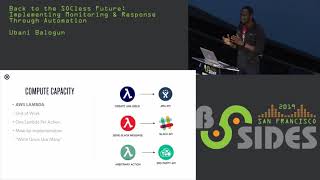
Back to the SOCless Future
Explore Twilio's journey towards automated security operations, featuring insights on scalable 24/7 monitoring and a serverless automation framework for effective threat response.
How to Lose a Container in 10 Minutes
Explore container security challenges, common deployment mistakes, and real-time vulnerabilities in cloud environments with practical examples and live demonstrations.
How to Kill an AWS Access Key
Learn to eliminate static AWS Access Keys using Security Token Service, SAML, and Identity Providers for enhanced cloud security and short-lived credentials.
Serverless Osquery Backend and Big Data Exploration
Explore serverless osquery backend deployment, scalability challenges, and large-scale data processing for enhanced intrusion detection and endpoint management.
Adventures in Vendor Security and Continuous Review
Explore innovative methods for continuous vendor security assessment in the cloud era, leveraging publicly available information to evaluate and monitor provider security postures.
Purple is the New Black - Modern Approaches to Application Security
Explore modern application security approaches combining defense, offense, automation, and continuous learning for various app types, including zero trust, supply chain, and microservices.
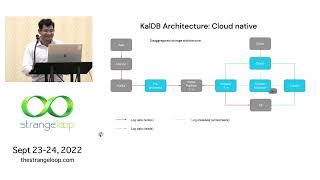
KalDB - A Cloud Native Log Search Platform
Explore KalDB, a cloud-native log search platform addressing Elasticsearch limitations. Learn about its architecture, real-time visibility, automatic field conflict handling, and cost-saving techniques.
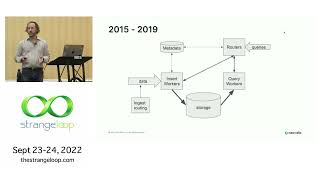
The Evolution of a Planetary-scale Distributed Database
Explore the evolution of New Relic's telemetry database, from its inception to a globally distributed system. Learn about architectural challenges, solutions, and insights into building large-scale distributed systems.
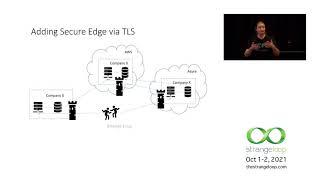
Injecting Security at the Cloud Edge
Explore secure hybrid cloud deployments using Apache Traffic Server, Athenz, and Waflz. Learn options for Secure Edge integration, policy enforcement, and lessons from real-world implementation at Yahoo.
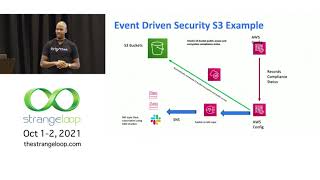
Why Security Is the Biggest Benefit of Using the Cloud
Explore how cloud migration enhances application and data security at scale, discussing modern challenges, event-driven security, and AWS guardrails for improved organizational security posture.
CloudLeak - DNN Model Extractions from Commercial MLaaS Platforms
Explore DNN model extraction vulnerabilities in cloud-based machine learning services, examining security risks and potential countermeasures for MLaaS platforms.
ChaosDB - How We Hacked Databases of Thousands of Azure Customers
Uncover the critical ChaosDB vulnerability in Azure Cosmos DB, allowing unauthorized access to thousands of customer databases. Learn about the discovery, exploitation, and implications of this unprecedented cloud security flaw.
Practical Attacks Against Attribute-based Encryption
Explore practical attacks on attribute-based encryption, examining vulnerabilities in multi-authority schemes and their implications for cloud security and IoT applications.
Mobius Band - Explore Hyper-V Attack Interface through Vulnerabilities Internals
Explore Hyper-V vulnerabilities and attack interfaces, focusing on 3 RCE vulnerabilities in Microsoft's virtualization solution. Gain insights into cloud security and potential risks.